Mallory
← Back to News
financial-sector-threatthird-party-vendor-breachinitial-access-methodlateral-movement-method

European Bank Breached via Third-Party Gateway; WSUS Exploit Attempt Contained

Sector Threat Intelligence · 2 sources · Updated 1mo ago · First seen Oct 14, 2026
European Bank Breached via Third-Party Gateway; WSUS Exploit Attempt Contained

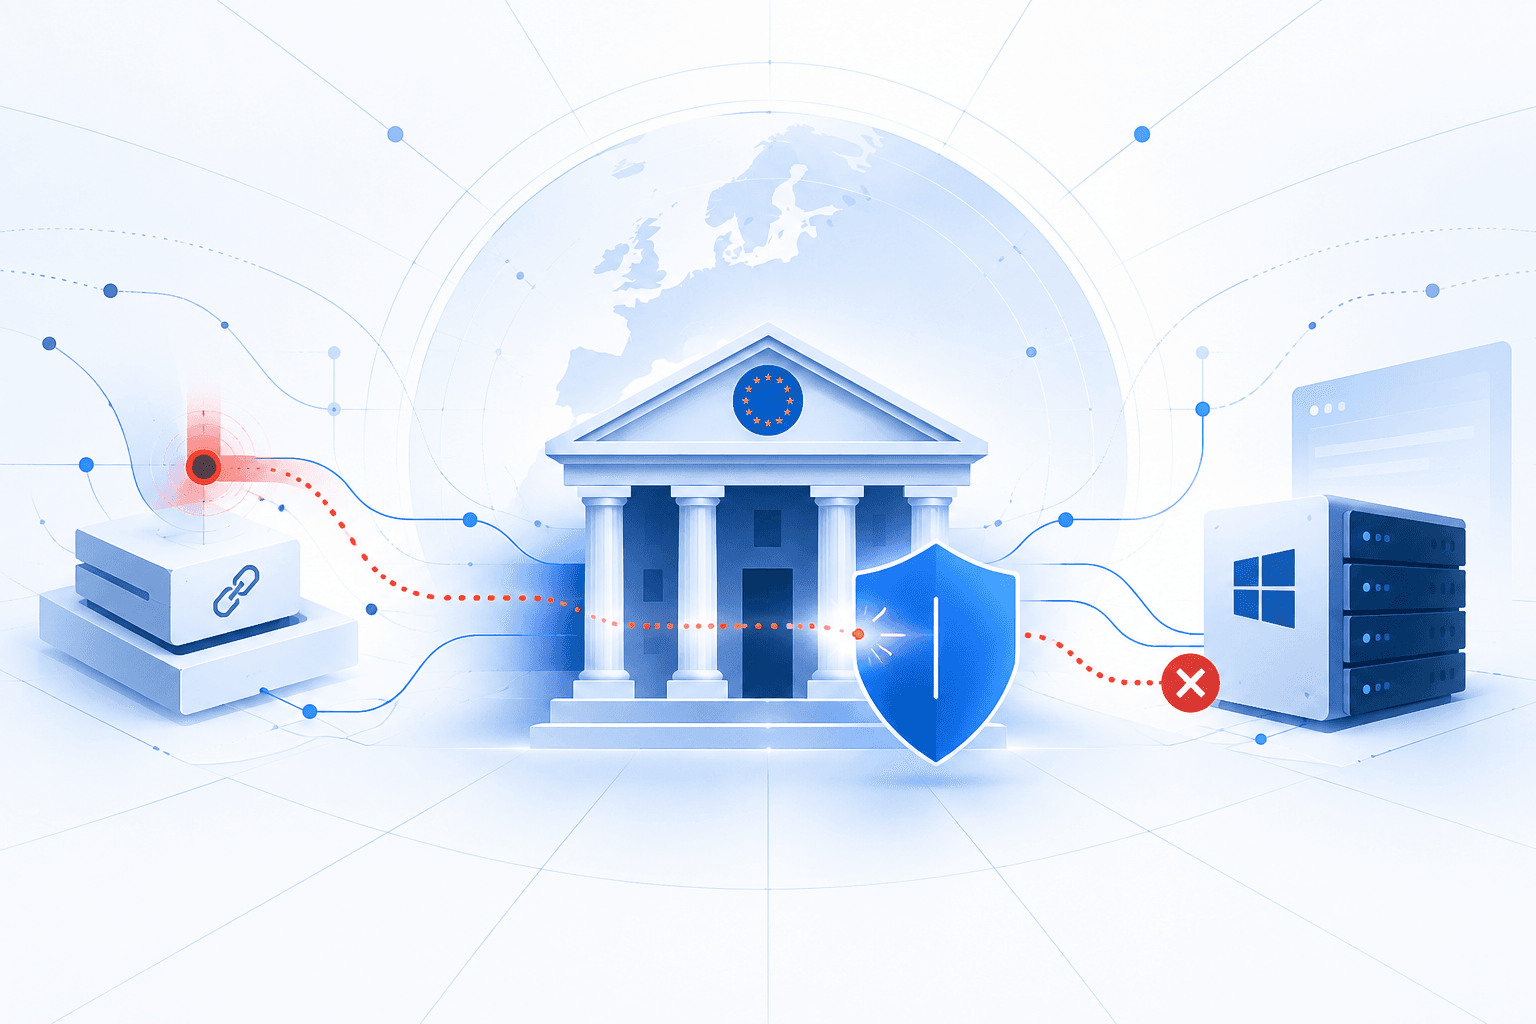
An attacker breached an unnamed European bank through a third-party-managed gateway with weak authentication, using compromised credentials to reach internal systems, according to reporting from Palo Alto Networks Unit 42 and Cybersecurity News. Over several months, the intruder scanned thousands of systems, attempted to guess administrator passwords, and accessed internal documentation, exposing a significant third-party access-control weakness.

The attacker subsequently attempted remote code execution against Windows Server Update Services (WSUS) on the bank’s central configuration management server. Cortex XDR detected and contained that attempt before it established persistent access or enabled further spread. Responders found no additional attacker presence or persistent backdoors, rotated compromised credentials, and expanded security monitoring. The reporting did not disclose the targeted CVE, identify malware, or confirm theft of customer banking records. The incident underscores the need to strengthen authentication on vendor-managed gateways and monitor third-party access for internal reconnaissance.
Who's targeting your sector?See the actors and campaigns active against you right now.
See sector threats
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

9 events · Oct 13, 2026
  1. Reported Oct 14, 20261mo ago

    Bank expands security monitoring and incident response support

    Following the incident, the bank expanded its Cortex XDR and Cortex XSIAM coverage and its incident response support.

    Attackers Breach European Bank Through Third-Party Gateway and Target WSUS Server
  2. Reported Oct 14, 20261mo ago

    Bank reviews exposed documentation and rotates compromised credentials

    Bank leaders reviewed the documentation exposed during the intrusion and rotated all compromised credentials.

    Attackers Breach European Bank Through Third-Party Gateway and Target WSUS Server
  3. Reported Oct 14, 20261mo ago

    Follow-up investigation finds no additional footholds or persistent backdoors

    Responders reviewed endpoint records across thousands of systems and logs from dozens of Windows and Linux servers. The follow-up investigation found no additional attacker presence or persistent backdoors.

    Attackers Breach European Bank Through Third-Party Gateway and Target WSUS Server
  4. Reported Oct 14, 20261mo ago

    Cortex XDR detects and contains the code execution attempt

    Cortex XDR detected the unauthorized code execution attempt and contained the threat before the attacker established persistent access or spread further. After detecting unusual activity on its central IT system, the bank's security team uncovered unauthorized VPN access attempts spanning several months.

    Attackers Breach European Bank Through Third-Party Gateway and Target WSUS Server
  5. Reported Oct 14, 20261mo ago

    Attacker attempts WSUS exploitation on central management server

    The attacker attempted to exploit a remote code execution vulnerability in Windows Server Update Services on the bank's central configuration management server, which handled software distribution. Unit 42 did not disclose the targeted vulnerability's CVE identifier.

    Attackers Breach European Bank Through Third-Party Gateway and Target WSUS Server
  6. Reported Oct 14, 20261mo ago

    Attacker accesses internal documentation

    The attacker used automated web requests to scrape internal pages and attachments and searched operational and network shares. These activities exposed internal documentation, but the report did not quantify stolen data or confirm theft of customer banking records.

    Attackers Breach European Bank Through Third-Party Gateway and Target WSUS Server
  7. Reported Oct 14, 20261mo ago

    Intruder scans thousands of systems and targets administrator credentials

    The attacker repeatedly scanned internal hosts and networks across multiple protocols, interacting with thousands of systems. Over several months, the intruder also conducted password-guessing campaigns focused on administrator accounts.

    Attackers Breach European Bank Through Third-Party Gateway and Target WSUS Server
  8. Reported Oct 14, 20261mo ago

    Attacker breaches European bank through third-party gateway

    An attacker used compromised credentials to enter an unnamed European bank through an externally managed gateway that did not enforce strict authentication. Investigators identified weak gateway authentication as the entry point rather than a disclosed software exploit.

    Attackers Breach European Bank Through Third-Party Gateway and Target WSUS Server
  9. Oct 13, 20261mo ago

    Unit 42 investigation into the bank intrusion is published

    An investigation describing Unit 42's findings was published, detailing the third-party gateway intrusion and the contained WSUS exploitation attempt. The report characterized the attacker as opportunistic and did not identify the gateway vendor, malware, or targeted CVE.

    Attackers Breach European Bank Through Third-Party Gateway and Target WSUS Server
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Affected products

1 linked
Windows Server Update Services
Do you run this?See the adversaries and campaigns active against your sector right now, ranked by what they're exploiting.
See Your Sector's Threats
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.