
Loading story…
Attackers impersonated Claude, ChatGPT/Codex and Copilot to distribute malware, steal browser sessions and phish business accounts through deceptive AI-tool installation and advertising workflows. ANY.RUN linked 1,258 public sandbox analyses from April 15 to October 5, 2026, to these campaigns; Claude and ChatGPT/Codex branding accounted for 81% of the analyses, and at least 45% involved prompts to paste and execute commands. Lures targeted developers, marketing teams and other employees through counterfeit command-line installation instructions, ClickFix download pages, malicious shared conversations or artifacts on legitimate AI platforms, trojanized installers, and fake AI advertising invitations, including Browser-in-the-Browser phishing.
Reported payloads included Aura Stealer, MacSync Stealer, AsyncRAT, Quasar RAT and HijackLoader. US submitters ranked second overall and first in two major campaign groups, but sandbox submission statistics do not establish victim counts or geographic infection rates; the reporting identified no named threat actor or CVE. Recommended defenses include providing approved AI software sources, restricting risky command execution, and detecting recurring command patterns, backend paths and scheduled tasks rather than relying primarily on rapidly changing domains. Supplied indicators require validation before operational use because secondary reporting contains conflicting statements about external verification.
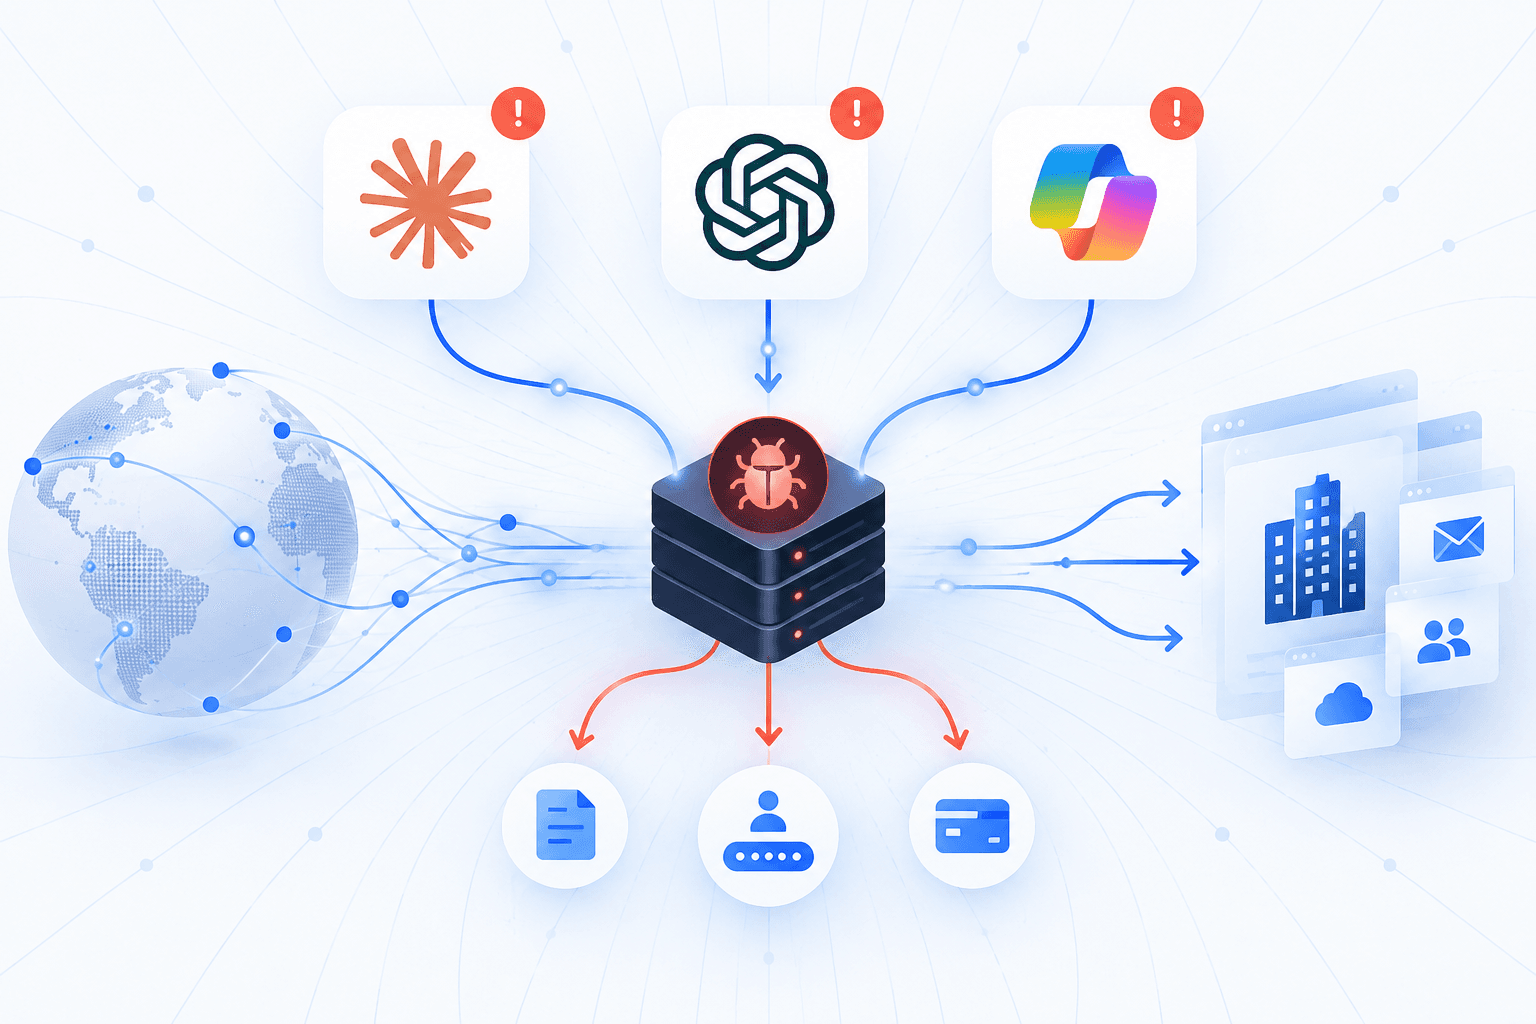
Get the infrastructure and lures behind it.
11 events from the most recent confirmed update back to the earliest known activity.
On October 14, 2026, ANY.RUN published research covering public sandbox analyses collected between April 15 and October 5, 2026. The report detailed malicious installation commands, ClickFix pages, shared AI-content lures, trojanized installers, and advertising phishing, while cautioning that submission statistics did not establish victim counts.
The last complete InstallFix chain observed by ANY.RUN ran on September 16, 2026. Observed chains used counterfeit CLI installation instructions to execute PowerShell downloads and retrieve a stealer from GitHub; an Ollama variant also installed genuine Ollama software.
September 2026 lures redirected users from shared ChatGPT chats and custom GPTs to openai-backup[.]one or Google Sites pages presenting fake verification checks. Related chains shared an operator key and Google Sites naming pattern, and one silently installed a MouseJiggleStudio MSI package.
Between August 24 and September 3, 2026, twelve analyses requested paripassuventures[.]com, with eight receiving payloads detected as MacSync Stealer. A Google-advertised claude.ai artifact impersonating Download Claude directed macOS users to execute a curl command containing an encoded URL to that host.
ANY.RUN recorded 57 analyses from July 21 through September 18, 2026, involving fake Claude, Gemini, Perplexity, and Manus advertising invitations. The lures targeted marketing personnel with browser-in-the-browser windows impersonating Google sign-in.
A counterfeit AI budgeting application on budgetforge[.]ai used an installer-registration pattern also found in the trojanized Claude installer campaign. The BudgetForge variant used a different brand label and GitHub account.
The campaign operated from April 2026, using counterfeit download pages to induce users to paste commands into PowerShell. Observed chains used mshta.exe to retrieve an obfuscated HTA and deliver stealer payloads rather than a legitimate installer.
A fake Cloudflare-check lure on claudedev[.]net led to a loader chain assessed as likely HijackLoader. The assessment relied on command-and-control detections in sandbox sessions sharing the download host.
ANY.RUN identified AsyncRAT in eight analyses involving Copilot-named files and Quasar RAT in a file named grok.exe. These samples formed part of a broader set of 220 analyses of suspicious or malicious files bearing AI-product names.
A counterfeit claude-code.exe contained Aura Stealer and communicated with sys-tools[.]cfd for command-and-control and exfiltration.
The counterfeit site claude-ai[.]us distributed Claude_x64-setup.exe through GitHub, displaying a setup window and launching a genuine Claude installer as a decoy. Its malicious chain created the mseupdate scheduled task, ran Edge headlessly with remote debugging, and sent cookies, extension data, and a dataset labeled sendkeys to nucleflowers[.]xyz.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 44 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
3 references tracked. Mallory keeps watching after this page renders.
darkreading.com
Open sourceany.run
Open sourcecyberveille.ch
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Threat actors are abusing interest in AI developer tools by impersonating installers and setup guides to trick users into executing malware. Fake installation-guide pages for Anthropic’s **Claude Code** were promoted via **Google Ads** to rank highly for searches like “Claude Code install/CLI,” leading Windows and macOS users to run copy-pasted commands in an **InstallFix** campaign (a variant of **ClickFix**) that ultimately deployed **Amatera** (an **ACR Stealer**-based MaaS infostealer). Push Security reported the malware steals browser-stored credentials, cookies, session tokens, and system information, and the infrastructure used legitimate hosting/CDN services (e.g., *Squarespace*, *Cloudflare Pages*, *Tencent EdgeOne*) to reduce suspicion. In a related AI-tool impersonation theme, JFrog identified a malicious **npm** package, `@openclaw-ai/openclawai`, posing as an **OpenClaw** installer that targets macOS users to steal credentials and establish persistent remote access. The package uses a `postinstall` hook to reinstall itself globally and registers a CLI via the `bin` field pointing to `scripts/setup.js`, which presents a fake installer UI and then prompts for the user’s system password via a bogus Keychain/iCloud authorization flow. The malware (self-identified as **GhostLoader**) was reported to collect browser data, crypto wallets, SSH keys, Apple Keychain databases, and iMessage history, while also deploying a **RAT** with **SOCKS5 proxy** capability and “live browser session cloning,” indicating a blend of credential theft and long-term access objectives.
Aug 21, 2026
Huntress documented malware-delivery campaigns that weaponized public, indexable content on trusted AI platforms—including Claude, ChatGPT, and Grok—without exploiting vulnerabilities in those services. In one campaign, Bing malvertising directed users searching for Claude Desktop to a fraudulent Claude Artifact hosted on the legitimate `claude.ai` domain, affecting more than 29 organizations and delivering the SectopRAT remote-access trojan. Other campaigns used a fake Apple Support installation guide on `claude.ai/share` to deploy the MacSync macOS malware and SEO-poisoned ChatGPT and Grok conversations to distribute the AMOS infostealer. The attacks exploit confidence in recognizable domains, prominent search results, and copied terminal commands; organizations should require official software download channels, treat AI-supplied commands as untrusted, restrict clipboard-triggered script execution, enforce application allowlisting, and monitor for scheduled-task creation and antivirus-exclusion changes.
Sep 21, 2026
Attackers are targeting macOS users with fake AI tool downloads promoted through **Google Ads** and public **Claude.ai** shared chats. Victims searching for terms such as “Claude mac download” are shown sponsored results that appear to reference the legitimate `claude.ai` domain, but the links redirect to shared chats containing bogus installation instructions. The lures present themselves as official guidance for running Claude-related tools on Mac, sometimes even masquerading as Apple Support content, and tell users to paste commands into Terminal that instead fetch and execute malware. Researchers said the campaign is active and uses rotating malicious chat pages and infrastructure to evade disruption. Observed payloads include Mac-focused infostealers with behavior consistent with **AMOS** and **Amatera/MacSync-style** theft, including collection of browser credentials, cookies, and **Keychain** data. The activity reflects a broader trend of threat actors disguising malware as AI agents and developer tools to exploit demand for generative AI software on macOS systems.
Jun 29, 2026