Microsoft Active Directory and AD FS Bypass Flaws Prompt Patching Guidance
Vulnerability Disclosure · 2 sources · Updated 16d ago · First seen Oct 14, 2026
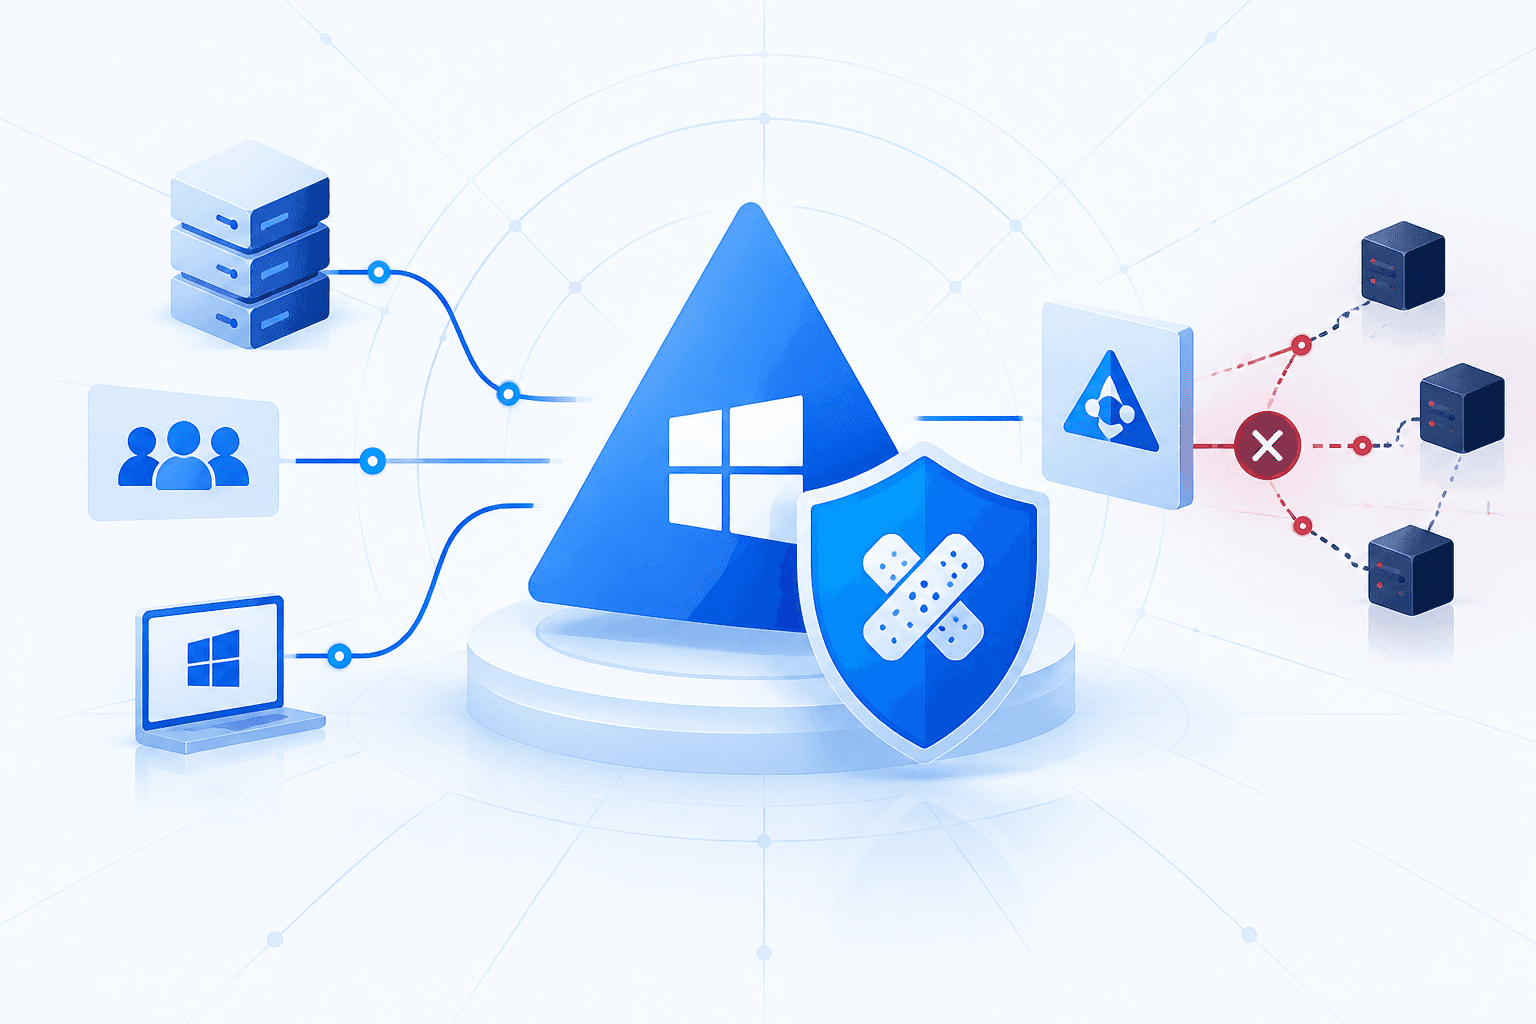
Microsoft has reportedly released fixes for three Active Directory security-feature bypass vulnerabilities: CVE-2026-69982, CVE-2026-96252, and CVE-2026-108131. The flaws could allow remote attackers to circumvent protections in Windows domain environments, though they do not necessarily grant full server control. CSIRT Panamá describes CVE-2026-108131 as an authentication-bypass and spoofing flaw in Active Directory Federation Services (AD FS), assigning it a CVSS 3.1 score of 7.5. According to the advisory, an unauthenticated remote attacker could impersonate trusted users or services without user interaction, primarily compromising integrity. Those technical details and the advisory’s update identifiers have not been independently verified.
Administrators should confirm affected products and fixes through Microsoft’s Security Update Guide, prioritize Internet-accessible AD FS deployments, apply relevant updates, and verify installation. Recommended defensive measures include reducing federation-service exposure, restricting access to domain controllers, and reviewing suspicious token issuance and federation trust changes. Active exploitation is not established by the supplied reporting: CSIRT Panamá’s advisory contradicts itself, stating both that Microsoft reports no exploitation and that active-exploitation reports exist, while the separate report says accessible Microsoft update information provides no evidence of exploitation.