CikaBika Bot RAT Uses Discord for Control and Ngrok for Data Theft
Malware Intelligence · 2 sources · Updated 13d ago · First seen Oct 15, 2026
Darktrace uncovered a campaign deploying CikaBika Bot, a Rust-based remote access trojan that uses Discord for command and control on compromised Windows systems. A business-proposal disk image contains a disguised Windows shortcut and a legitimate-looking PDF; opening the shortcut initiates hidden PowerShell execution and extracts a Nim-based loader. The deployment chain attempts to bypass Windows User Account Control and place a malicious DLL in Microsoft Edge’s protected installation directory, potentially enabling DLL search-order hijacking. Researchers did not establish that Edge successfully loaded the DLL. Initial delivery remains unconfirmed, although the document-themed lure suggests phishing.
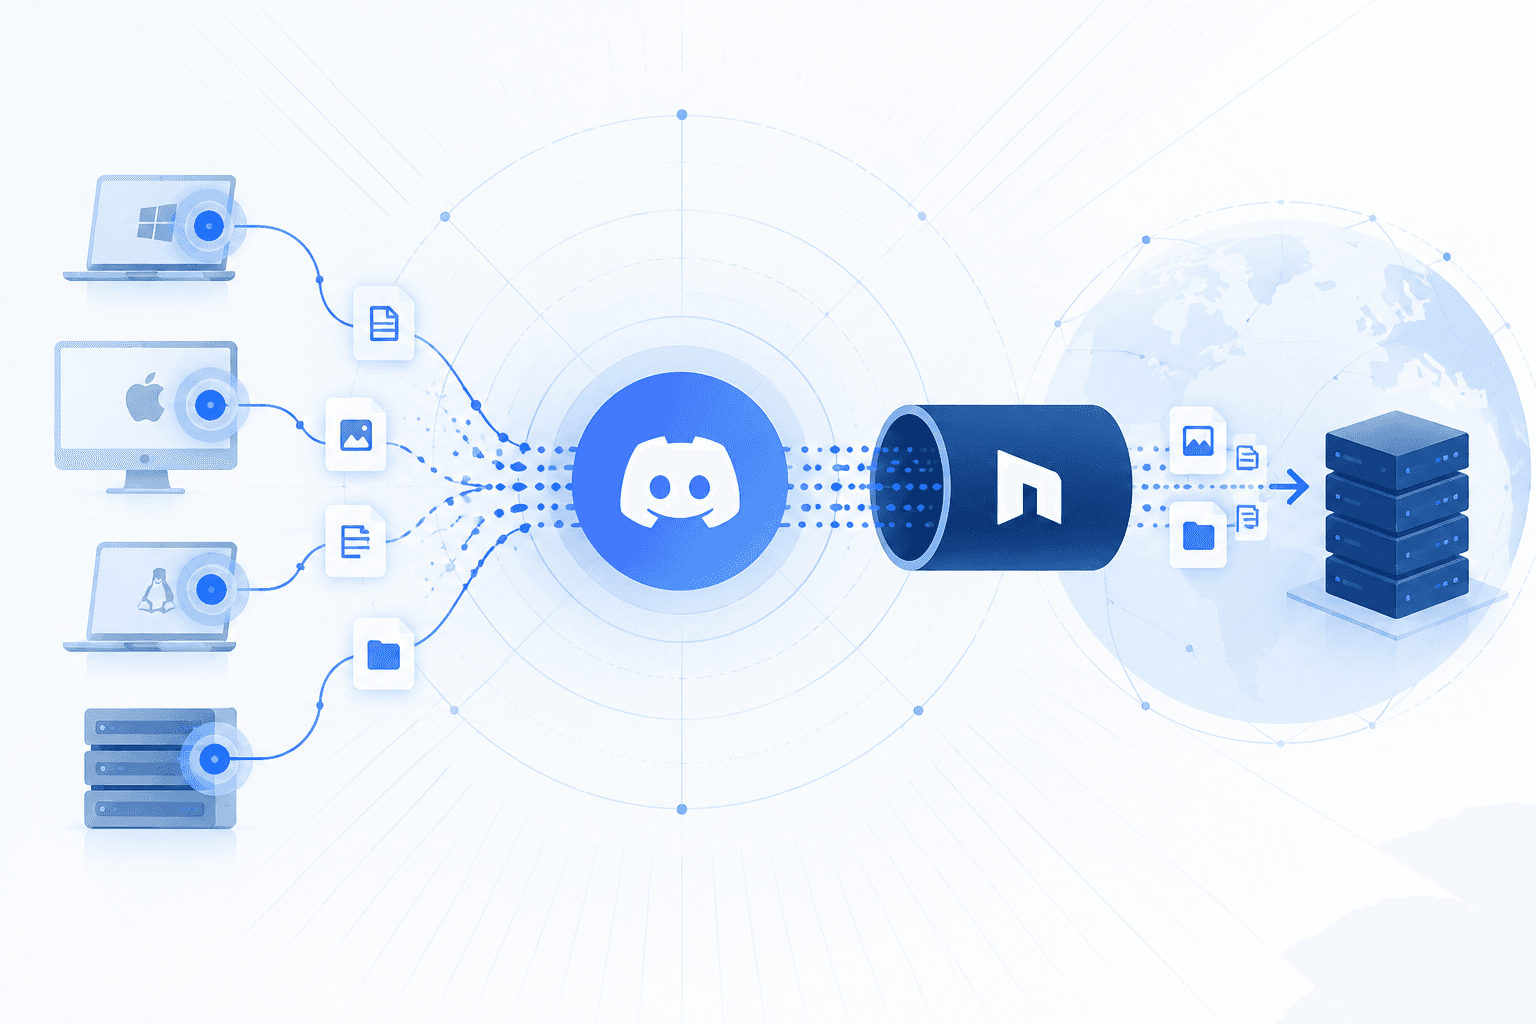
Once running, CikaBika Bot collects system information and enables remote command execution, process management, file transfers, screenshots, camera access, and screen streaming. Attackers can also compress victim directories into ZIP archives and exfiltrate them through Ngrok, providing a transfer channel alongside Discord-based control. Defenders should prioritize detection of document-lure shortcuts launching hidden PowerShell, unexpected DLL writes to Edge’s installation directory, and unauthorized Discord or Ngrok traffic from endpoints.