Researchers Find Indirect Prompt Injection Attempts in Website HTTP Headers
Emerging Technology Risk · 2 sources · Updated 9d ago · First seen Oct 15, 2026
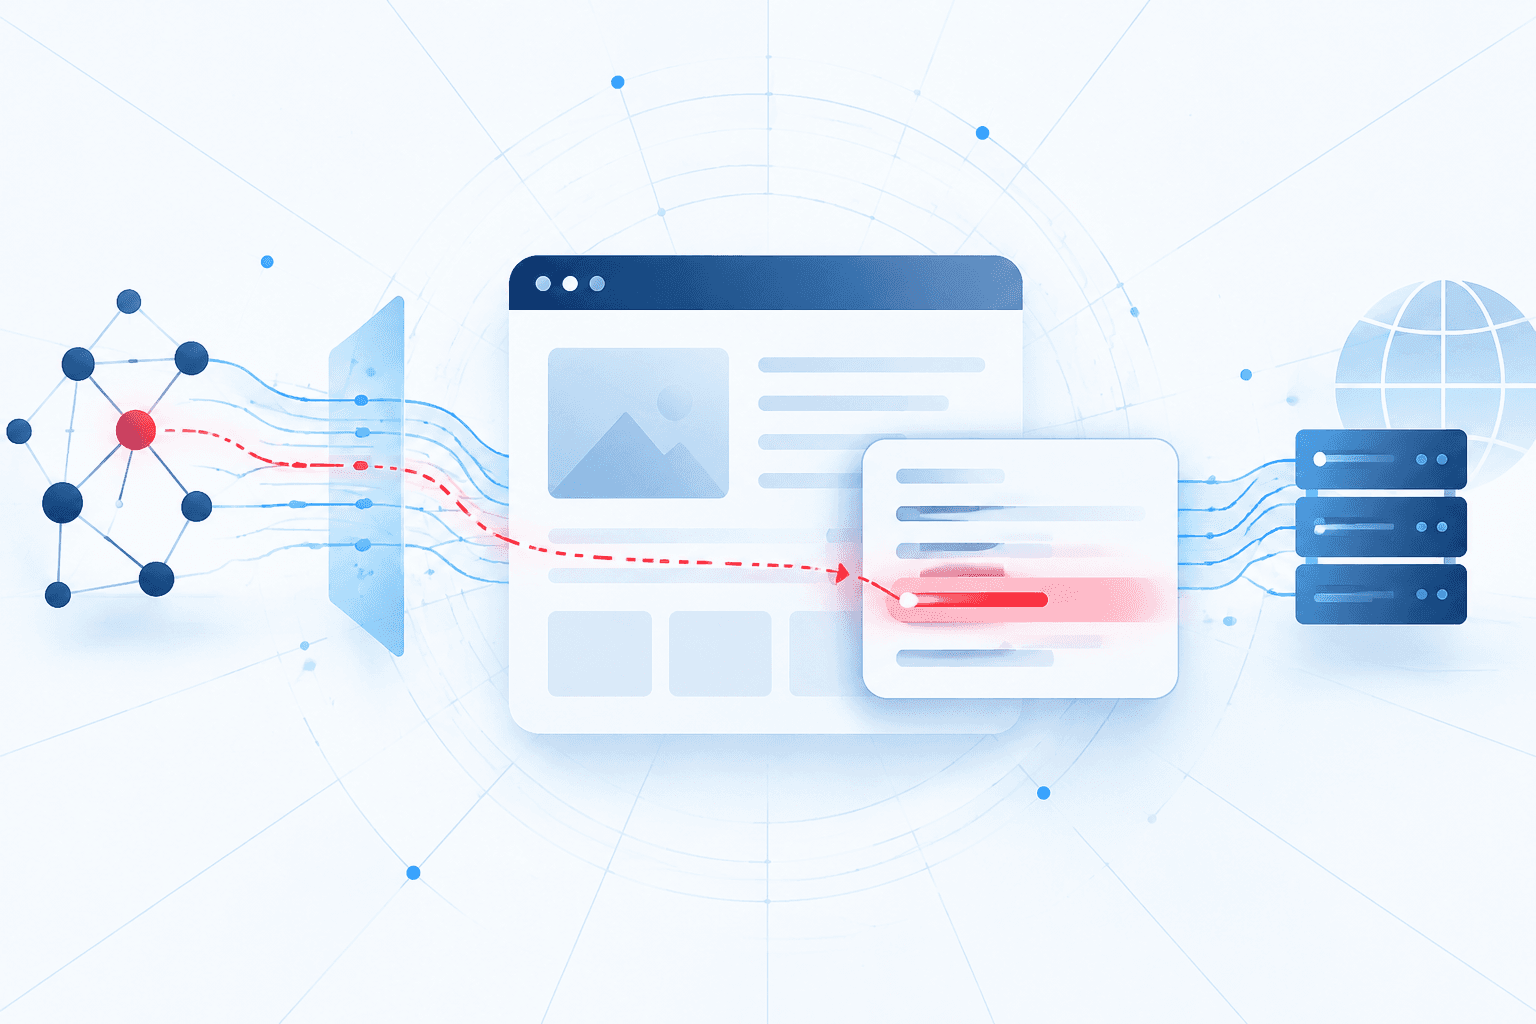
Signals Corps identified 30 websites attempting indirect prompt injection through HTTP response headers after analyzing 217 million page responses from Common Crawl. Nearly 8,000 websites carried AI-oriented header messages, most of which were harmless navigation pointers. The injection attempts ranged from pranks to messages potentially designed to trigger Claude’s refusal behavior or influence AI-powered hiring screening.
The researchers assessed the likelihood of anyone actually being affected as extremely low: exposure depends on whether an AI agent’s tools retrieve response headers and pass them to the model. The findings highlight metadata as another route for attacker-controlled instructions to reach agents. Recommended safeguards include treating external content, metadata and redirects as untrusted, allowlisting permitted metadata, requiring approval for Model Context Protocol (MCP) connections, and independently validating proposed actions outside the model.