Claude Code Desktop Preview Flaw Let Malicious HTML Steal Developer Credentials
Emerging Technology Risk · 3 sources · Updated 20d ago · First seen Aug 17, 2026
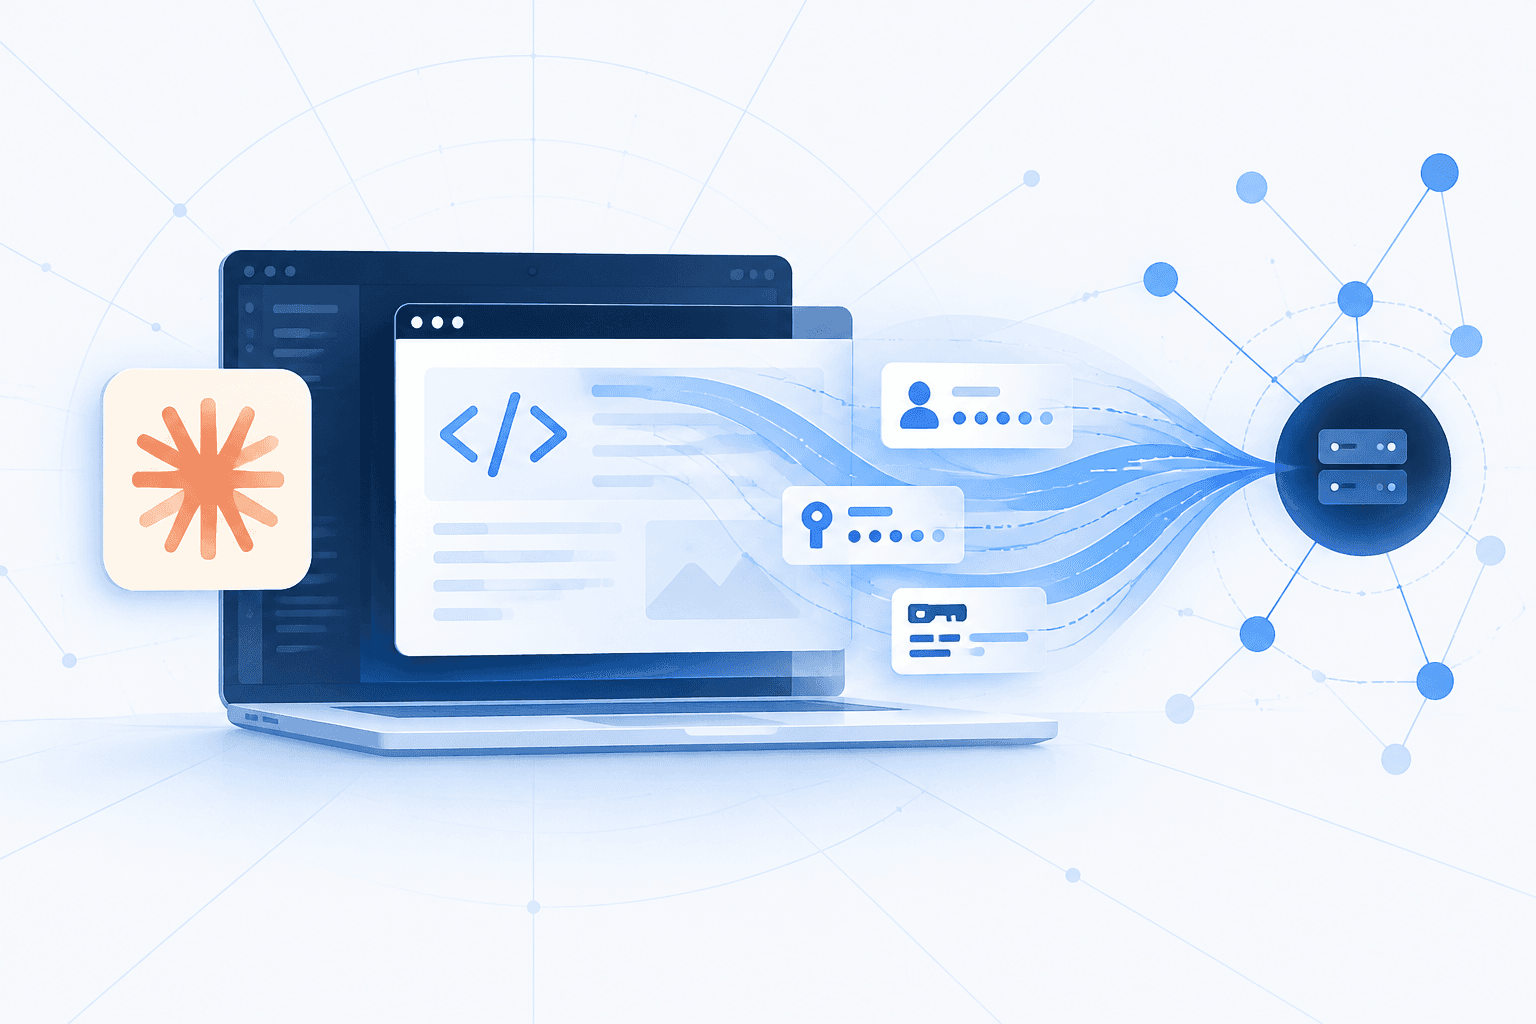
Noma Labs discovered SneakPeek, a high-severity vulnerability in Anthropic’s Claude Code Desktop preview pane that could allow malicious HTML to execute JavaScript without a separate permission prompt and exfiltrate local credentials and private keys. The flaw received a CVSS v4.0 score of 8.7. Researchers demonstrated an attack using a repository containing a malicious HTML code coverage report, which executed when a developer asked Claude to review or edit it.
Anthropic’s initial patch was bypassed using Web Workers, requiring additional fixes. Noma Labs reported that the remaining issues were resolved in Claude Desktop version 1.30096.1 and later, distributed through automatic updates on August 17, 2026. Organizations using Claude Code Desktop should verify that developer installations meet that fixed-version baseline, particularly where repositories contain untrusted HTML artifacts. A CVE assignment and GitHub Advisory publication were still pending at the time of the researchers’ report.