Supply-Chain Compromise Injects Malware into Some Rank Math SEO PRO Downloads
Supply Chain Risk · 9 sources · Updated 8d ago · First seen Oct 17, 2026
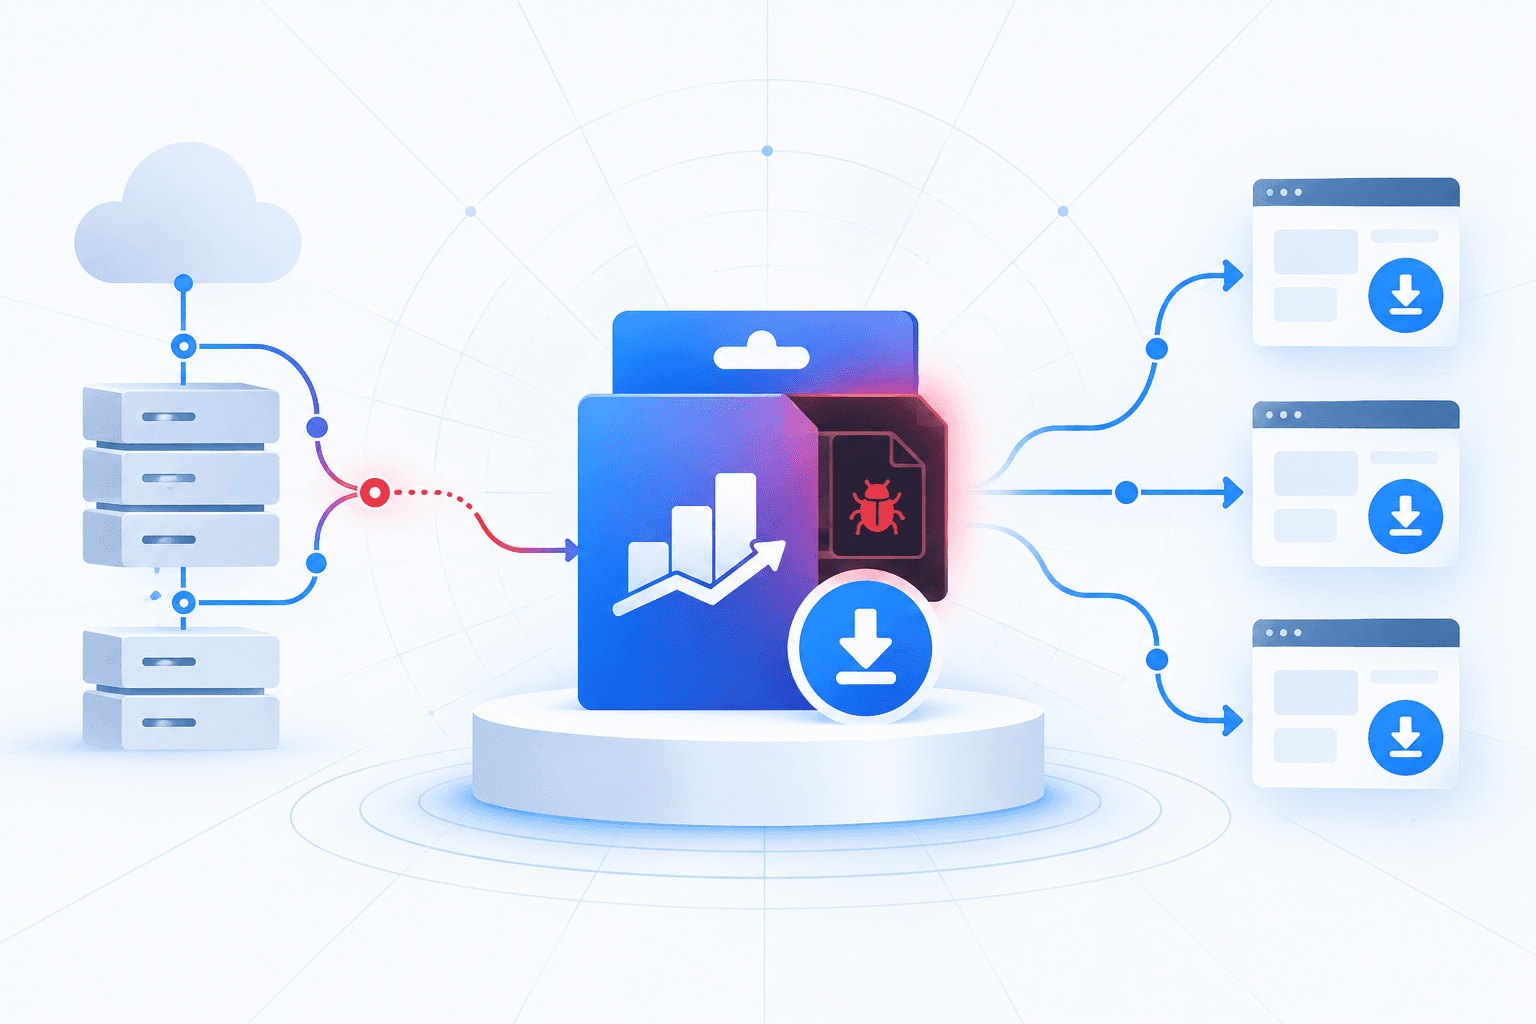
A supply-chain compromise affected some Rank Math SEO PRO 3.0.123 packages downloaded or installed through updates between October 15, 2026, at 20:02 UTC and October 16 at 07:12 UTC. Wordfence reported the incident as CVE-2026-111862, with a critical CVSS score of 9.8. Version 3.0.123 alone does not establish compromise; exposure depends on whether a site received and activated an affected package. The malware could maintain persistent access, recreate hidden backdoors, and expose credentials and other secrets accessible to the web server.
Rank Math removed the affected files and released clean version 3.0.124, but upgrading alone does not eliminate established persistence, including malicious files, accounts, or scheduled tasks created elsewhere. Sites that activated an affected package should be treated as compromised. Administrators should restore a verified clean pre-incident backup or perform comprehensive manual cleanup, replace potentially exposed credentials and secrets, and monitor for reinfection.