FirstVDS Customer Data Stolen Through VMmanager 6 Vulnerability
Active Exploitation · 3 sources · Updated 15d ago · First seen Oct 19, 2026
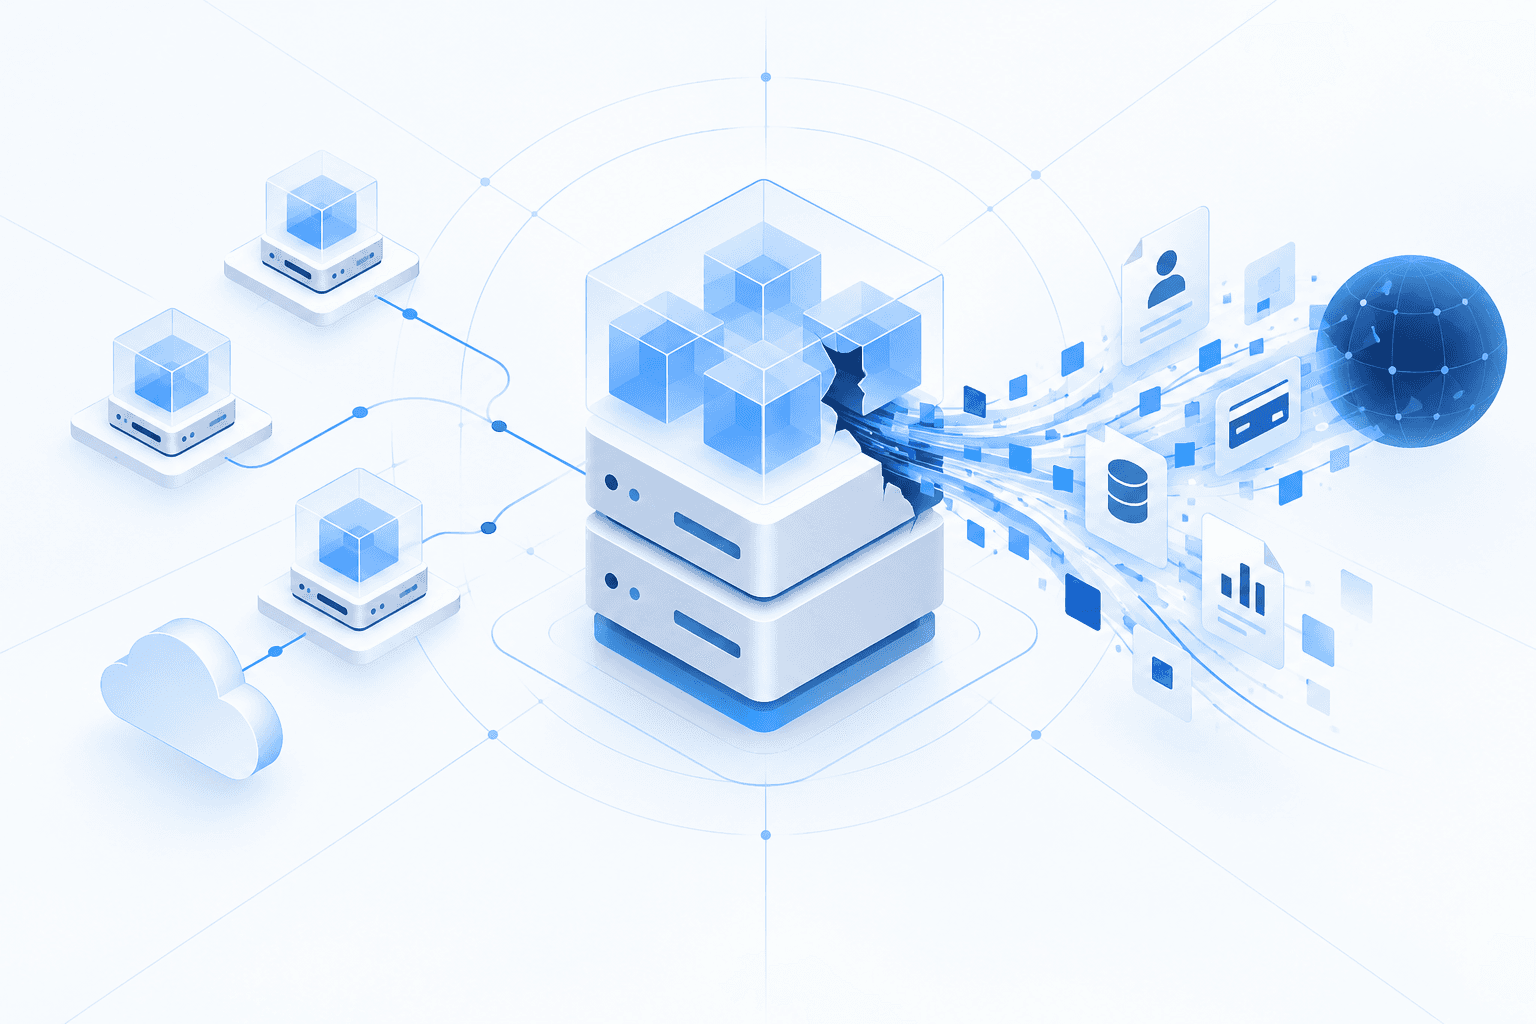
Attackers exploited a vulnerability in ISPsystem’s VMmanager 6 virtualization management platform on October 17 to steal customer data from Russian hosting provider FirstVDS. A data stealer on affected virtualization hosts mounted customers’ virtual-server disks in read-only mode and copied passwords, cloud credentials, configuration files, cryptocurrency-wallet data and other files to an attacker-controlled server. The theft did not require execution inside guest systems or disrupt virtual-server operations. FirstVDS said only part of its infrastructure was affected but did not disclose how many customers or servers were compromised.
FirstVDS disabled external access to the vulnerable management system, blocked communications with the attackers’ server and notified affected customers. The provider advised those customers to assume all server data had been copied, rotate or revoke exposed credentials, secure cryptocurrency funds and investigate potential follow-on access. ISPsystem released patches, but FirstVDS reported that the vulnerability remained incompletely fixed and said management-interface access should remain restricted pending further updates.