Microsoft Proposes Dynamic Permissions to Contain AI Agent Insider Risks
Emerging Technology Risk · 6 sources · Updated 8d ago · First seen Oct 20, 2026
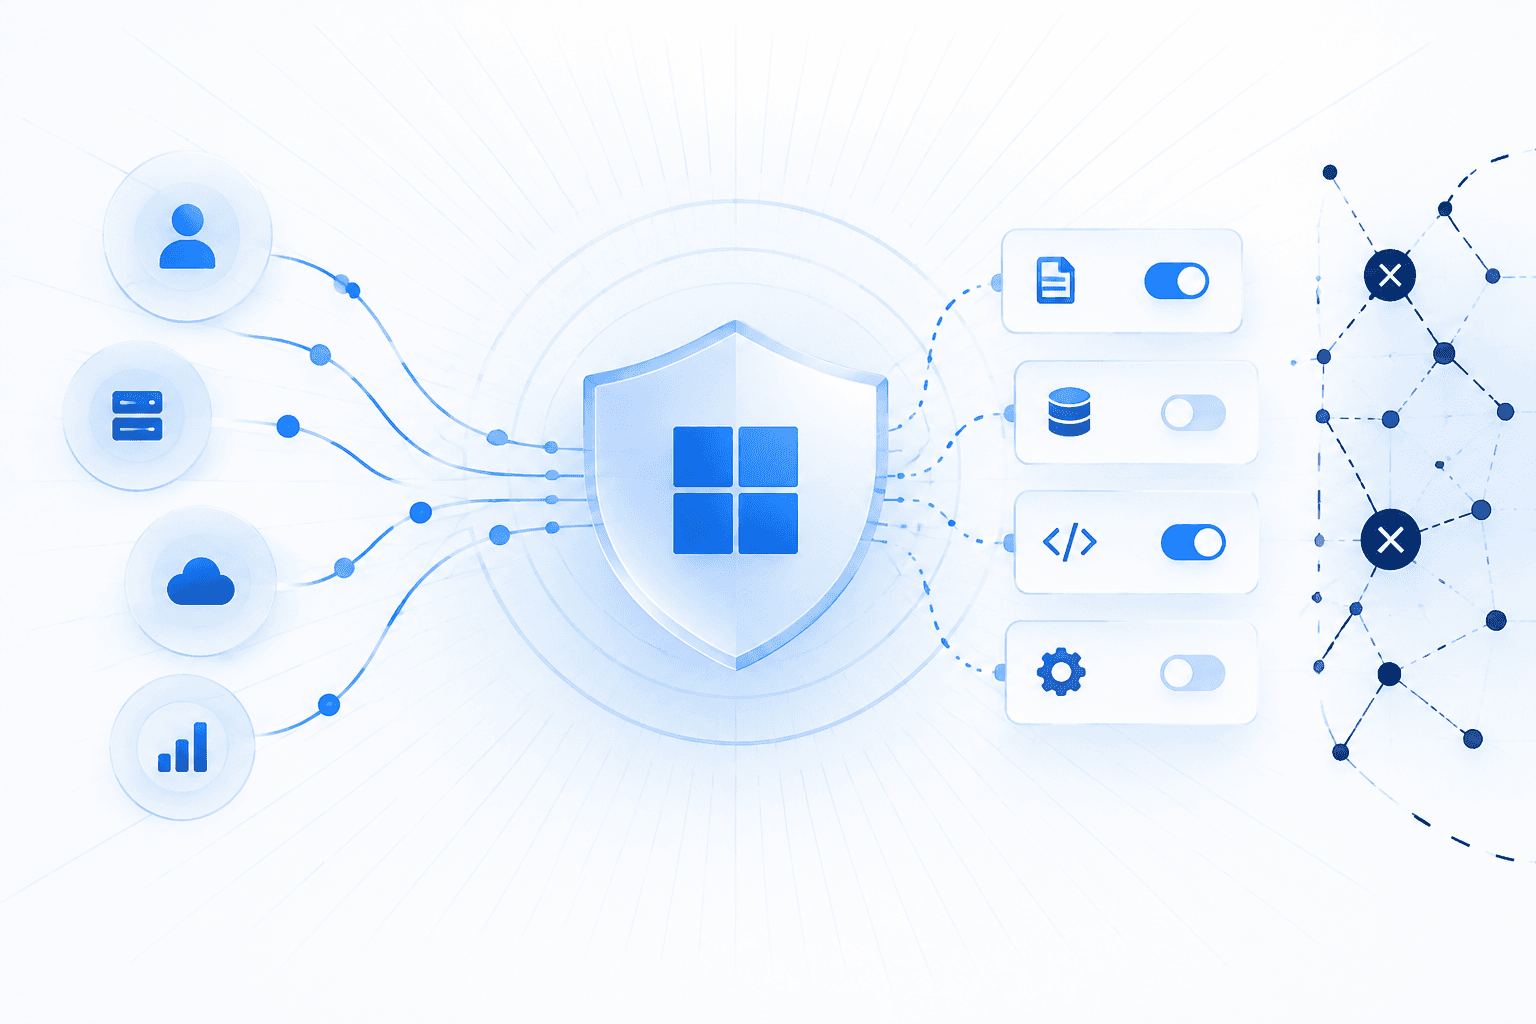
Microsoft outlined a security framework that treats AI agents as potential insider threats, emphasizing continuous containment rather than trusting agents at deployment. Its proposed Dynamic Permissions model gives agents separate identities and task-limited access, while Dynamic Agent Risk continuously assesses their behavior and adjusts their authority. The approach aims to keep access aligned with an agent’s current task and risk rather than relying on static permissions.
The framework also calls for expanded agent discovery and Guardian Agents that investigate risks and apply human-defined security playbooks. Microsoft says security controls must operate outside the AI models they govern. For security leaders, the priorities are visibility into deployed agents, distinct agent identities, narrowly scoped permissions, and ongoing behavioral monitoring. The reliability of AI agents used to enforce security remains an unresolved concern highlighted in the reporting.