FortiSIEM gRPC Flaw Enables Unauthenticated File Writes and Remote Code Execution
Patch & Detection Intelligence · 12 sources · Updated 20d ago · First seen Oct 20, 2026
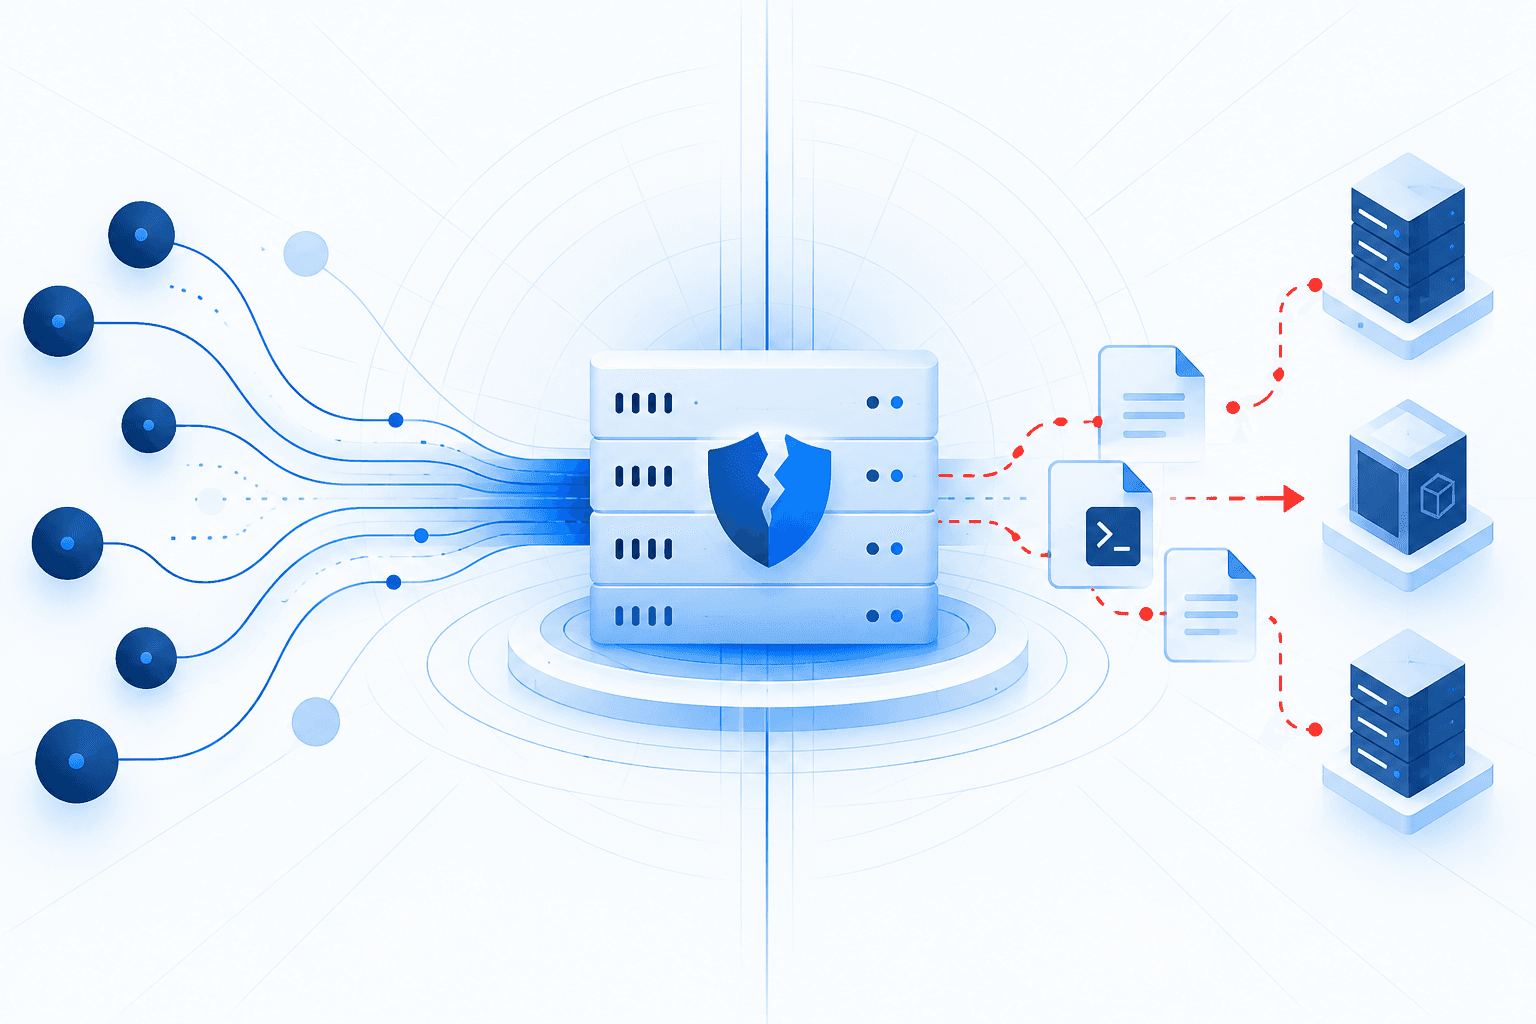
Horizon3 disclosed technical details and proof-of-concept code for CVE-2026-106173, a critical Fortinet FortiSIEM vulnerability that enables unauthenticated arbitrary file writes through a gRPC service on TCP port 27918. Directory traversal and embedded null bytes in attacker-controlled request metadata bypass server-generated filename restrictions. Attackers can achieve remote code execution by overwriting /opt/charting/redishb.sh, which a cron job executes every 60 seconds. Fortinet published an advisory on October 13, 2026.
The supplied reporting does not identify affected versions, patch details, or evidence of active exploitation. Defenders should consult Fortinet’s advisory to determine exposure and remediation requirements, and restrict access to the gRPC service where feasible. Horizon3 found no application logs that explicitly identify exploitation and recommended inspecting relevant files for suspicious modification timestamps, making file-integrity checks particularly important.