Researcher Reports 333 Tor Exit Nodes Hijacking SSH Traffic to Steal Credentials
Attack Tradecraft · 12 sources · Updated 8h ago · First seen Oct 20, 2026
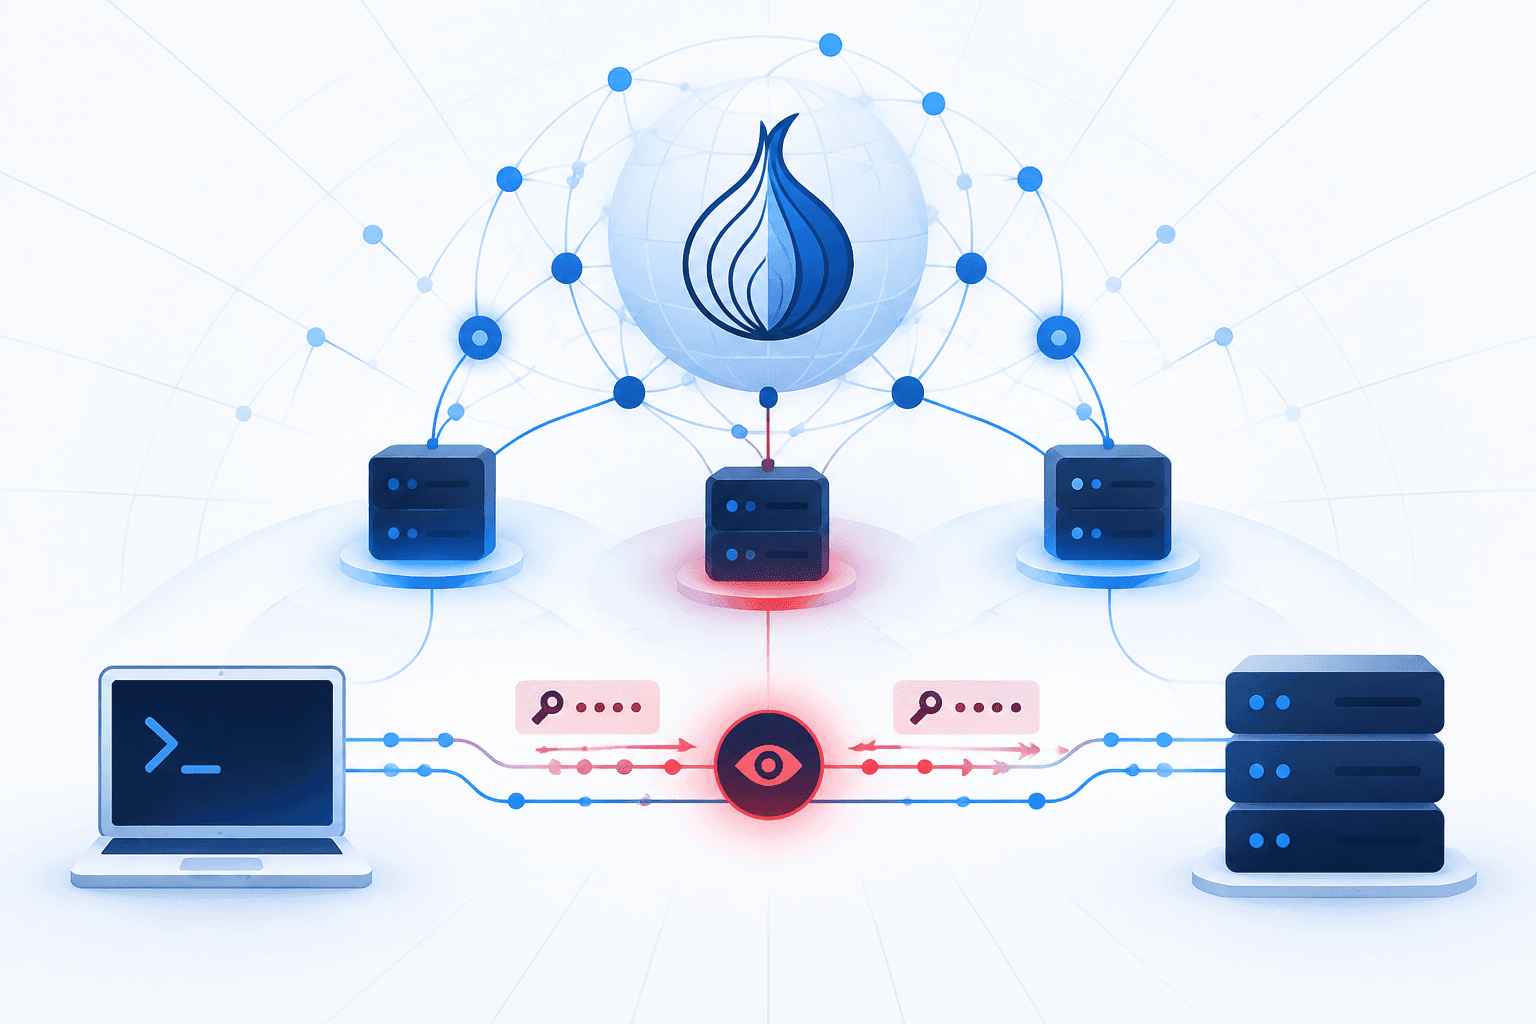
A researcher posting as u/kabakaba0 reported that 333 Tor exit nodes—approximately 10% of all Tor exits—began redirecting port 22 traffic on October 2. The nodes allegedly routed SSH connections to 12 interception servers running a Paramiko-based man-in-the-middle implementation that stole passwords and attempted to deploy Ebury malware on targeted systems.
In a Reddit post linking to a KABA write-up, the researcher claimed to have secured the removal of more than 300 exit nodes. The supplied reporting does not establish how those removals were performed or confirm successful malware installation. Organizations whose administrators use SSH through Tor should enforce strict SSH host-key verification, investigate unexpected host-key changes, and rotate credentials potentially exposed through intercepted connections.