OpenCode MCP Sign-In Flaw Allowed Code Execution on Windows and WSL
Vulnerability Disclosure · 4 sources · Updated 8d ago · First seen Oct 20, 2026
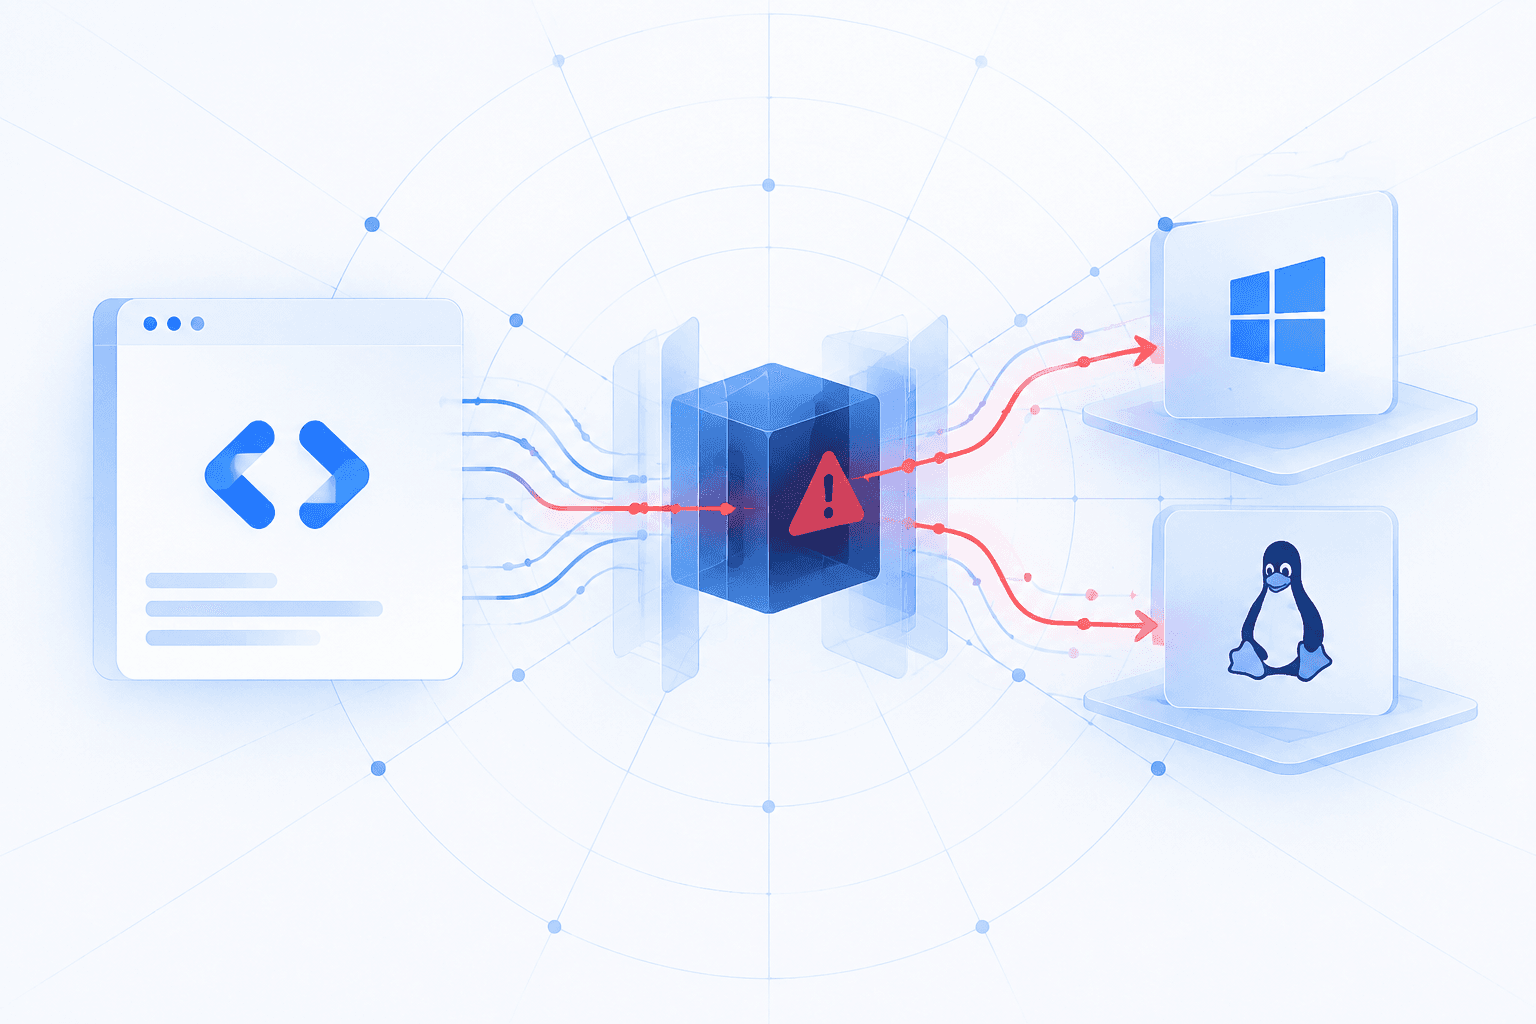
A command-injection vulnerability in OpenCode versions 1.0.137 through 1.18.32 allowed a malicious or compromised remote Model Context Protocol (MCP) server to execute code with a developer’s privileges on Windows and Windows Subsystem for Linux during OAuth authentication. An attacker-controlled authorization URL reached a browser-launch helper that embedded it in a PowerShell command without proper escaping, enabling execution without additional user interaction or consent. Pillar Security privately reported the flaw on August 29 and publicly disclosed it on October 19, proposing a critical severity score of 9.8; researchers reported no evidence of exploitation.
Anomaly fixed the vulnerability in OpenCode 1.18.33, released September 28, but did not request a CVE or publish a security advisory, leaving users reliant on direct version checks to identify affected installations. Organizations should upgrade vulnerable developer environments and review configured remote MCP servers. Researchers identified an update to the browser-launch dependency that correctly quotes URLs passed to PowerShell as the crucial remediation, warning that URL scheme validation alone is insufficient. The flaw is unrelated to the separately reported OpenCode Console breach that exposed stored AI provider keys.