Attackers Chain Ivanti Connect Secure Flaws to Gain Root Access
Active Exploitation · 2 sources · Updated 14d ago · First seen Oct 20, 2026
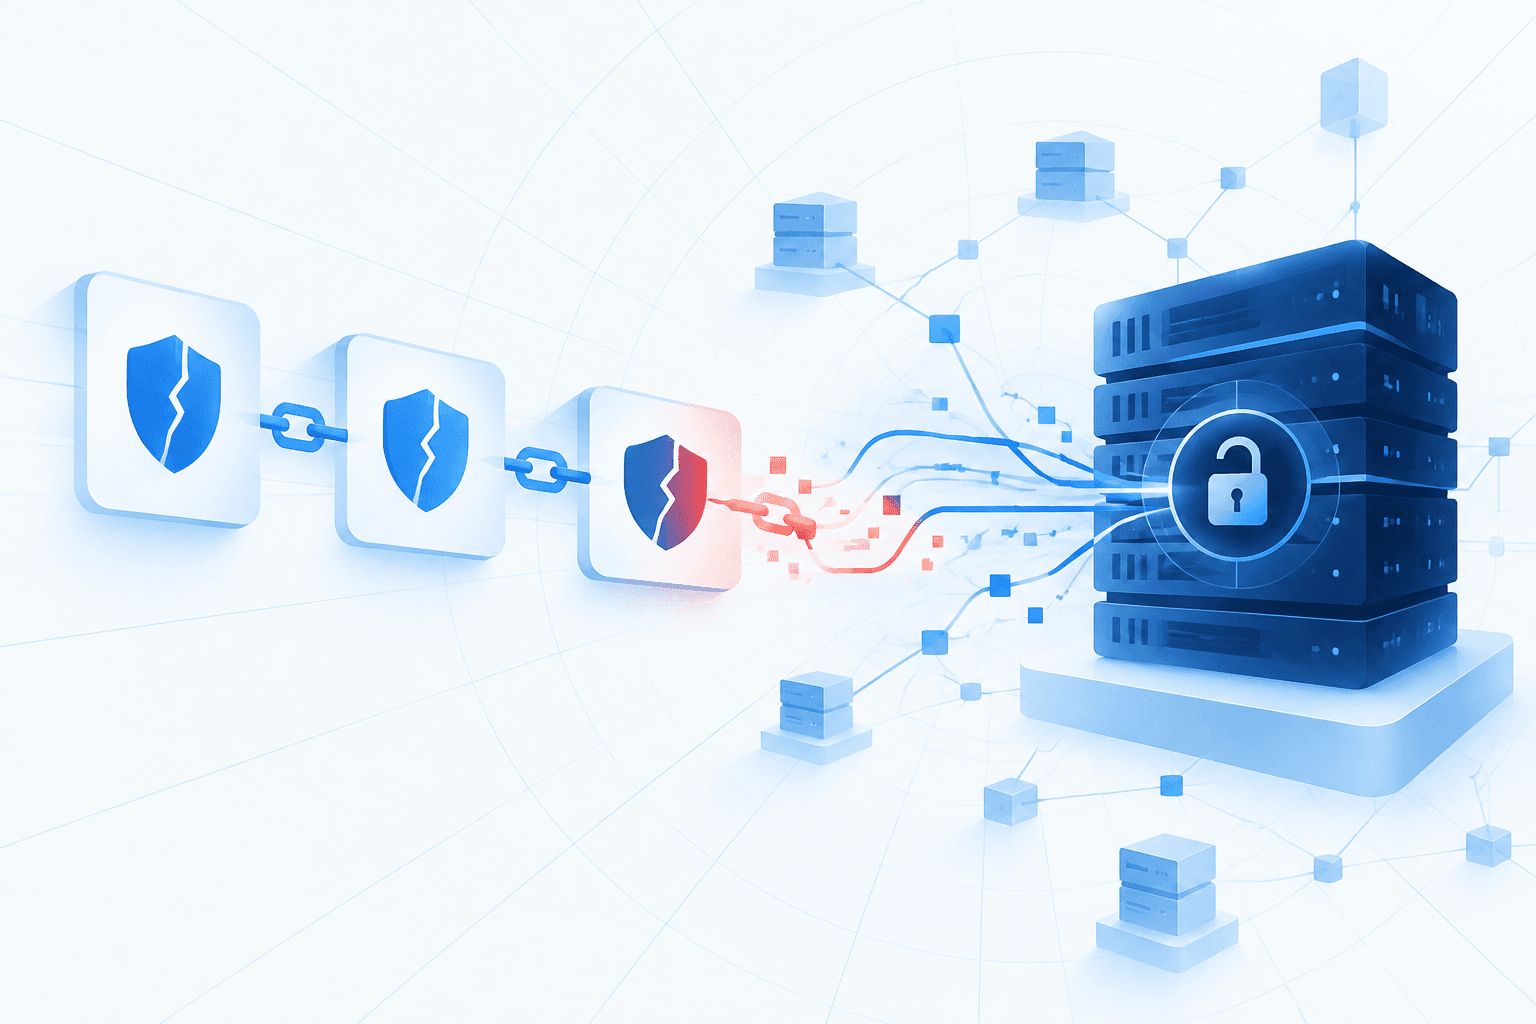
Threat actor UTA0576 is reportedly exploiting CVE-2026-104935 in Ivanti Connect Secure VPN appliances alongside a separate privilege-escalation vulnerability to obtain root access. The authentication-bypass and remote-code-execution flaw has a reported CVSS score of 8.6 and requires neither credentials nor user interaction. According to reporting citing Volexity research, attackers used in-memory execution and anti-forensic techniques to conceal activity. Observed post-exploitation activity included Active Directory data collection, LDAP packet capture, reconnaissance, and password spraying, raising risks of credential theft and compromise of internal systems.
Ivanti has reportedly patched CVE-2026-104935, but the separate privilege-escalation flaw remains unpatched. Affected organizations should apply available updates immediately and investigate potential compromise using memory and network forensic analysis, alongside monitoring for suspicious requests and filesystem artifacts. Because the reported attack chain uses stealth techniques, patching should be accompanied by compromise assessment; organizations running legacy versions should also plan migration.