Lazarus Targets South Korean Firms With Modular FlashHole Espionage Campaign
Threat Actor Intelligence · 14 sources · Updated 15h ago · First seen Oct 21, 2026
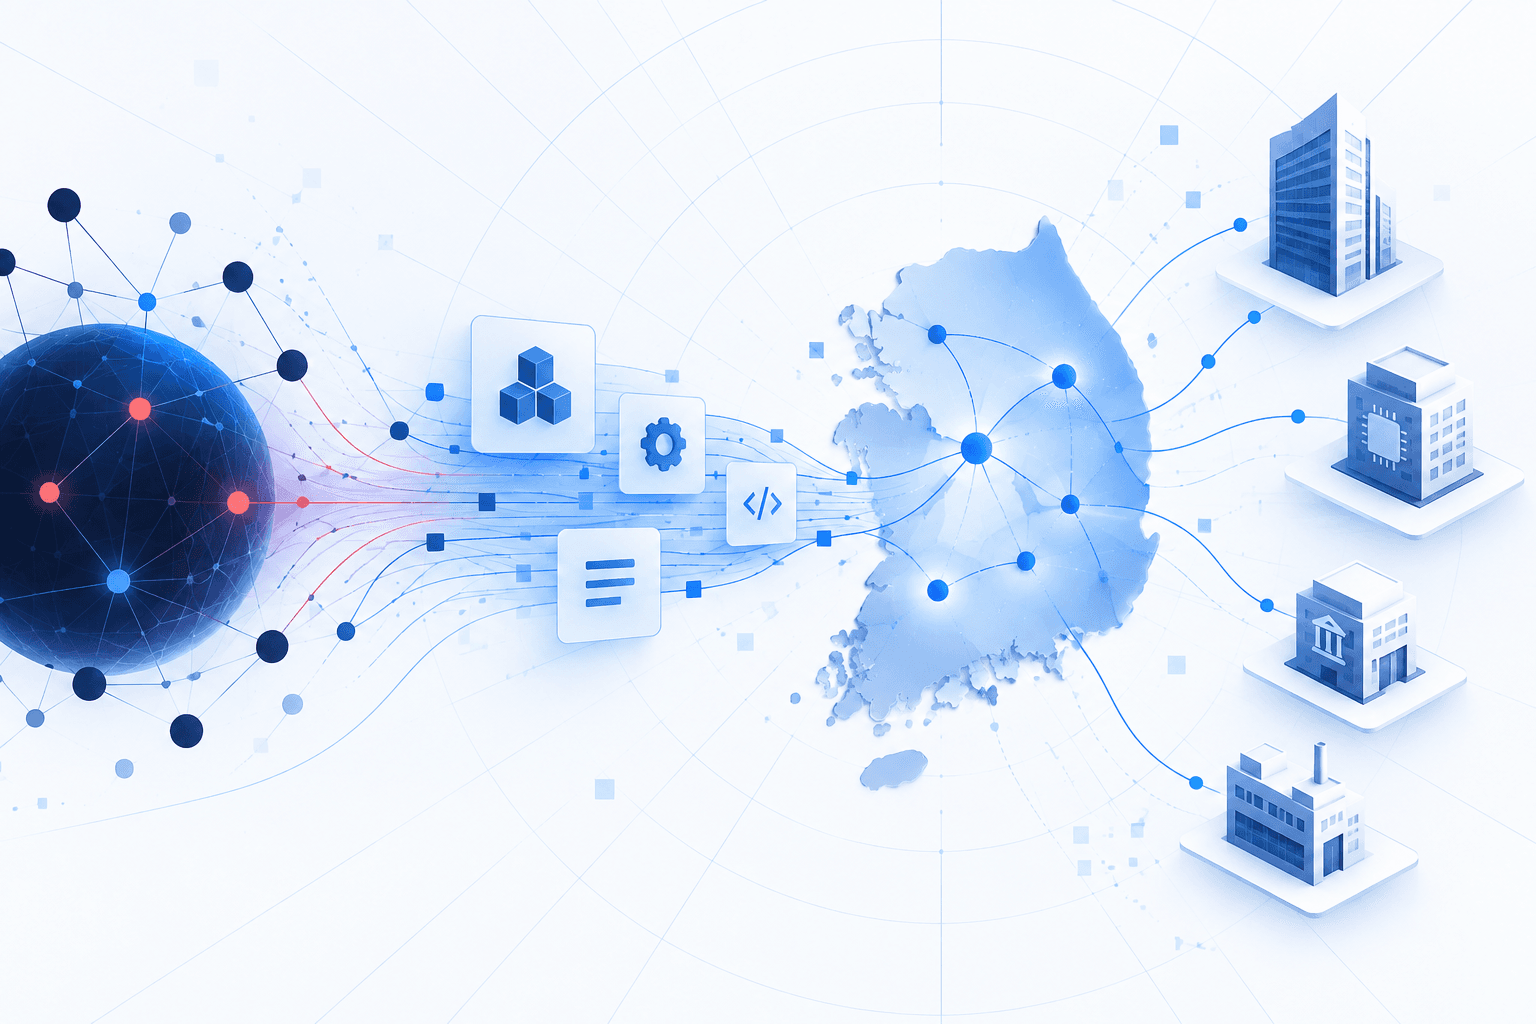
Lazarus Group’s Operation FlashHole espionage campaign compromised at least three South Korean organizations in software development, construction, and wired communications equipment manufacturing, with preparatory activity traced to July 2025. Securelist researchers assess that tailored phishing links, fabricated portfolio or résumé websites, and watering-hole techniques likely directed victims to malicious sites that triggered infection through INISAFE CrossWeb EX financial security software. The precise exploitation mechanism remains unconfirmed. Researchers link FlashHole to Operation SyncHole and the broader Cascade Hole campaign with medium-to-high confidence, while distinguishing it from separate COPPERHEDGE-associated monetization and data-leak activity.
FlashHole uses a predominantly memory-resident, multistage framework comprising TechHub, Cubridge, TouchShift, LPEClient, and newly identified TouchHub and ClientHub. Its capabilities include host profiling, browser credential theft, Active Directory reconnaissance, file collection, and process manipulation, with persistence through DLL side-loading and Windows services. Private GitHub repositories, Dropbox, and compromised legitimate websites support its infrastructure, while an updated LPEClient uses ML-KEM-1024 post-quantum key encapsulation and layered encryption to protect subsequent payload delivery. Defenders should prioritize investigation of suspicious INISAFE CrossWeb EX activity, unexpected service creation and DLL loading, and anomalous GitHub or Dropbox communications.