Sponsored Search Ads Abuse ChatGPT Content to Deliver ClickFix Malware Lures
Social Engineering & Fraud · 2 sources · Updated 24d ago · First seen Jul 26, 2026
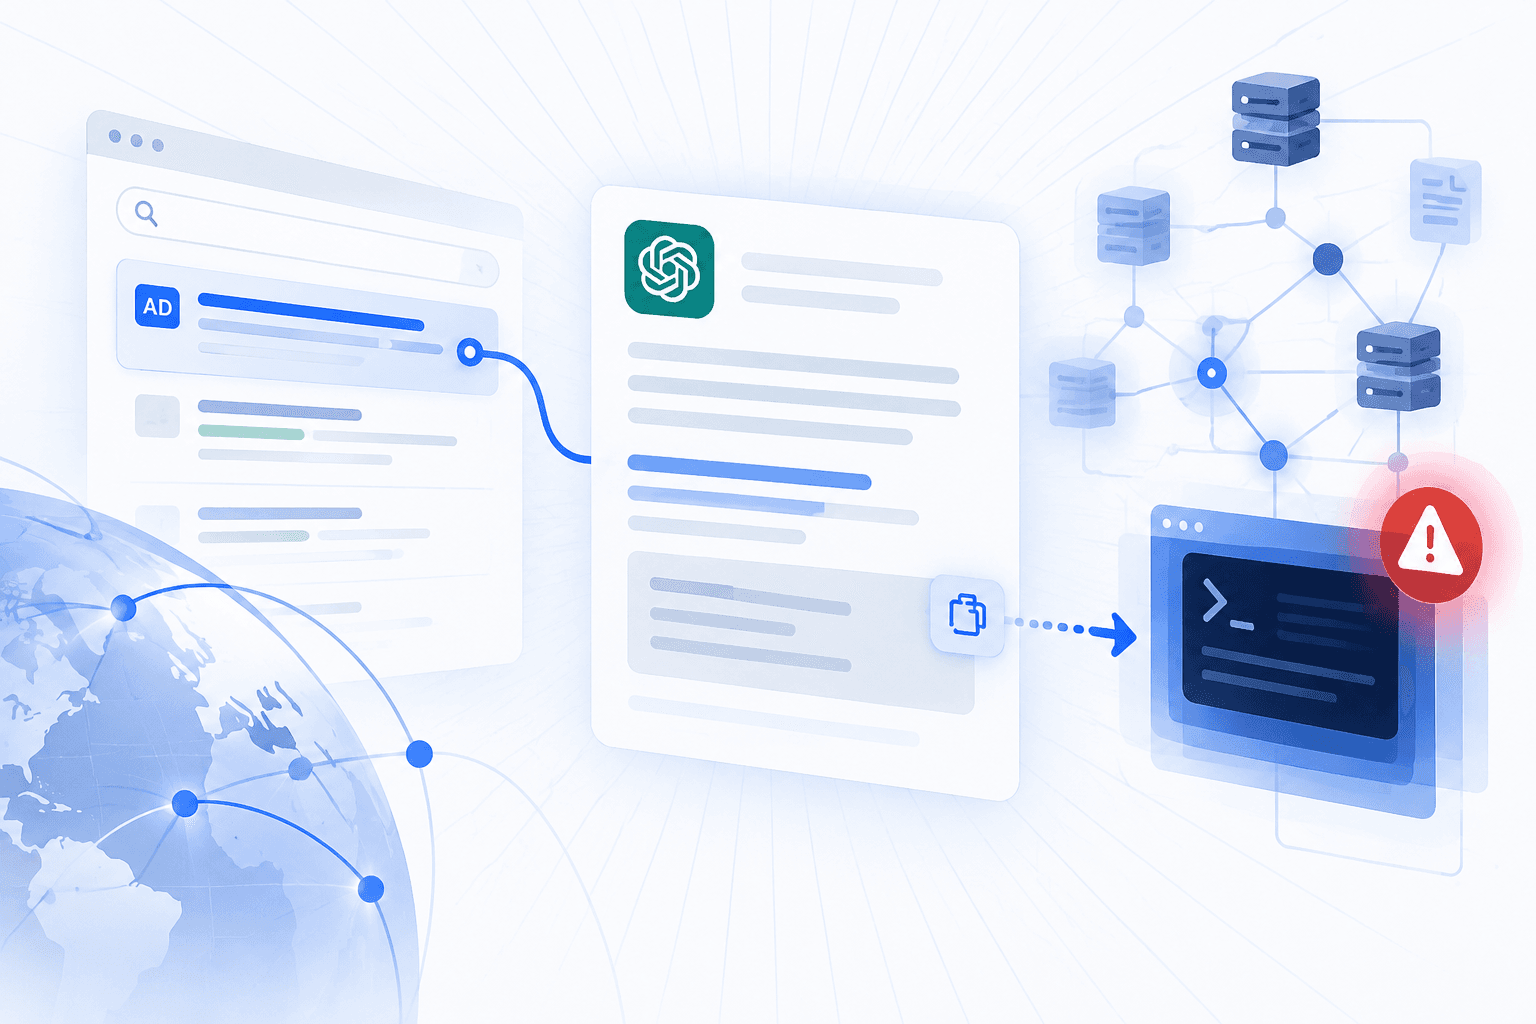
Attackers used sponsored search advertisements to funnel users through attacker-authored Custom GPTs and shared conversations on legitimate ChatGPT pages, exploiting trust in the platform to promote malicious destinations. Fake service warnings directed visitors to supposed “backup” domains. One confirmed redirect chain reached counterfeit ChatGPT and Cloudflare verification pages that used ClickFix instructions to persuade Windows users to execute a PowerShell loader. Isolated analysis identified behavior consistent with NetSupport RAT delivery, rather than establishing confirmed infections across the campaign.
Island researchers mapped approximately 850 paid-ad landings, 26 ChatGPT-lookalike destinations, and 71 Google Ads campaign IDs from late May through August 24, 2026. Only a small subset of destinations was confirmed to serve the exact lure, so those totals should not be interpreted as victim counts. The campaign rotated infrastructure and used separate PowerShell/MSI and WebDAV delivery branches. Researchers found no evidence of a vulnerability in ChatGPT or Google and did not attribute the activity to a specific operator. Defensive priorities include warning users against executing commands supplied by verification pages and monitoring unexpected PowerShell, MSI, and WebDAV activity following browser sessions.