StealC Seller Launches Stadia RAT With Credential Theft and Hidden Desktop Control
Malware Intelligence · 4 sources · Updated 22d ago · First seen Oct 22, 2026
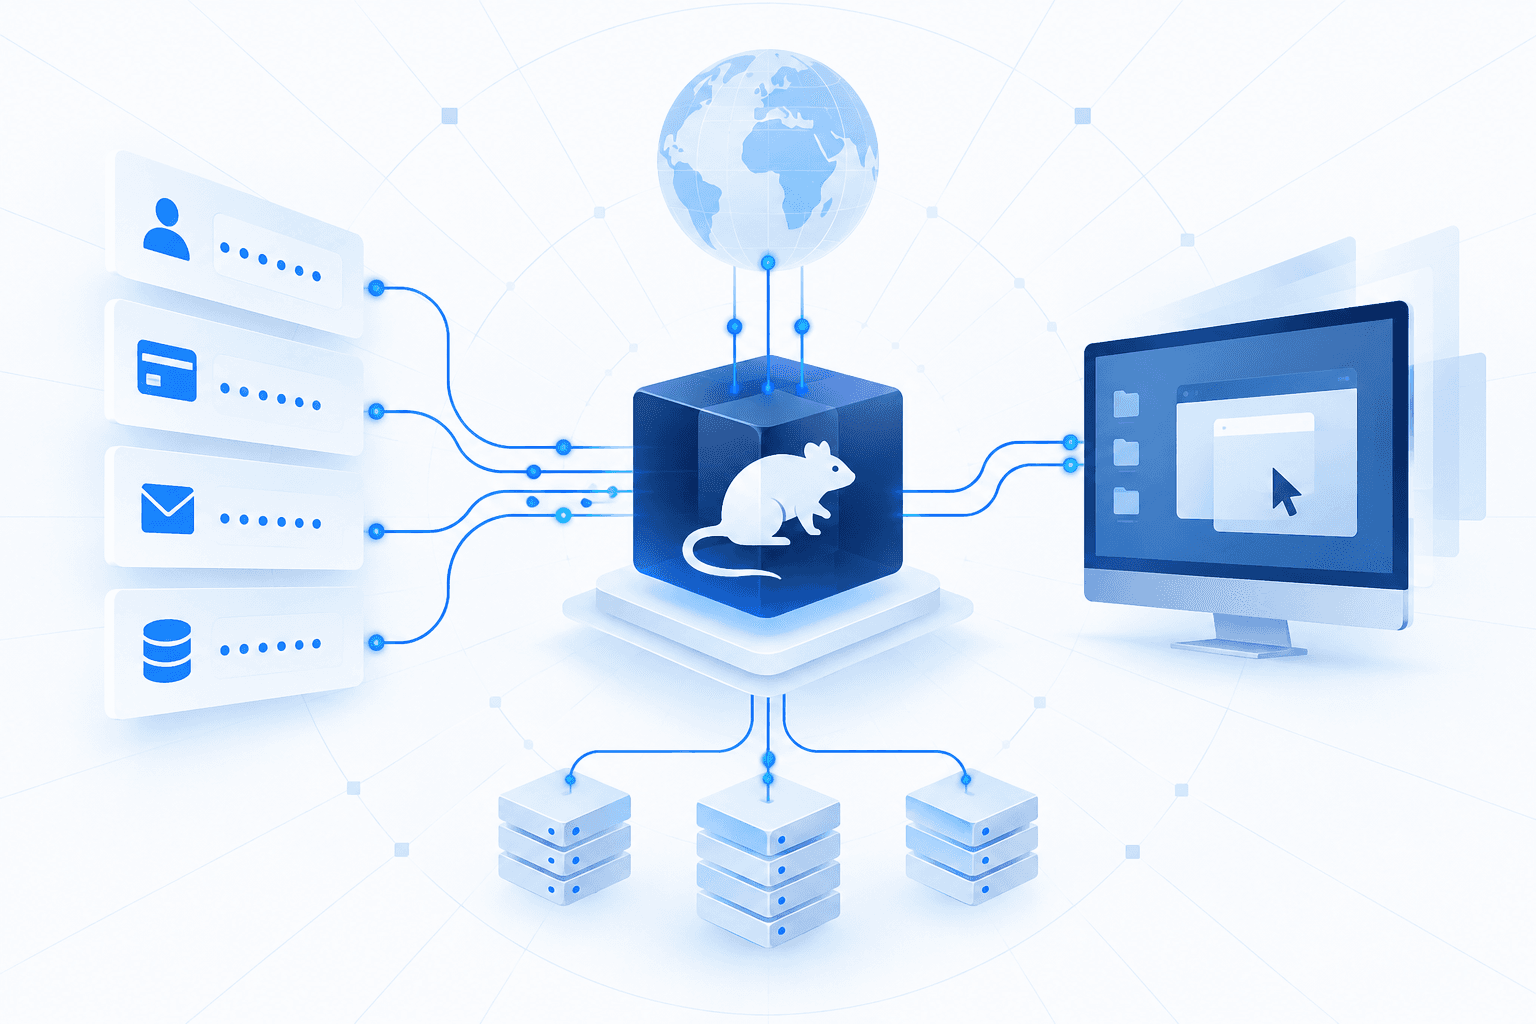
The seller behind the StealC infostealer launched Stadia, a Windows remote access trojan, on October 16 following the June disruption of StealC by Operation Endgame. Stadia combines credential theft with hidden desktop access, remote command execution, file and process management, and additional payload delivery. Varonis Threat Labs found a Chromium App-Bound Encryption helper byte-for-byte identical to the one in StealC 3.5, supporting the claimed code continuity between the malware families.
The analyzed implant persists through hidden scheduled tasks, injects code into browser processes to recover encryption keys, and can add Microsoft Defender exclusions when elevated. It communicates with three hard-coded HTTP servers using RC4-encrypted, Base64-encoded data mislabeled as JSON. Because infrastructure and encryption keys vary between builds, defenders should prioritize behavioral detection of scheduled-task persistence, browser injection, and unauthorized Defender exclusions over static indicators. The reporting does not establish an initial delivery method or an independently verified infection count.