Stolen Okta Support Tokens Enabled Intrusions at Cloudflare, 1Password and BeyondTrust
Breach & Incident Intelligence · 6 sources · Updated 2d ago · First seen Oct 20, 2023
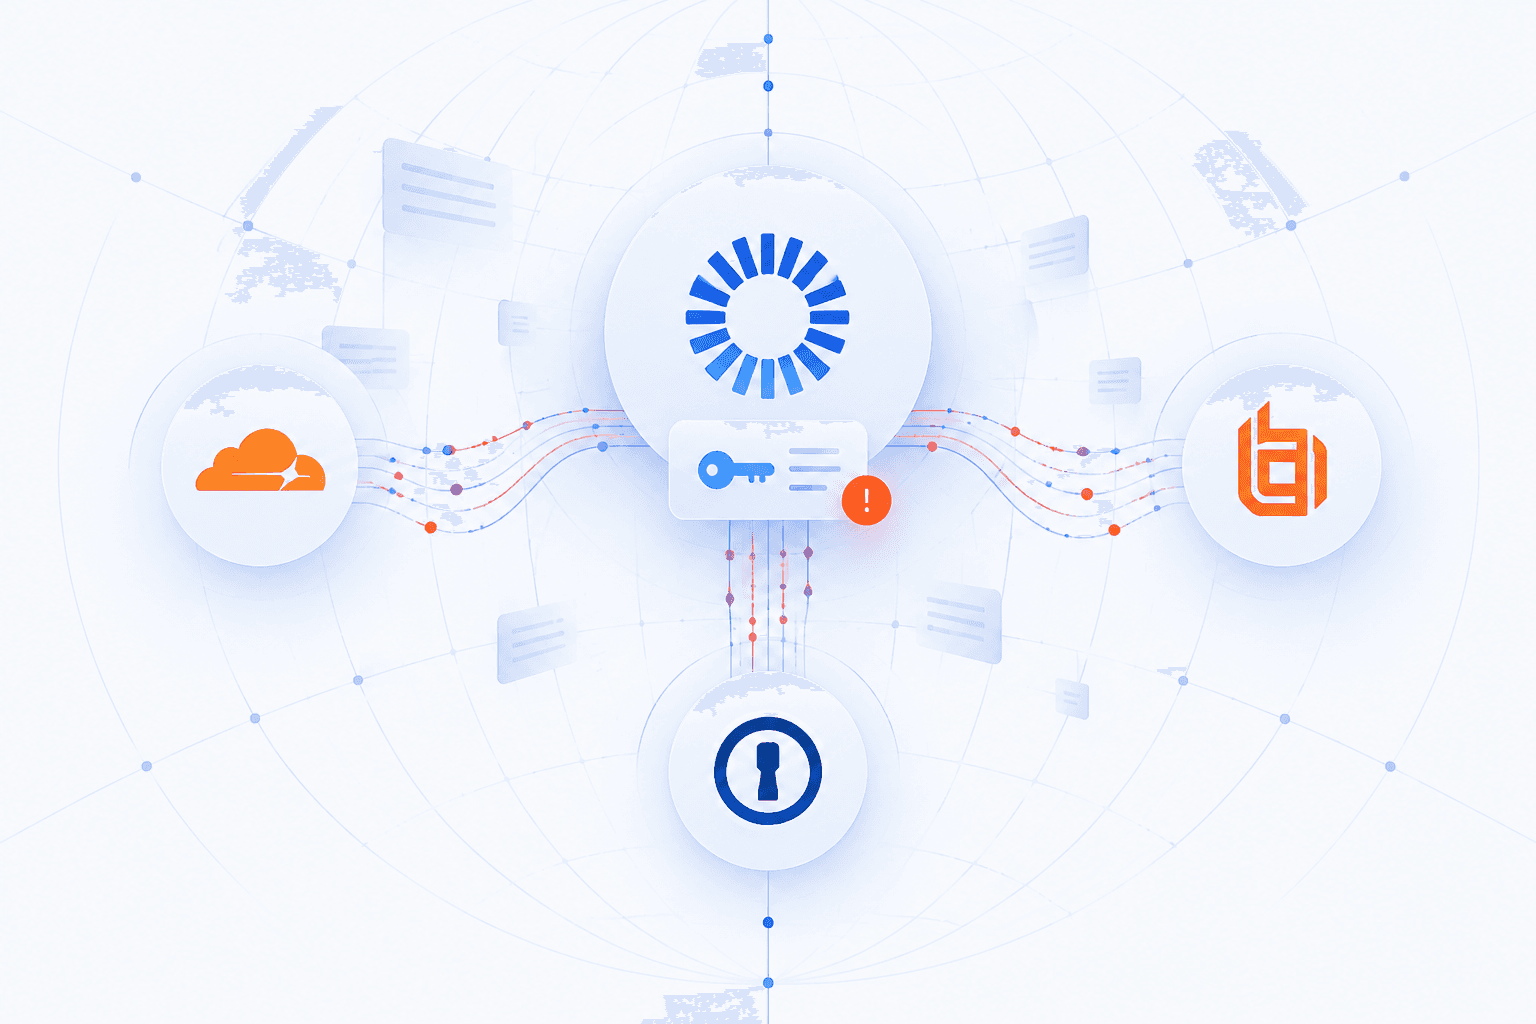
Attackers breached Okta’s customer support case management system using a stolen credential and accessed customer-uploaded files, including HTTP Archive (HAR) recordings containing session tokens and cookies. Those credentials enabled impersonation and unauthorized activity in customer Okta environments, including Cloudflare, 1Password and BeyondTrust. Okta said it notified approximately 170 customers, about 1% of its customer base, disabled the compromised support account, invalidated associated access tokens and published indicators of compromise. A subsequent Malwarebytes report linked the breach to an employee signing into a personal Google account.
Customer detections exposed significant notification and response delays. 1Password detected and terminated suspicious activity on September 29, 2023; BeyondTrust detected an attempted takeover on October 2, roughly 30 minutes after uploading a HAR file to Okta. Okta reported containing the support-system intrusion on October 17. Cloudflare detected token-based access on October 18, more than 24 hours before Okta notified it, and reported that attackers used an administrative session and compromised two employee accounts. Cloudflare contained the intrusion before persistence was established and found no impact to customer information, customer systems or its production network. 1Password likewise reported no access to user data or compromise of other sensitive systems, while BeyondTrust reported no customer impact. Cloudflare called for faster disclosure, hardware-based MFA and stronger session and account monitoring; the token theft also underscores the need to remove authentication secrets from support uploads.