OpenSSL TLS Handshake Flaw Lets Malicious Servers Crash Connecting Applications
Vulnerability Disclosure · 7 sources · Updated 14d ago · First seen Jan 9, 2014
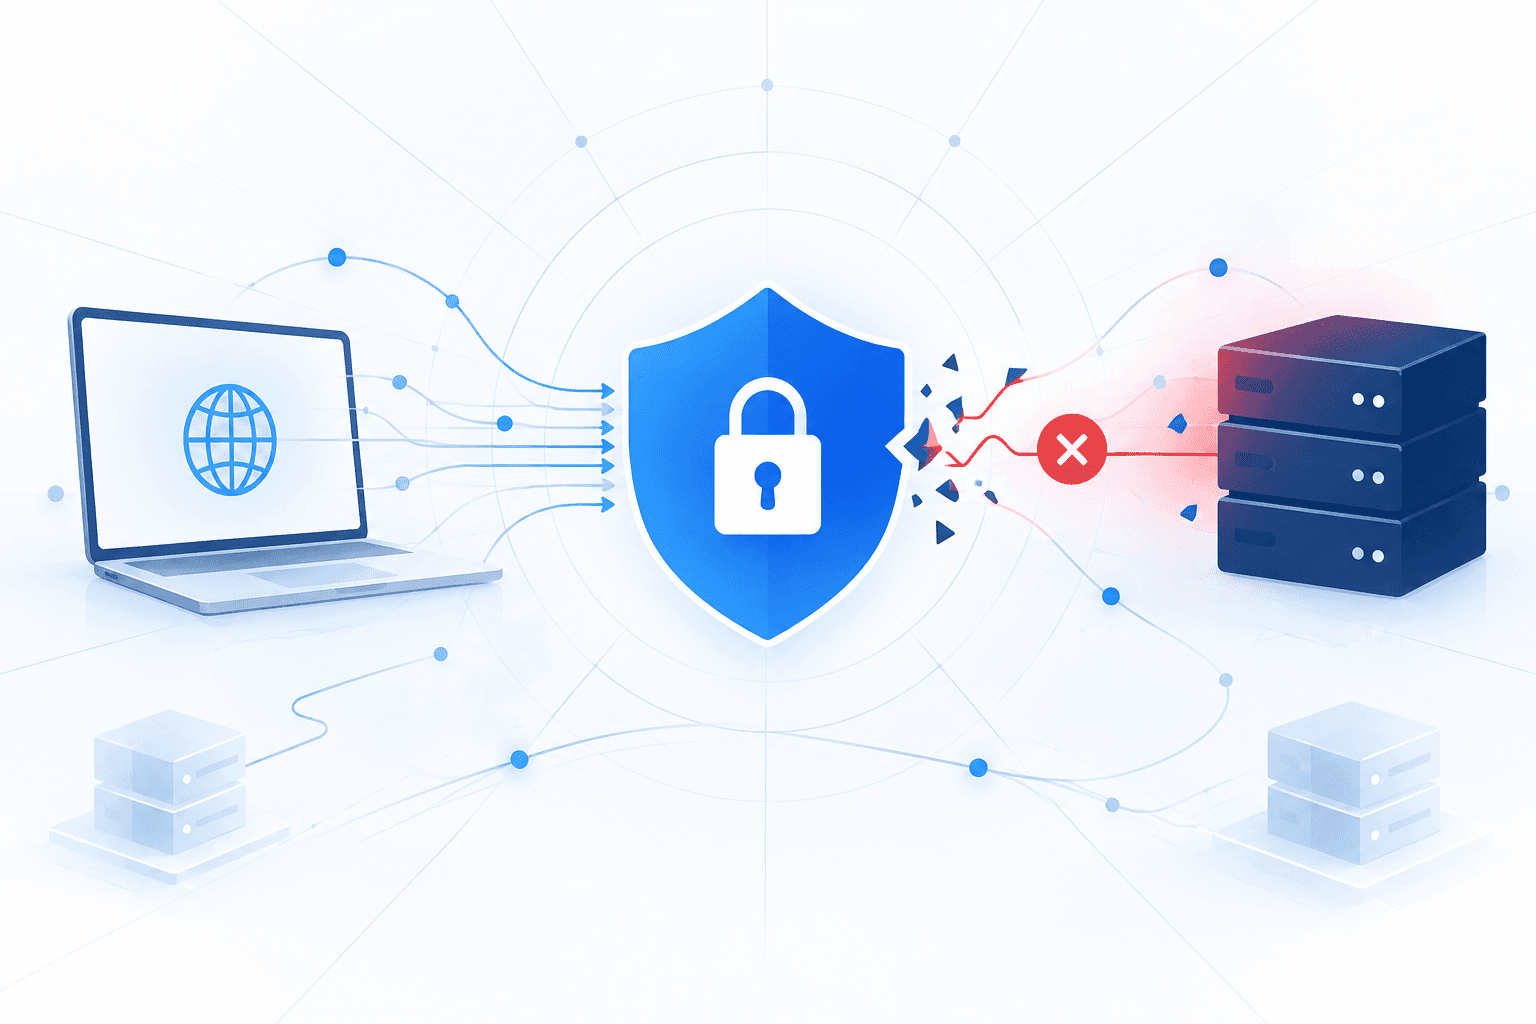
A denial-of-service vulnerability in OpenSSL 1.0.1 releases before 1.0.1f allows a malicious remote TLS server to crash an application connecting to it. Tracked as CVE-2013-4353, the flaw involves a crafted Next Protocol Negotiation record sent during the TLS handshake, triggering a NULL pointer dereference in the ssl3_take_mac function in ssl/s3_both.c. The CVE record was originally published on January 9, 2014, with Red Hat listed as the assigning authority.
The exposure affects applications acting as TLS clients, rather than requiring an attacker to initiate a connection to a vulnerable server. OpenSSL 1.0.1f fixed the vulnerability; organizations retaining affected legacy software should migrate to a supported release and verify that dependent applications use the updated library. The supplied references do not establish active exploitation or identify affected organizations.