uCreator Android Spyware Steals Telegram Credentials and Enables WeChat Account Cloning
Malware Intelligence · 5 sources · Updated 4h ago · First seen Oct 24, 2026
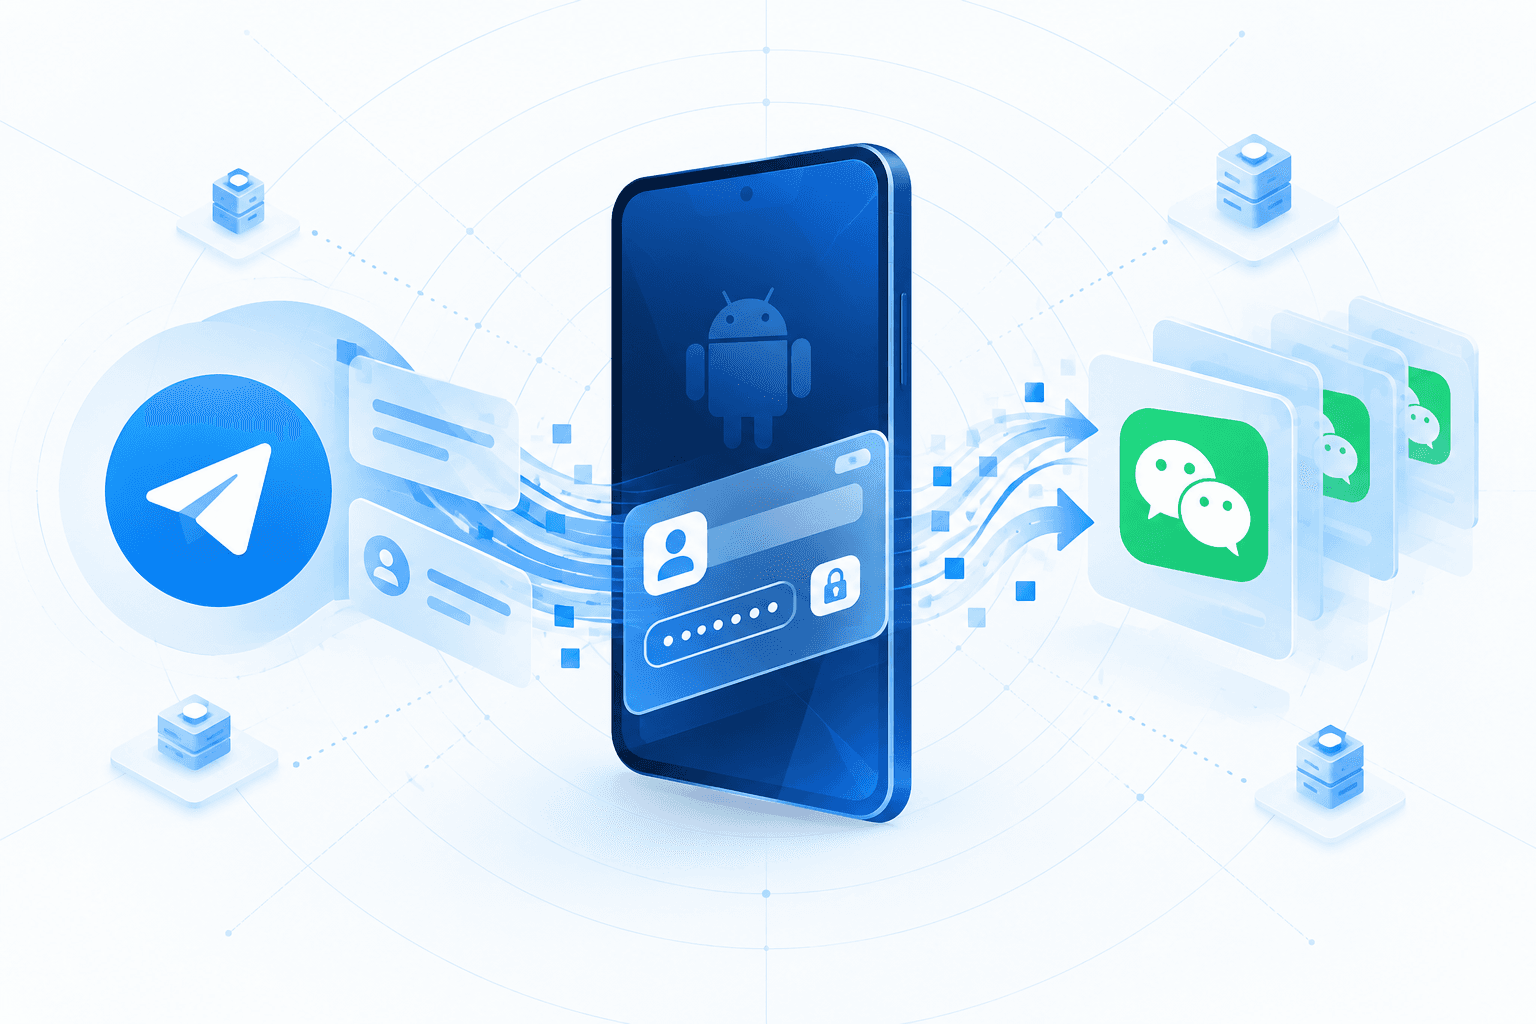
Researchers identified uCreator, also marketed as YingGai, as a rentable Android spyware platform that targets Telegram and WeChat through modified applications and an attacker-controlled virtualization container called Onion Box. Recovered code supports interception of one-time passwords, extraction of messages and contacts, capture of Telegram two-step-verification passwords, and account-session manipulation, including concealment of attacker sessions. The platform also enables WeChat account cloning and camera spoofing intended to bypass identity-verification liveness checks. These are documented capabilities; the investigation does not establish that operators exercised all of them against victims.
Researcher Ovi linked uCreator’s Telegram functionality to Baohuo through matching code, infrastructure, and commands. Doctor Web previously reported more than 58,000 Baohuo infections involving tampered Telegram X apps distributed through malicious websites and third-party Android catalogs; that figure is not a verified uCreator victim count. An exposed GitLab instance revealed a multitenant backend for command dispatch, account harvesting, backups, and automated activity designed to evade platform risk checks. Evidence connects components to three companies in Hunan, China, but common ownership and responsibility for earlier attacks remain unproven. Compatibility failures observed in a captured instrumentation engine on Android 16/17 do not establish platform-wide protection. Organizations should restrict untrusted messaging apps and containers, investigate suspicious account sessions, and reset exposed credentials from trusted devices.