Microsoft Authenticator Android Flaw Let Rogue Apps Steal Work-Account Tokens
Vulnerability Disclosure · 10 sources · Updated 12d ago · First seen Oct 26, 2026
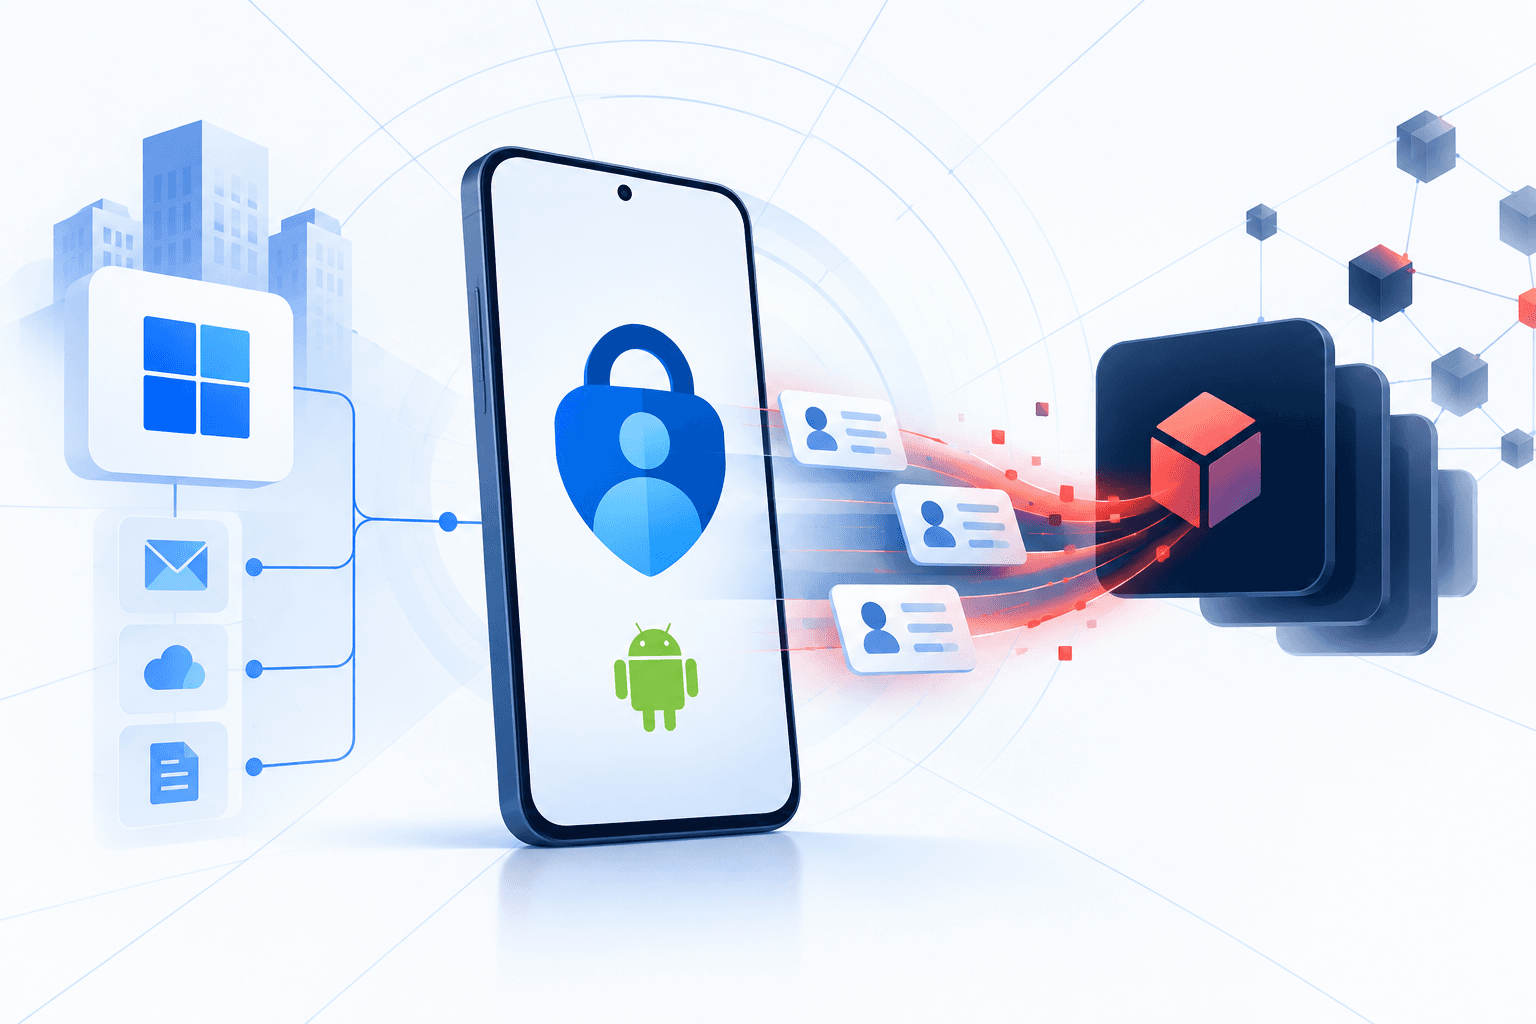
Microsoft patched CVE-2026-80097, a high-severity vulnerability in Microsoft Authenticator for Android that allowed a malicious app installed on the same device to silently obtain work-account tokens. The flaw, rated CVSS 8.6, required no declared Android permissions, account credentials, or further user approval. Authenticator’s broker trusted attacker-supplied application identity information without verifying that it belonged to the calling app, allowing rogue applications to impersonate trusted Microsoft apps and access Microsoft Graph resources.
Enclave researchers demonstrated access to email, files, calendars, SharePoint, and Teams, as well as changes to account sign-in methods by impersonating Authenticator itself. Adding an attacker-controlled passkey could preserve account access even after the malicious app was removed. Microsoft addressed the vulnerability in Authenticator version 6.2606.4246; administrators should verify that managed Android devices run that version or later, restrict sideloading, and monitor suspicious token use, Microsoft Graph activity, and unexpected sign-in-method changes.