Blue Initiative Launches Maritime IT and OT Vulnerability Repository
Sector Threat Intelligence · 4 sources · Updated 2h ago · First seen Oct 26, 2026
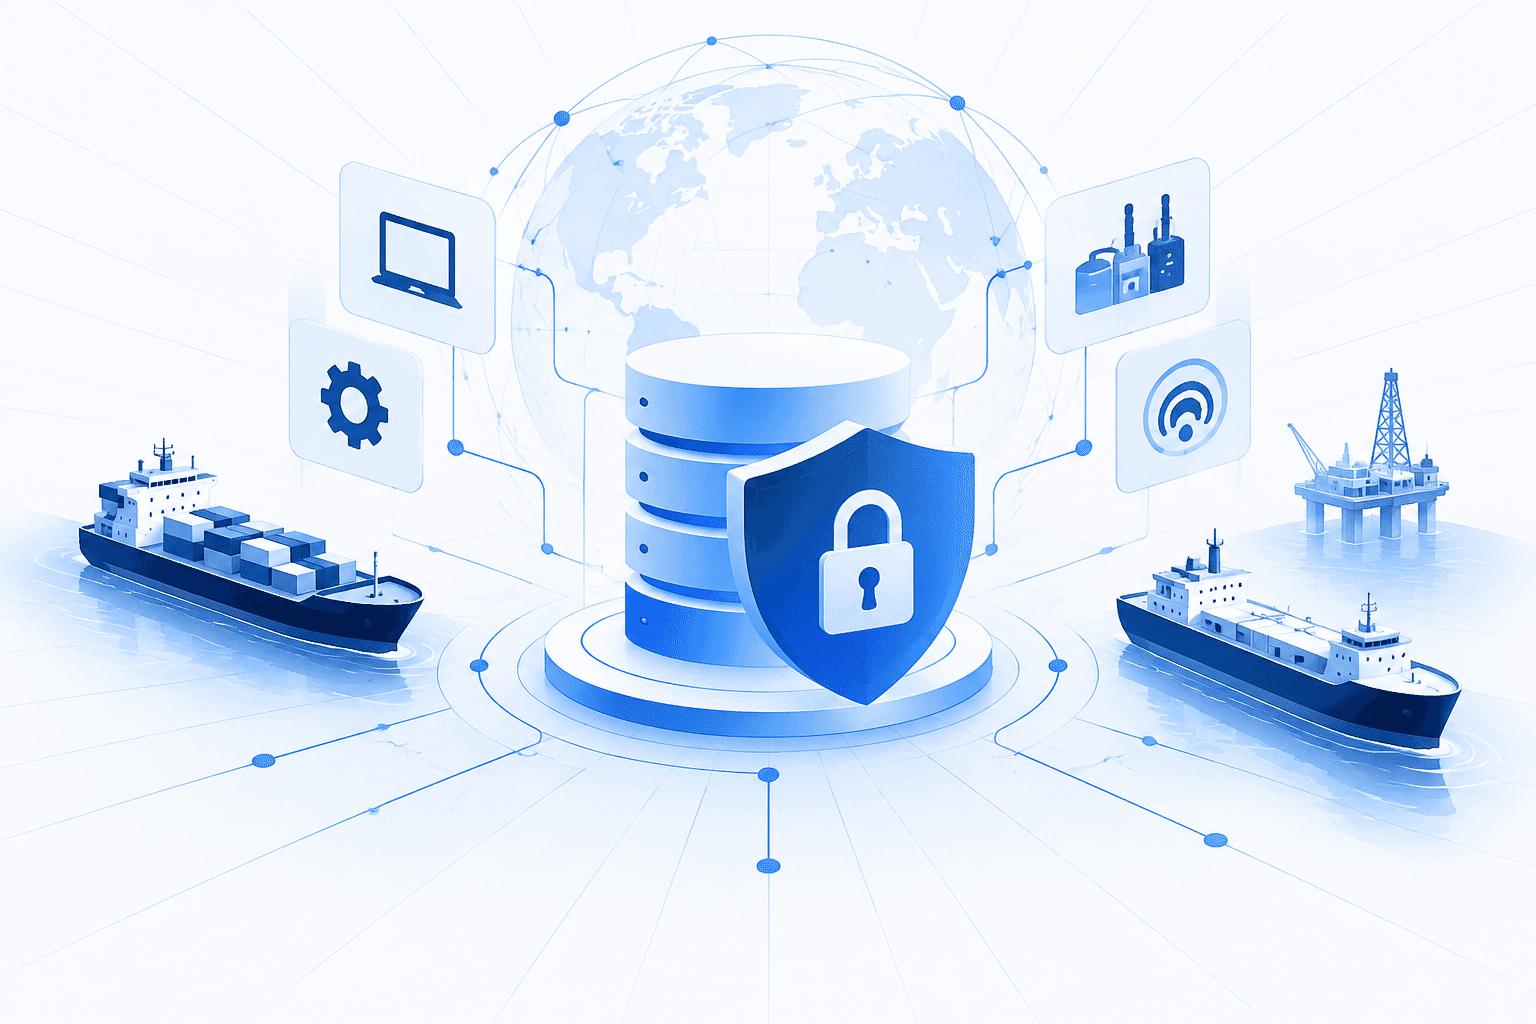
A maritime industry coalition launched the Blue Initiative and its public-access Maritime Vulnerabilities Repository (MVR) to help operators identify software flaws affecting vessels, offshore facilities, ports and supporting onshore infrastructure. Founded by Cydome, Rakuten Maritime, ClassNK and Bureau Veritas, with participation from MTS-ISAC, the initiative describes MVR as the first database dedicated exclusively to maritime-relevant IT and operational technology vulnerabilities. At publication, it tracked 29,505 vulnerabilities, predominantly affecting fleet IT systems, including 37 in maritime-only systems.
The repository combines vulnerability advisories, CVE records and CISA’s Known Exploited Vulnerabilities catalog with partner-researcher validation; the coalition says vulnerabilities will be published only after a patch is available. Operators can browse CVEs, filter by equipment or vendor, access expert analysis and subscribe to alerts to support remediation prioritization. The launch follows investigations into suspected cyberattacks on two commercial oil tankers, which a federal official linked to known, unpatched onboard vulnerabilities, alongside unconfirmed extortion claims involving dozens of maritime organizations.