Phished npm Maintainer Account Used to Poison 18 Popular Packages With Crypto-Stealing Code
Supply Chain Risk · 5 sources · Updated 7d ago · First seen Sep 8, 2025
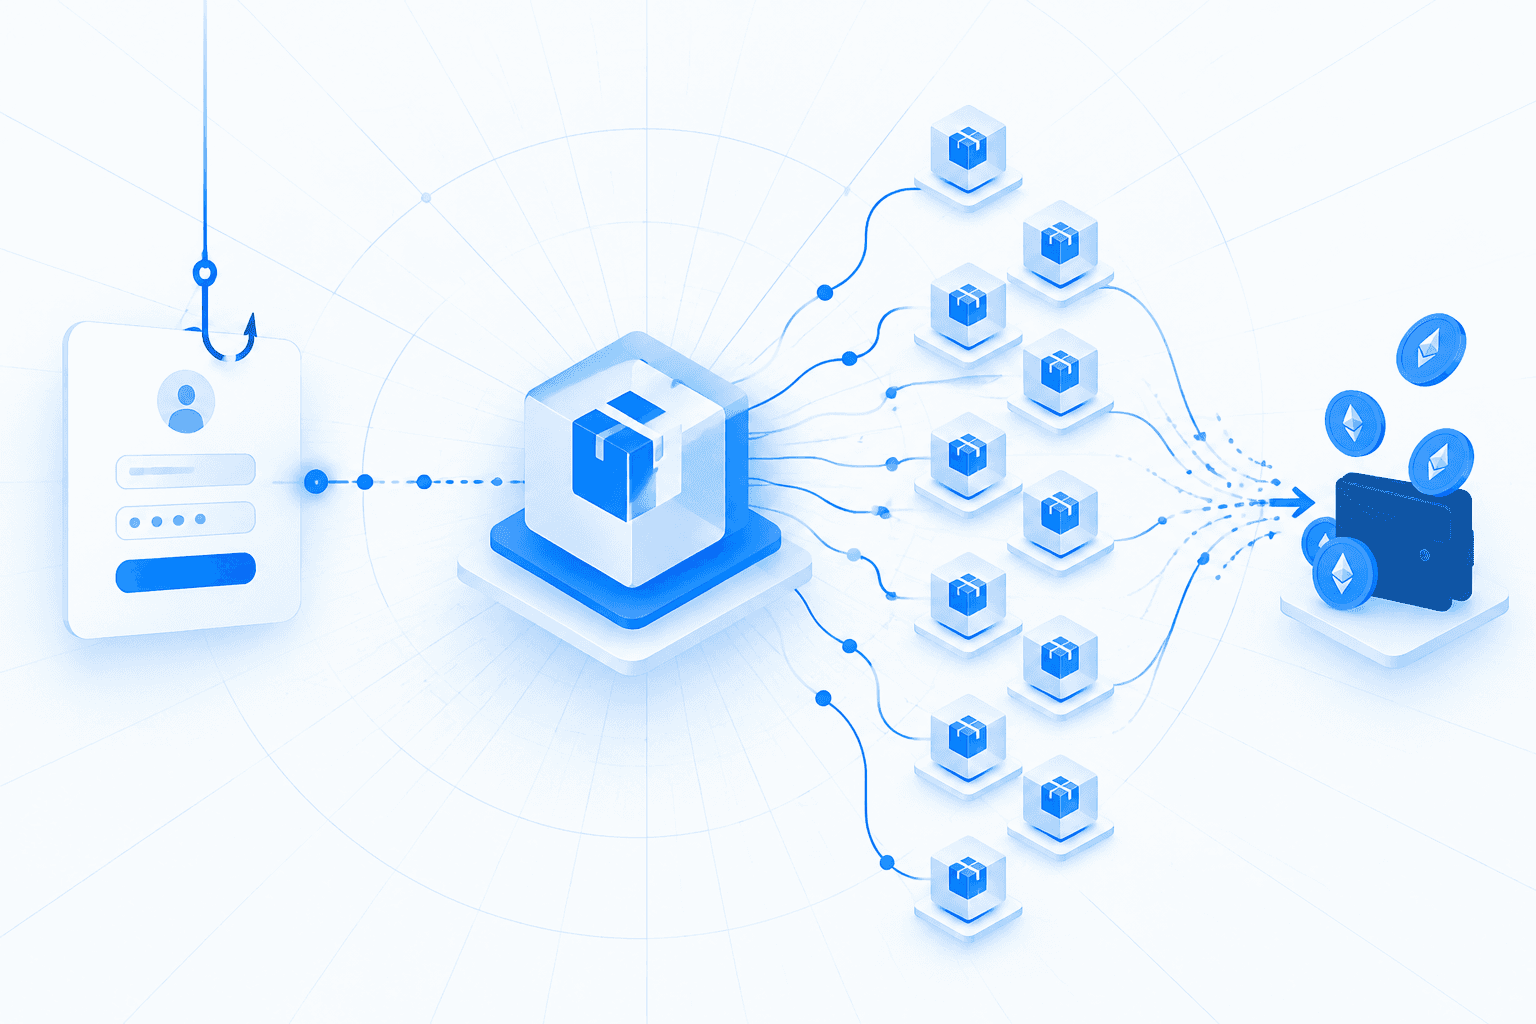
Attackers compromised npm maintainer Qix through a phishing email impersonating an npm two-factor authentication reset notice, then published cryptocurrency-stealing versions of at least 18 widely used JavaScript packages. Affected libraries included chalk, debug, strip-ansi, and supports-color, collectively downloaded more than two billion times weekly—a measure of potential reach, not confirmed infections. The browser-focused payload targeted cryptocurrency transactions through applications incorporating the poisoned dependencies. Coinspect reported that malicious versions were available for nearly seven hours on September 8 before npm confirmed their removal.
Follow-up reporting found that dependency controls limited exposure in examined decentralized applications. Coinspect identified more than 30 frontend deployments containing debug, but the production builds it analyzed used safe, pinned versions; Curve Finance’s lockfile retained version 4.4.1 rather than malicious version 4.4.2 despite six layers of indirect dependencies. MetaMask separately reported that LavaMoat sandboxing neutralized the attack for its users. Recommended safeguards include enforced lockfiles, reviewed dependency updates, audits of recent installations, phishing-resistant MFA for maintainers, and restricted build environments. Dynamically loaded third-party widgets remain a potential route around dependency controls. The incident also illustrates risks covered by the Ethereum Foundation’s Trillion Dollar Security initiative, which targets improvements across wallet security, frontends, infrastructure, and dependency management.