Ukraine Warns of Dahua Camera Compromises Through Easy4IP Cloud Access
Active Exploitation · 9 sources · Updated 21d ago · First seen Oct 26, 2026
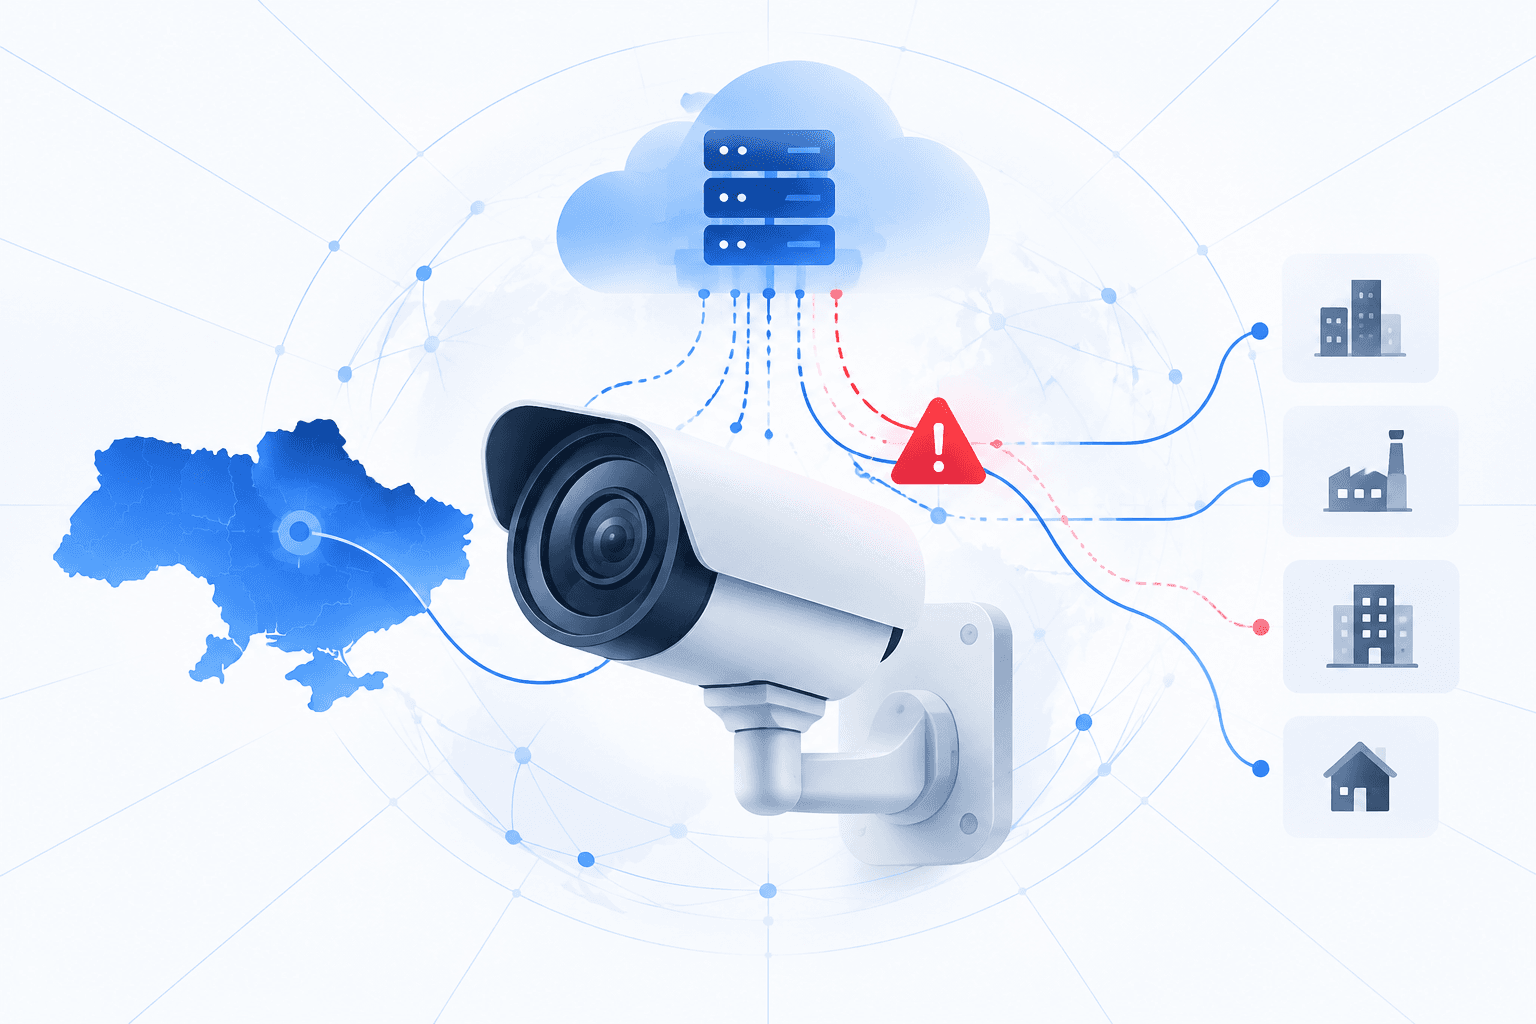
Ukraine’s computer emergency response team, CERT-UA, warned that unidentified attackers are compromising Dahua surveillance cameras and video recorders through the Easy4IP cloud remote-access service. Attackers reportedly discover devices by guessing predictable serial numbers, then gain access using weak passwords or authentication-bypass vulnerabilities in outdated firmware, including CVE-2021-33044 and CVE-2021-33045. They modify device settings and create unauthorized accounts. CERT-UA did not disclose the number of affected devices, attack dates or perpetrators.
Unauthorized accounts and recovery codes reportedly survive password changes and, on most firmware versions, factory resets, making those measures alone insufficient to establish that a device is secure. The warning carries particular significance for Ukraine, where Chinese-made cameras remain deployed by government institutions and military units, and Russian intelligence services have previously compromised cameras to monitor air defenses and critical infrastructure. Separately, Hunt.io reported more than 14,500 compromised Dahua devices in August 2026, concentrated in Ukraine and Russia; no formal connection between that activity and CERT-UA’s findings has been established.