Attackers Abuse Claude Shared Content and Google Ads to Deliver macOS and Windows Malware
Social Engineering & Fraud · 3 sources · Updated 2h ago · First seen Oct 26, 2026
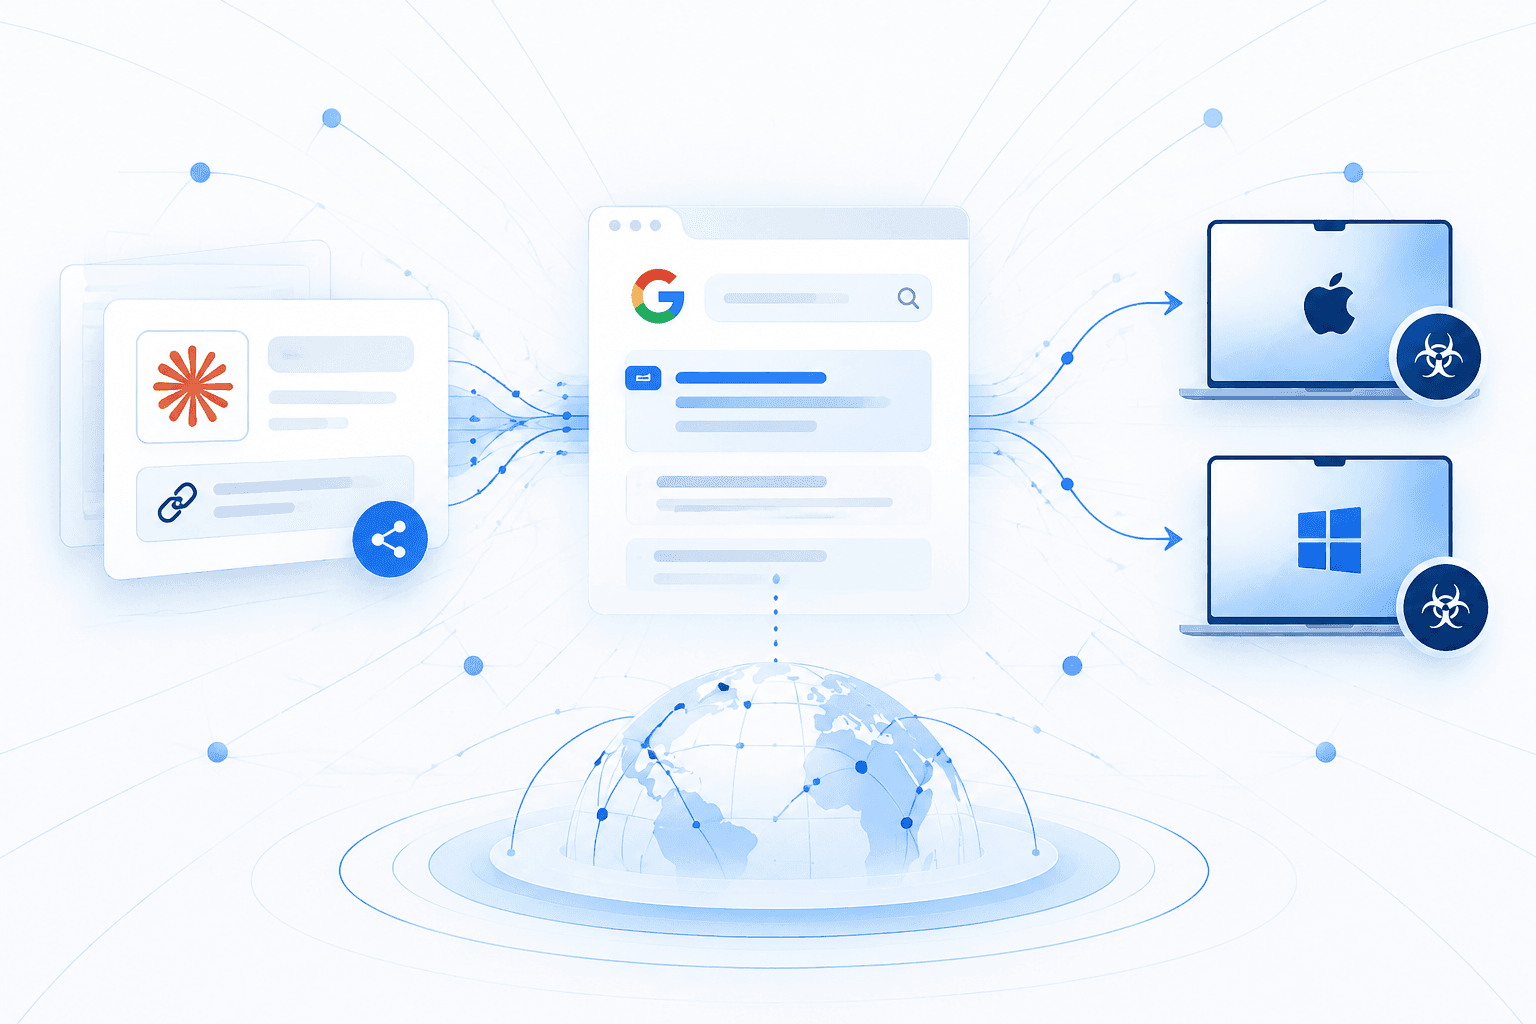
Attackers used Claude’s public Artifacts and Shared Chats on the legitimate claude.ai domain to host fake installation instructions, promoting the malicious content through Google Ads. Gen Digital identified two campaigns that used ClickFix social engineering to persuade users to execute malicious commands themselves. Neither campaign required compromising Anthropic’s infrastructure; instead, attackers exploited trust in Claude’s domain and branding to make user-generated instructions appear legitimate.
The macOS campaign delivered Atomic macOS Stealer (AMOS) to steal credentials, browser sessions, cryptocurrency-wallet data, and sensitive files. It could also replace Ledger and Trezor applications with trojanized versions designed to capture recovery phrases. The Windows campaign delivered an obfuscated, encrypted .NET remote-access payload capable of process injection, antivirus discovery, screenshot capture, cryptocurrency-wallet discovery, and ongoing communication with an attacker-controlled server. Defenders should warn users against executing untrusted installation commands, even when hosted on legitimate platforms, and treat devices where these commands were run as compromised.