Testmetest npm Worm Arms 42 GitHub Repositories and Threatens Token-Revocation Wipe
Supply Chain Risk · 3 sources · Updated 11h ago · First seen Oct 26, 2026
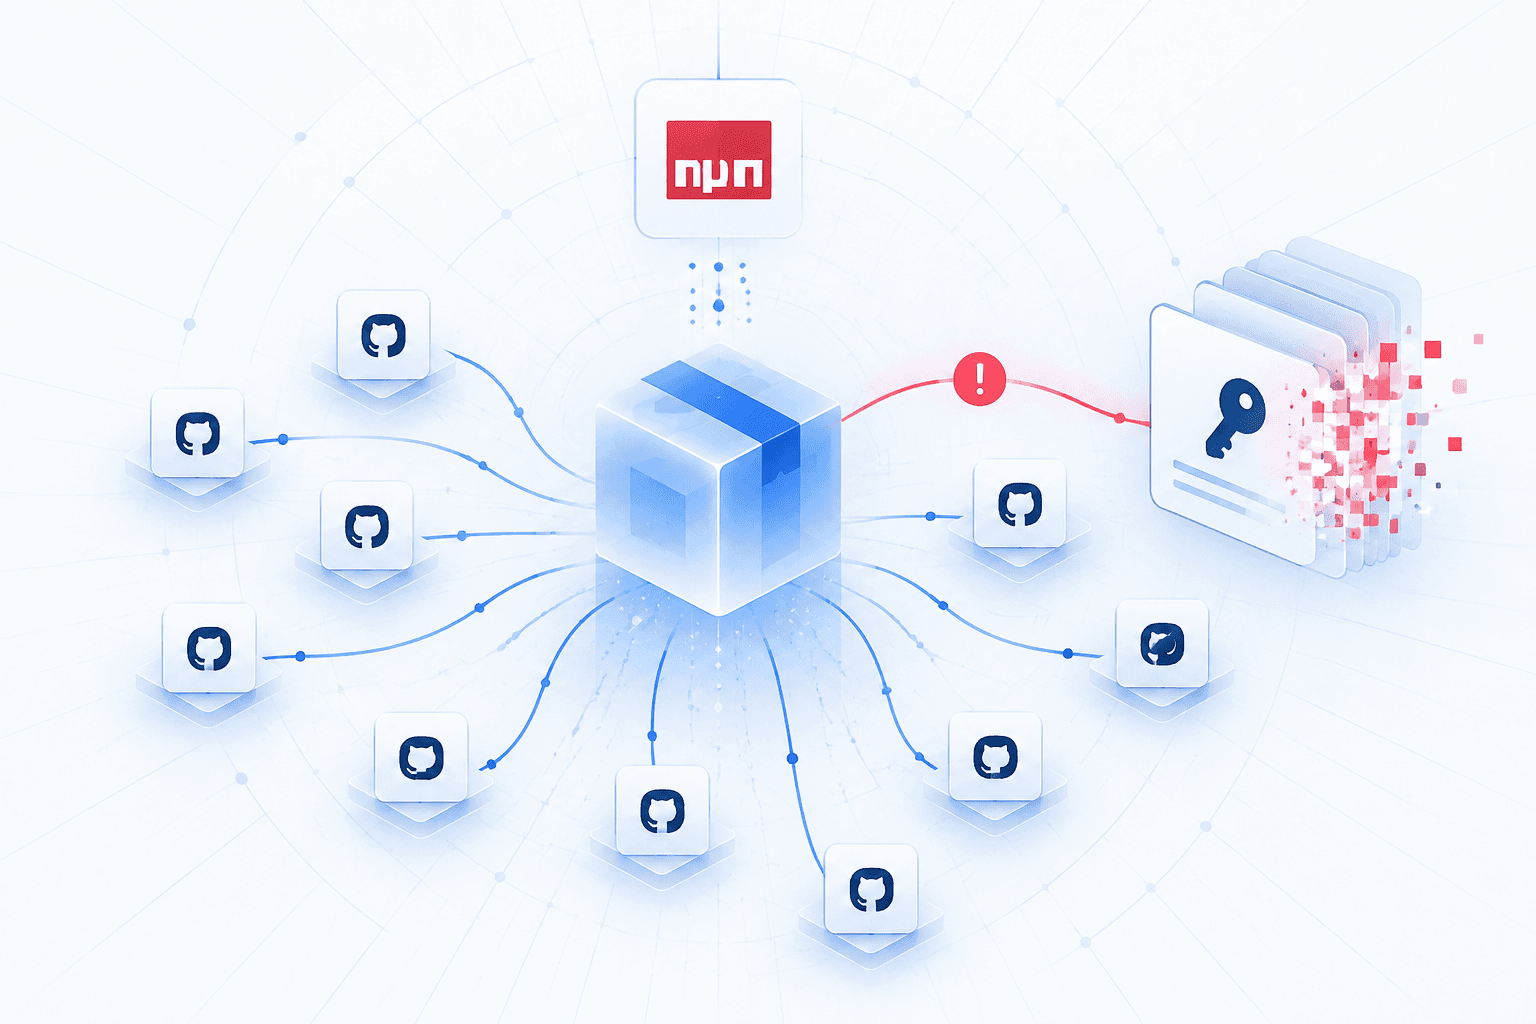
The testmetest npm worm campaign armed 42 GitHub repositories belonging to 11 owners, according to JFrog findings reported October 26, expanding the known scope beyond the operator’s test accounts. SafeDep identified 18 malicious npm packages published through the accounts alexjoipamiba, testnewtestme, and iobandamwer; three iobandamwer packages still had malicious latest versions as of October 26. The Miasma-family malware steals developer, cloud, CI/CD, and AI-tool credentials, exfiltrates data through GitHub repositories or aiarmor[.]website, and spreads through package registries, repositories, and SSH-accessible hosts. SafeDep’s earlier finding of no third-party compromises was explicitly limited to October 22, before the broader repository findings.
The campaign shifted from a binding.gyp execution trigger to a postinstall script loading a native Node.js addon, while also planting execution hooks for AI coding assistants and development tools. Polymorphic payload wrappers measuring 12.9–13.7 MB helped evade GitHub search and common discovery methods. A persistence component named net-health-checker checks a stolen GitHub token every 45 seconds for 48 hours and attempts to delete the user’s home directory if the token returns HTTP 401 or 403. Defenders should detect both installation triggers and account for this destructive mechanism when coordinating containment and credential revocation. JFrog also linked the campaign’s GitHub infrastructure to an operation targeting the cPanel and WHM authentication-bypass flaw CVE-2026-41940, but downstream cPanel compromises were not confirmed. The worm’s exact lineage and attribution to the original Miasma operators remain unestablished.