Microsoft Issues Emergency Trust Updates After eMudhra CA Key Compromise
Patch & Detection Intelligence · 13 sources · Updated 3h ago · First seen Oct 27, 2026
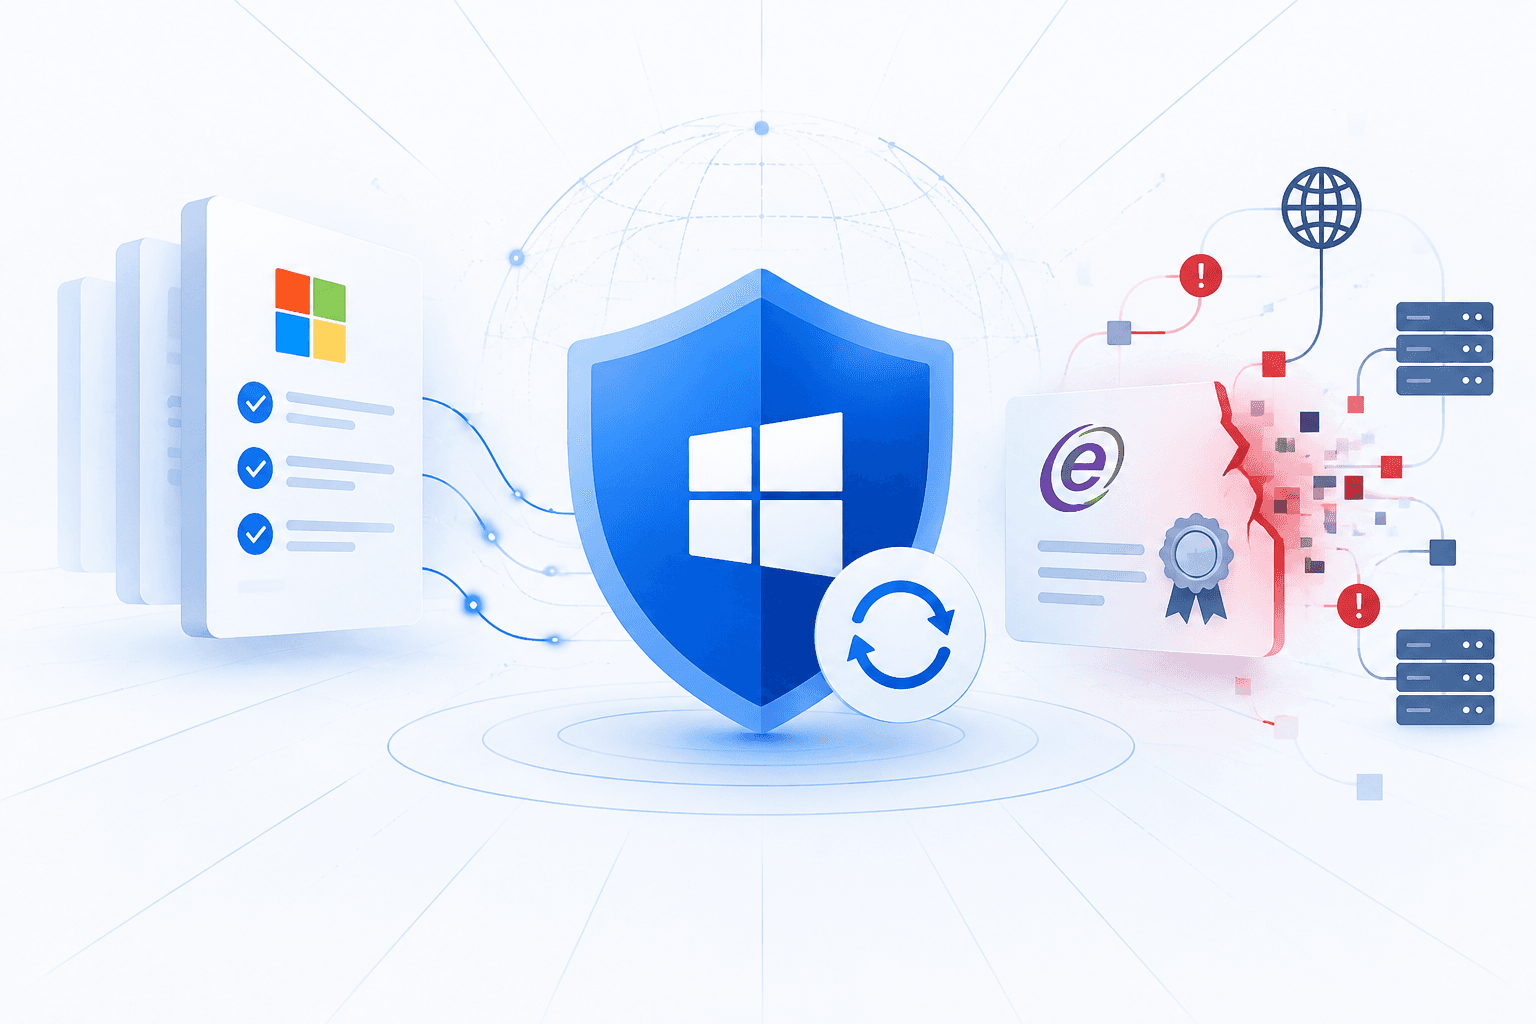
Microsoft released out-of-band Windows updates to remove trust in seven certificates associated with compromised eMudhra certificate authority hierarchies: six eMudhra G3 roots and an AAA Certificate Services cross-sign. The action follows disclosure of eight intermediate CA certificates issued with dangerously weak P-384 private keys, affecting six TLS intermediates and two code-signing intermediates. Researchers reported that some key values were below 256, including one equal to 4, making recovery trivial and potentially enabling forged HTTPS certificates, interception of encrypted traffic, and malicious software signing. The cited research reported no known exploitation in the wild.
The Windows updates primarily protect disconnected systems and devices with automatic certificate trust-list updates disabled. Microsoft also blocked affected certificates through its Windows Disallowed Certificate Trust List and released a separate CRLSet update for Edge and WebView2. Administrators should prioritize disconnected devices, update application-specific trust stores and runtimes, and identify dependent certificates requiring replacement. HCL separately disclosed outbound TLS spoofing risks in Notes Client (CVE-2026-108015) and Domino Server (CVE-2026-108014), referencing advisories KB0134749 and KB0134742; browser protections alone do not resolve these application exposures. Although classified as non-security releases, the Windows updates include the October 13 update and inherit its known issues, including VPN problems and potential on-premises Exchange disruption, warranting deployment testing.