Microsoft Moves TPM Duties Away From Pluton on New AMD and Qualcomm PCs
Patch & Detection Intelligence · 3 sources · Updated 4d ago · First seen Oct 27, 2026
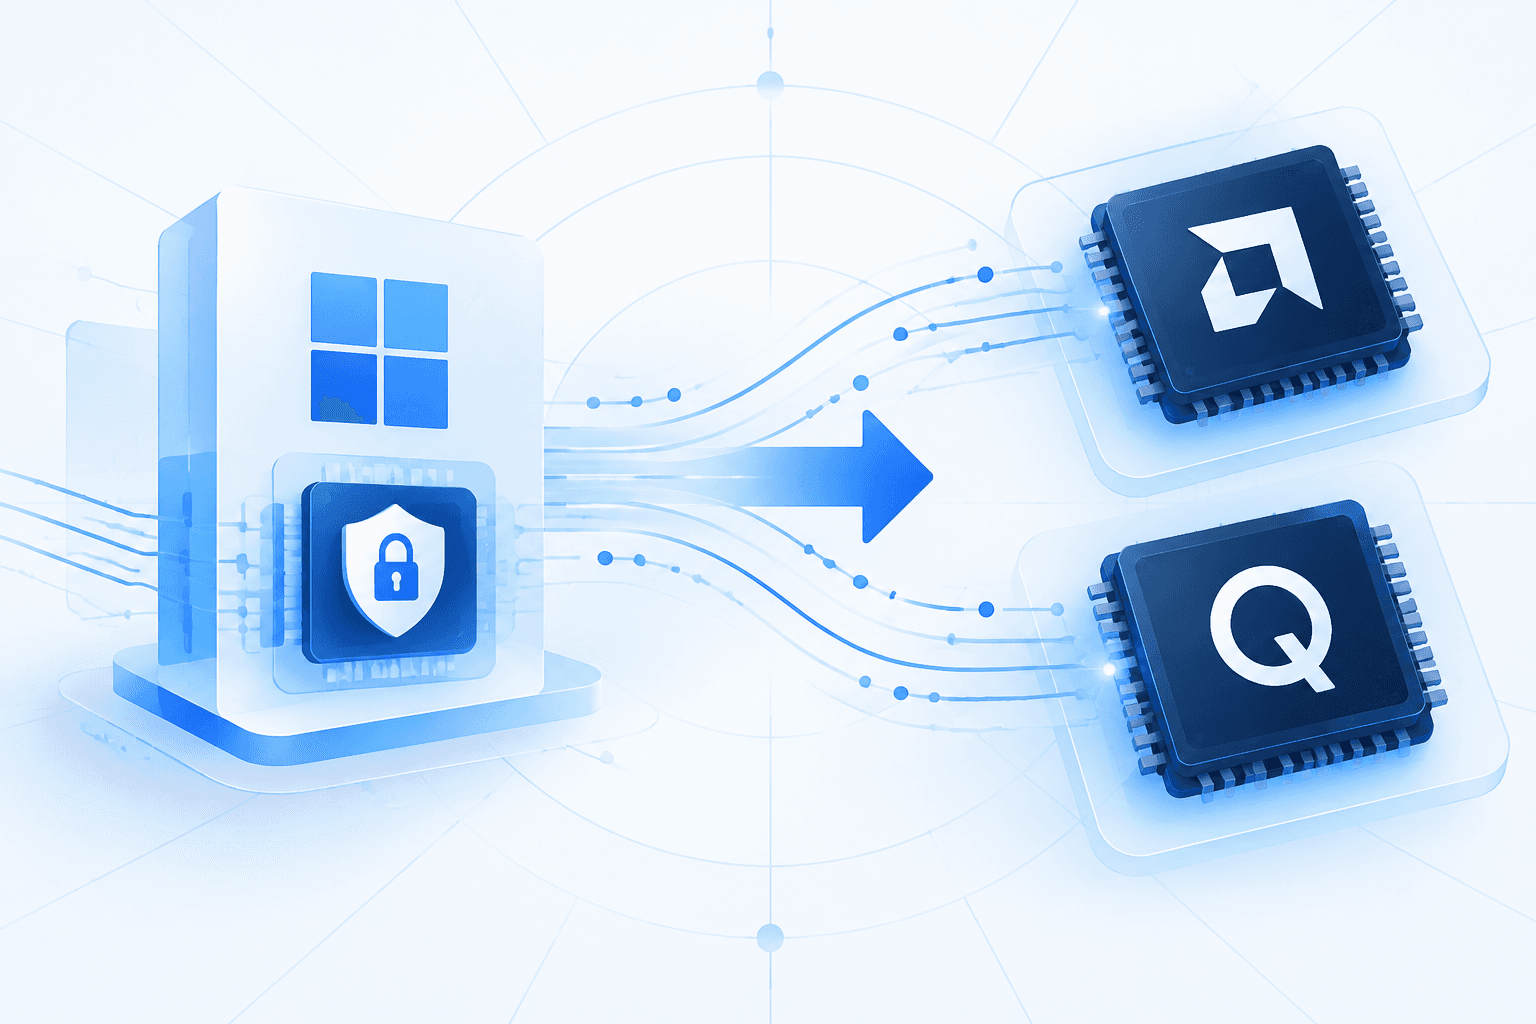
Microsoft says Pluton will stop providing Trusted Platform Module functionality on AMD and Qualcomm platforms beginning with 2026 silicon, with those systems instead relying on vendor firmware TPMs or discrete TPM chips. Pluton will remain available as a hardware-isolated security environment, and existing AMD and Qualcomm devices using it as their TPM will remain supported. Windows 11 still requires TPM 2.0, and BitLocker and Windows Hello will continue operating normally. Microsoft has not explained the decision or precisely identified which processors fall within the new policy.
The principal security-management implication is a change in how TPM vulnerabilities are patched. Microsoft documents Pluton as a CPU-integrated security processor supporting root of trust, secure identity, attestation and cryptographic services, with firmware updates deliverable through Windows Update. Vendor firmware TPM fixes generally depend instead on BIOS updates distributed by PC manufacturers, making OEM support and deployment timelines more important. Security teams should verify the TPM implementation in newly purchased AMD and Qualcomm systems, confirm firmware-update responsibilities and ensure BIOS updates are covered by vulnerability-management processes rather than assuming Windows Update handles TPM remediation.