Malicious Firefox Add-ons Impersonate Phantom, Jupiter and Bitget to Steal Wallet Secrets
Malware Intelligence · 4 sources · Updated 12h ago · First seen Oct 27, 2026
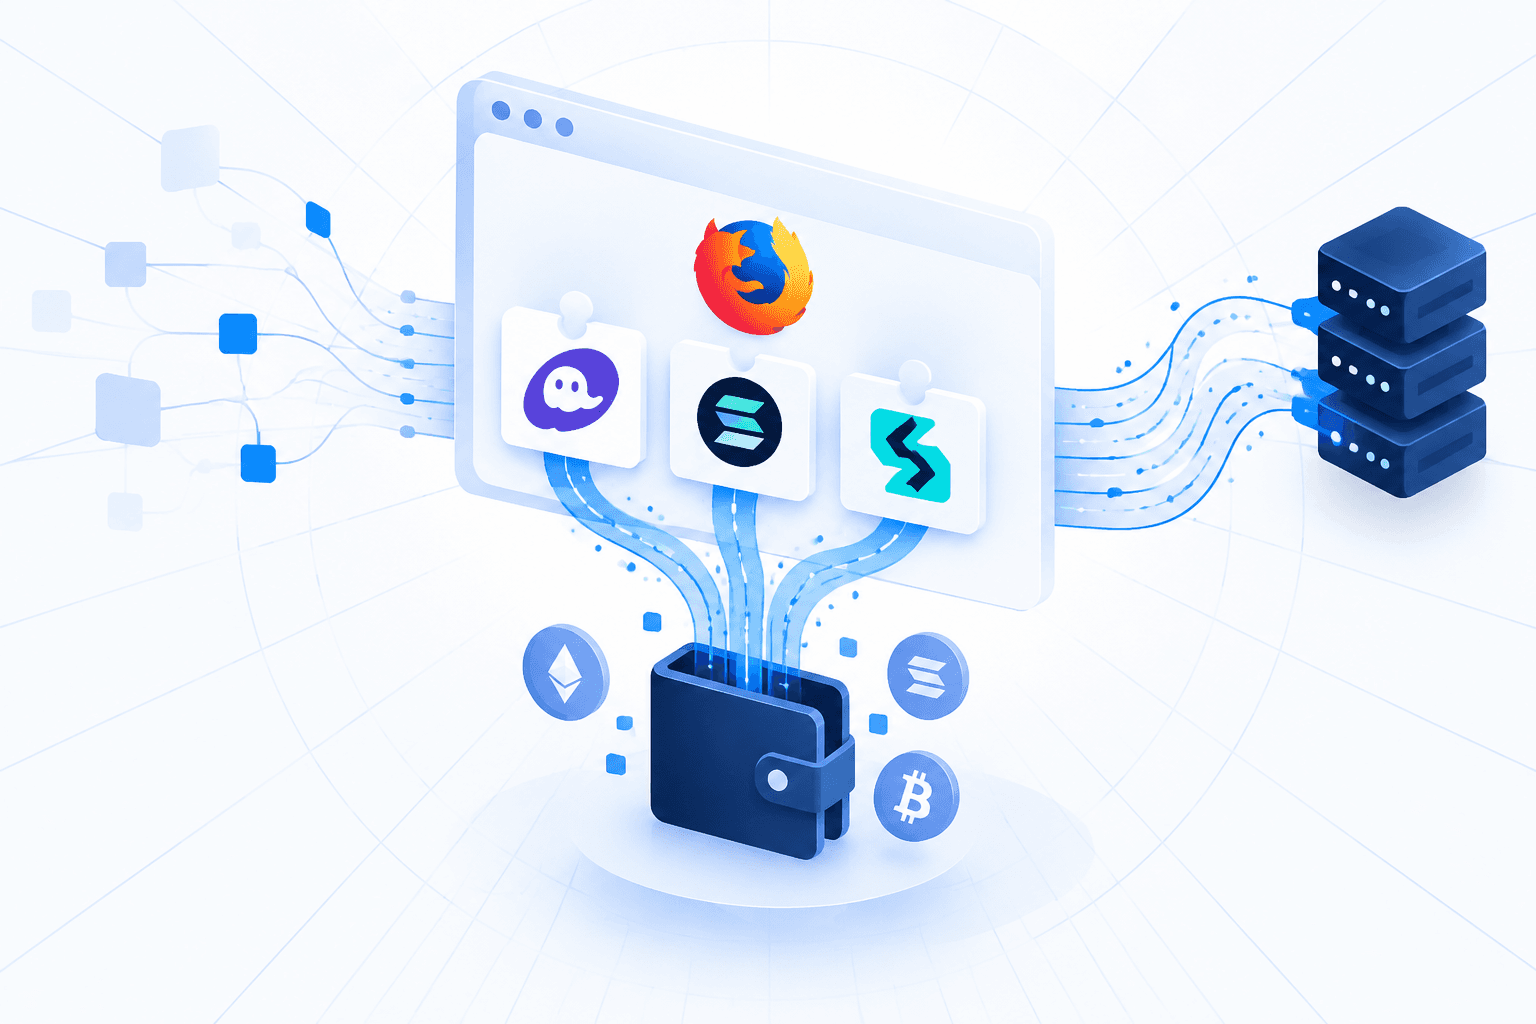
Socket identified three malicious Firefox extensions impersonating Phantom, Jupiter and Bitget wallets to steal recovery phrases and private keys through attacker-controlled subdomains of bonto[.]io. All three signed packages contained operational stealers; the Phantom impersonator also fetched remotely controlled code and injected it into browser pages. Its package included backend code capable of forwarding stolen secrets to Telegram and draining cryptocurrency wallets across multiple blockchains, although reported financial losses were not independently verified.
The extensions used copied branding, Unicode homoglyphs and separate developer accounts to appear legitimate, with apparent ratings manipulation also observed for the Phantom impersonator. Review-evasion code and additional wallet-branded subdomains suggested a coordinated operation, but plans for further impersonators remained unconfirmed. All three listings had been removed from the Firefox Add-ons store by Socket’s October 27 publication. Defenders should block bonto[.]io and its subdomains and hunt for the malicious extensions; users who entered wallet secrets should move assets to a newly created wallet on a clean device.