Critical EDK II PXE Boot Flaw Enables Potential Pre-OS Code Execution
Vulnerability Disclosure · 8 sources · Updated 44m ago · First seen Oct 28, 2026
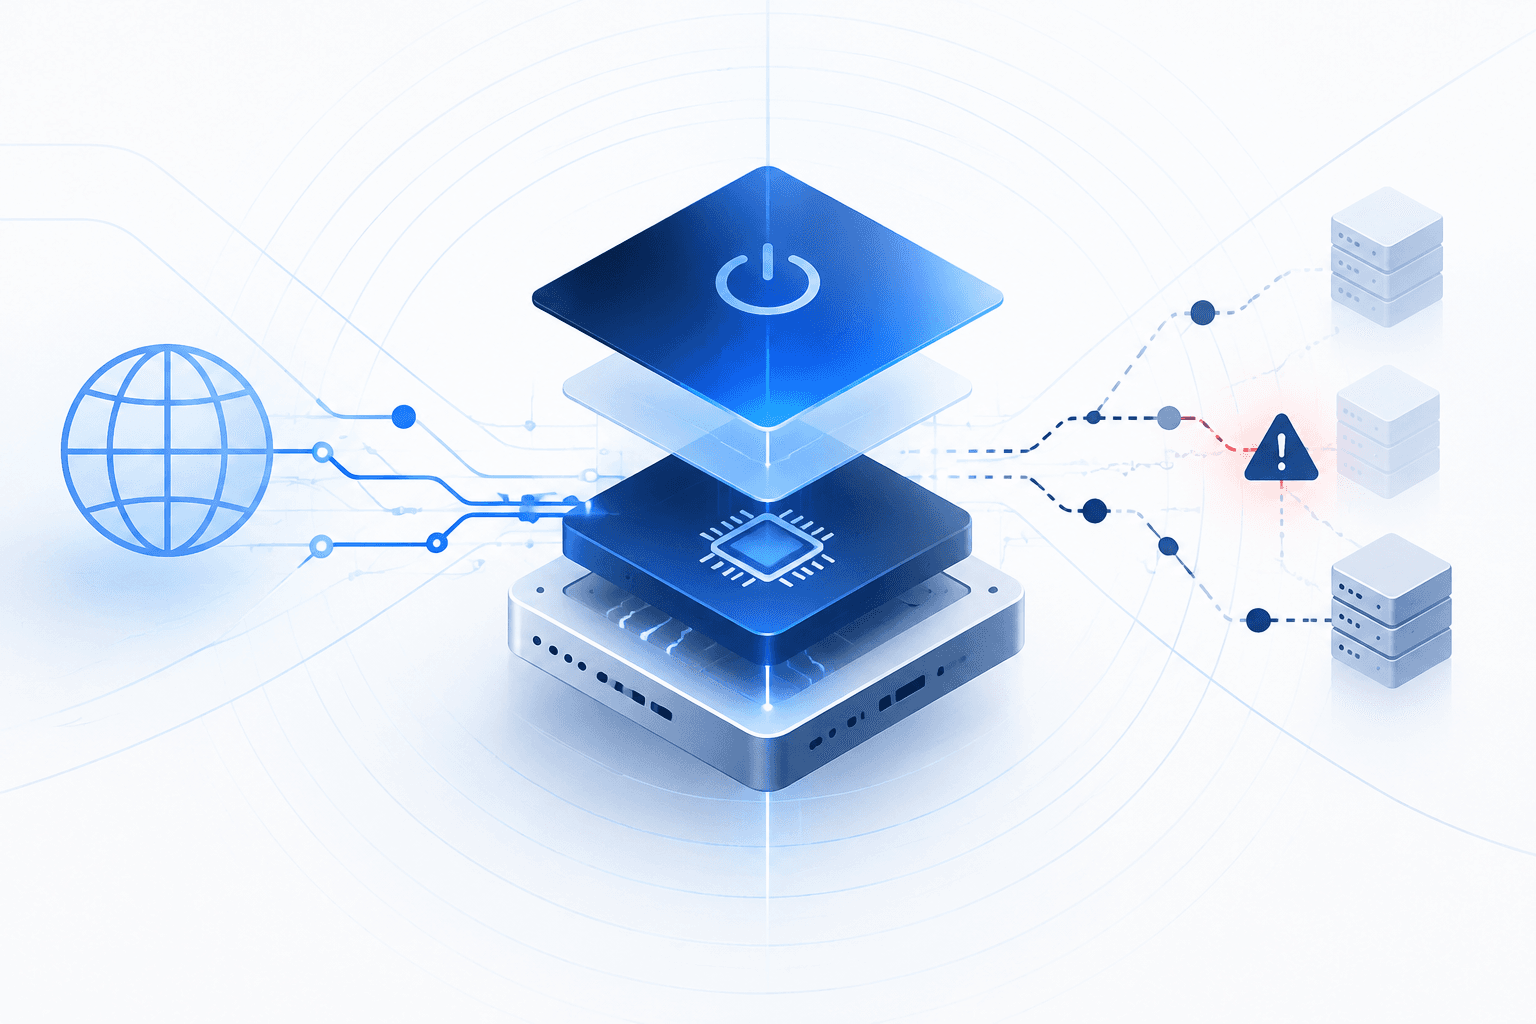
A critical buffer-overflow vulnerability in EDK II’s UefiPxeBcDxe network-boot driver could allow an unauthenticated attacker to crash affected systems or potentially execute highly privileged code before the operating system starts. Tracked as CVE-2026-97631, with a reported CVSS v4 score of 9.5, the flaw involves IPv4 and IPv6 ICMP error-message handling during PXE boot. Exploitation requires delivering a crafted message while the system is network-booting; code execution additionally requires knowledge of the exact firmware build. Systems booting solely from local disks are not exposed through this attack path.
Maintainers merged a fix on October 15, ahead of an October 22 advisory, but downstream firmware vendors must integrate and distribute the correction. The precise affected products and deployment scale remain unclear, despite potentially broad exposure across servers, desktops, and laptops using affected EDK II-derived firmware. Intel said no currently supported commercial products were known to be affected, while Arm said the flaw was not directly applicable to its portfolio; connections to EDK II alone do not establish exposure. Organizations should identify PXE-enabled systems, seek vendor-confirmed firmware updates, isolate provisioning networks, filter unexpected ICMP error messages, and disable unnecessary PXE boot.