MR ROBOT Android Malware Service Steals Banking OTPs and Diverts Verification Calls
Threat Actor Intelligence · 5 sources · Updated 8d ago · First seen Oct 28, 2026
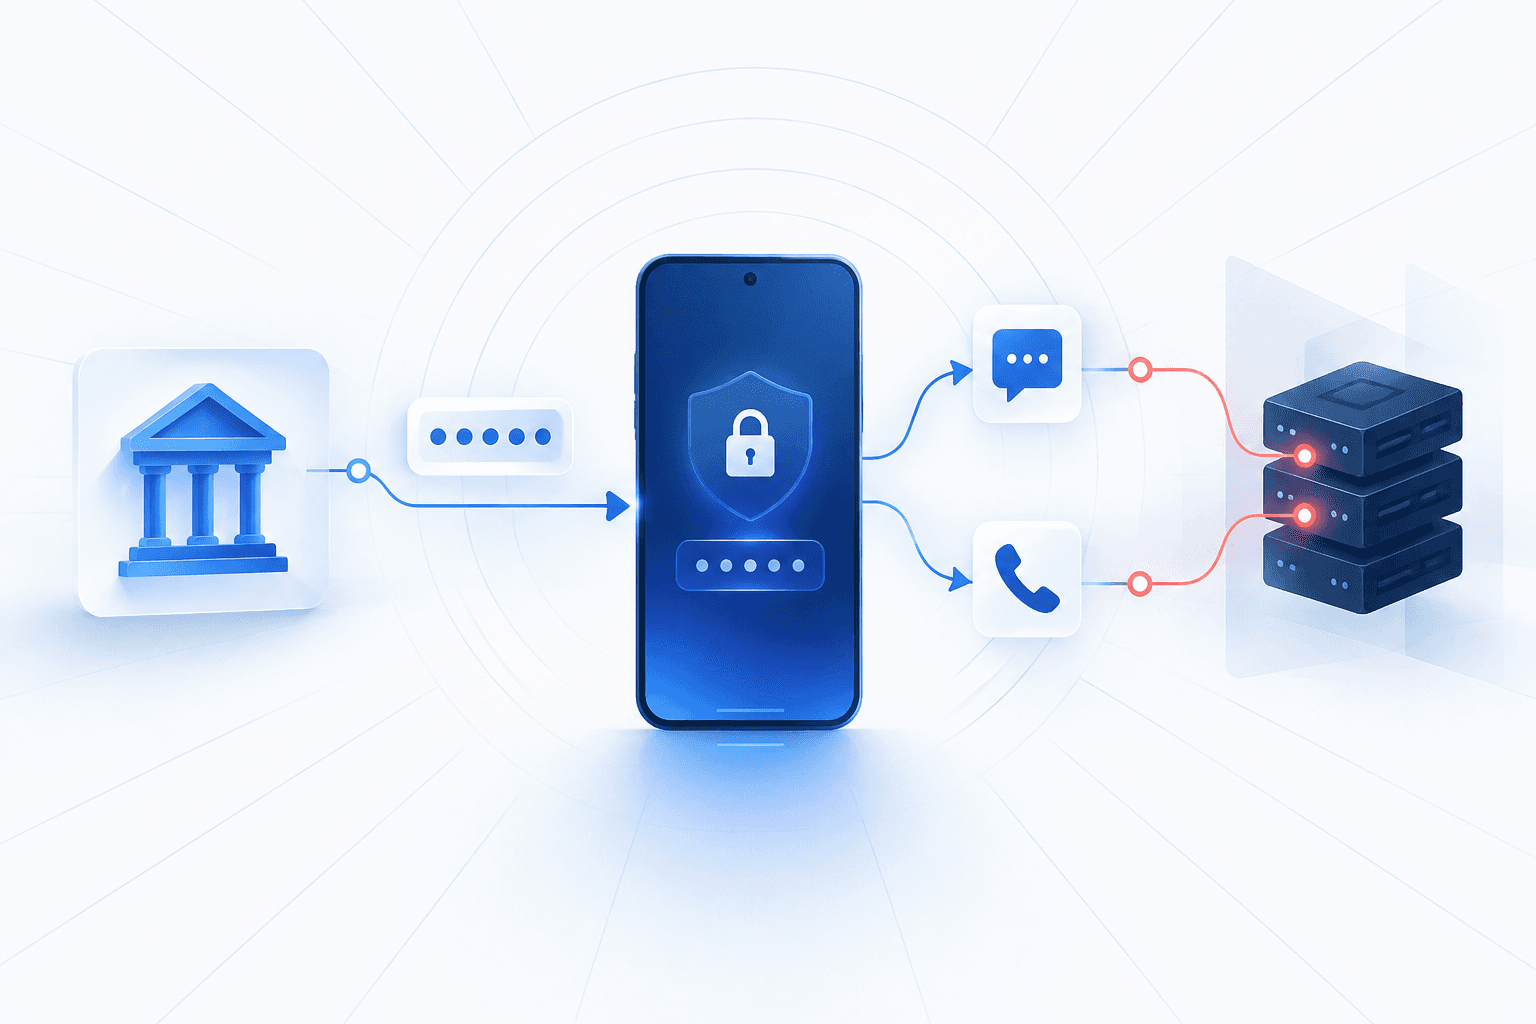
MR ROBOT, an Android malware-as-a-service operation investigated by CloudSEK, rents customizable banking trojans to criminals targeting Indian bank customers. Affiliates distribute malicious apps impersonating banks, utilities and government services through fake Play Store-style pages. An APK Shield Telegram bot and version 7.0 web panel support personalized malware generation and subscription-based affiliate management. The malware steals SMS messages, one-time passwords, financial credentials and identity information, while silently enabling unconditional call forwarding to divert calls, including banks’ fraud-verification callbacks.
Researchers observed approximately 154 enrolled devices in one affiliate’s panel; a separate affiliate’s exposed Firebase database held 5,407 intercepted SMS messages from 153 infected devices collected between July 16 and 30, 2026. Individual affiliates reuse a Firebase backend across multiple lures, creating an opportunity for coordinated backend takedowns. Similarities to FatBoyPanel and RedWing suggest possible shared lineage but do not establish attribution. CloudSEK recommended avoiding bank-branded apps distributed through messaging links and moving customers toward app-based or FIDO authentication where feasible.