UAT-11473 Exploits Cisco SD-WAN Authentication Bypass to Deploy KeyDrift Malware
Active Exploitation · 8 sources · Updated 4m ago · First seen Oct 28, 2026
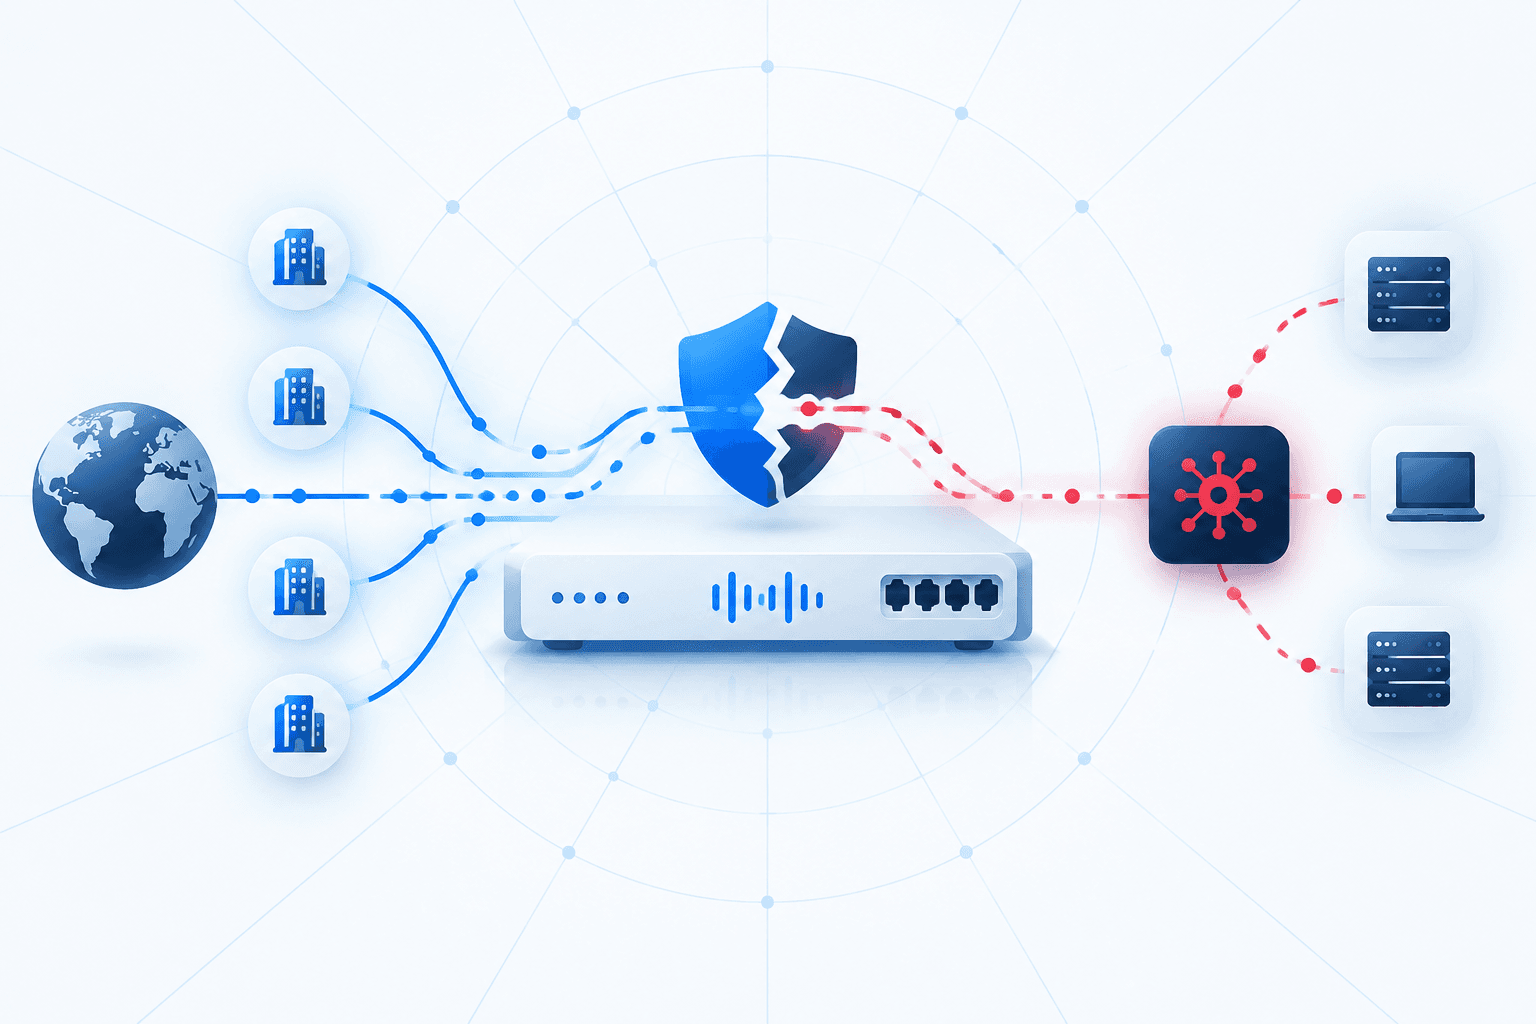
Cisco Talos identified UAT-11473 exploiting CVE-2026-20127, an authentication bypass vulnerability in Cisco Catalyst SD-WAN Controllers, to deploy the custom KeyDrift malware framework. Observed targets include space and satellite services, defense and aerospace technology, and policy research organizations. KeyDrift embeds within legitimate controller processes to maintain persistent access, execute commands, relay command-and-control traffic, and extract sensitive keying material from decrypted control-plane communications.
Talos assesses with high confidence that UAT-11473’s infrastructure substantially overlaps with Volt Typhoon’s Silent Train covert access network, but the findings do not establish that the actors are identical. Cisco has released patches. Organizations operating affected controllers should prioritize updates, apply Cisco’s deployment-hardening guidance, and investigate indicators of post-compromise activity rather than treating patching alone as evidence that systems are clean.