NetamLoader Targets Government-Customized Windows in Suspected Supply-Chain Attack
Malware Intelligence · 5 sources · Updated 18d ago · First seen Sep 27, 2023
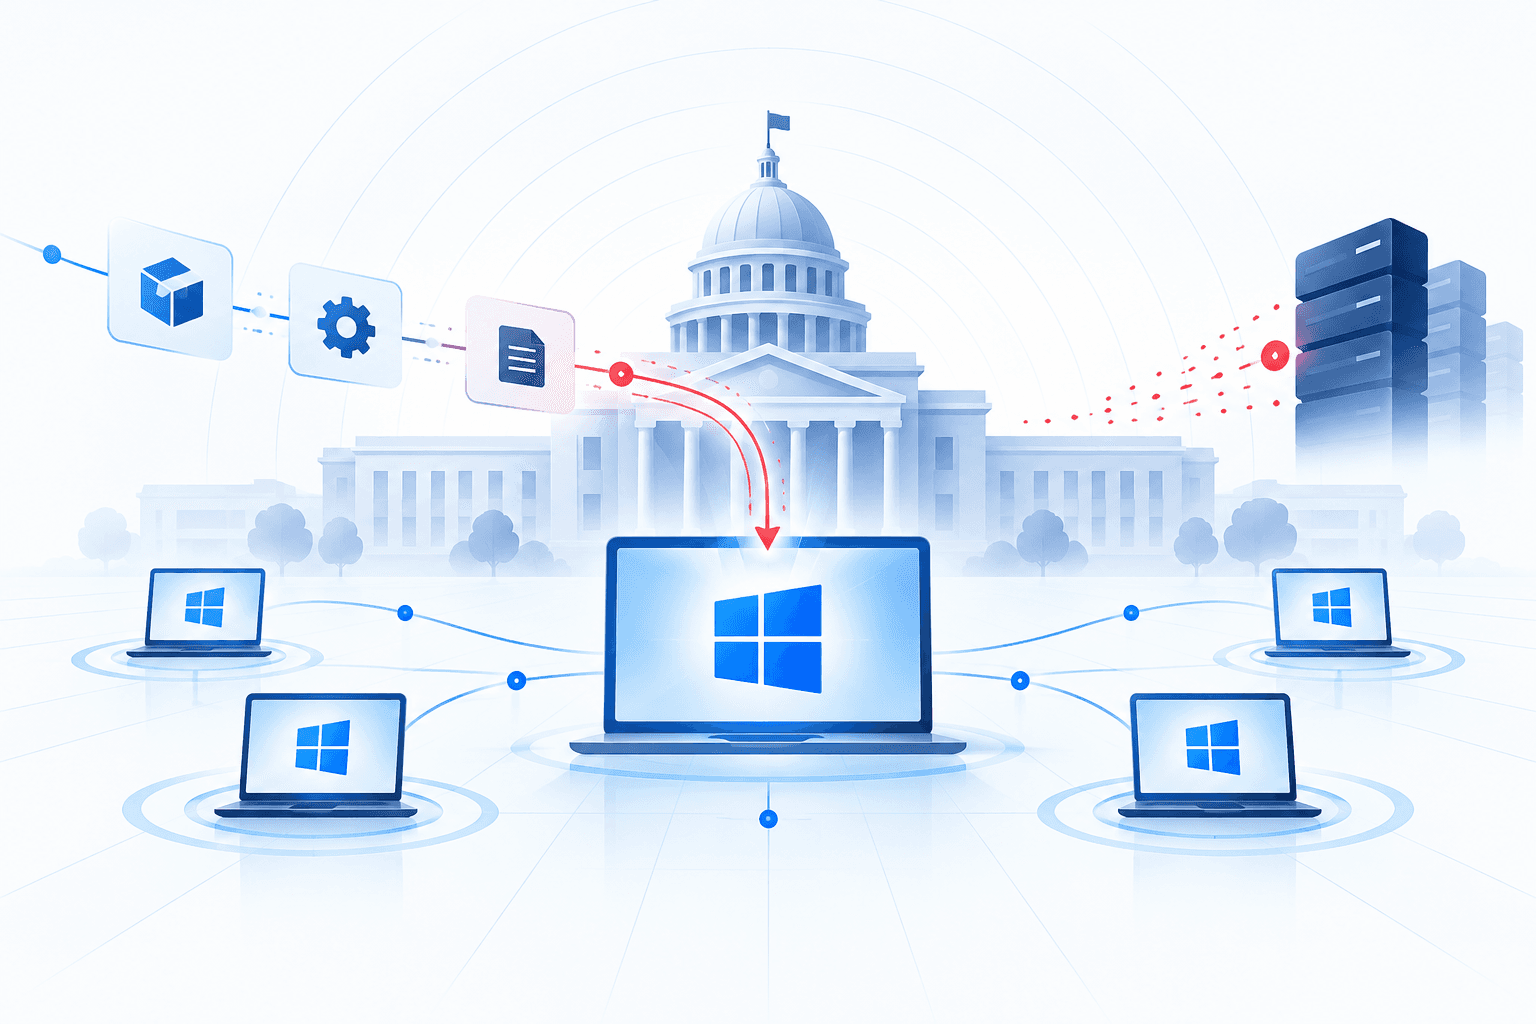
Kaspersky discovered NetamLoader, a multilayer .NET loading framework, in the first half of 2026 and assessed that it was likely deployed through a supply-chain attack targeting a customized Windows 10 build reserved for Asian government entities. Researchers identified one victim in Asia but did not establish how the initial archive was delivered or attribute the operation to a known APT group. The infection chain abuses a legitimate Patch My PC executable, Microsoft-signed assemblies, configuration files, unsafe deserialization, and XAML to load malicious code.
NetamLoader combines AMSI bypasses, suppression of .NET telemetry, forensic artifact removal, and delayed execution to evade detection. It also transfers execution into dllhost.exe through COM-based deserialization. Its final plugin communicates with openaigpt4v[.]com using encrypted, authenticated traffic and executes downloaded XAML in isolated application domains. Defenders supporting affected government environments should investigate this domain and unusual Patch My PC, .NET, and dllhost.exe activity; the suspected supply-chain delivery mechanism remains unconfirmed.