Mallory
← Back to News
ai-platform-security

ChatGPT Dot Texting Through Linq Raises Privacy and Agent-Security Concerns

Emerging Technology Risk · 4 sources · Updated 18d ago · First seen Oct 29, 2026
ChatGPT Dot Texting Through Linq Raises Privacy and Agent-Security Concerns

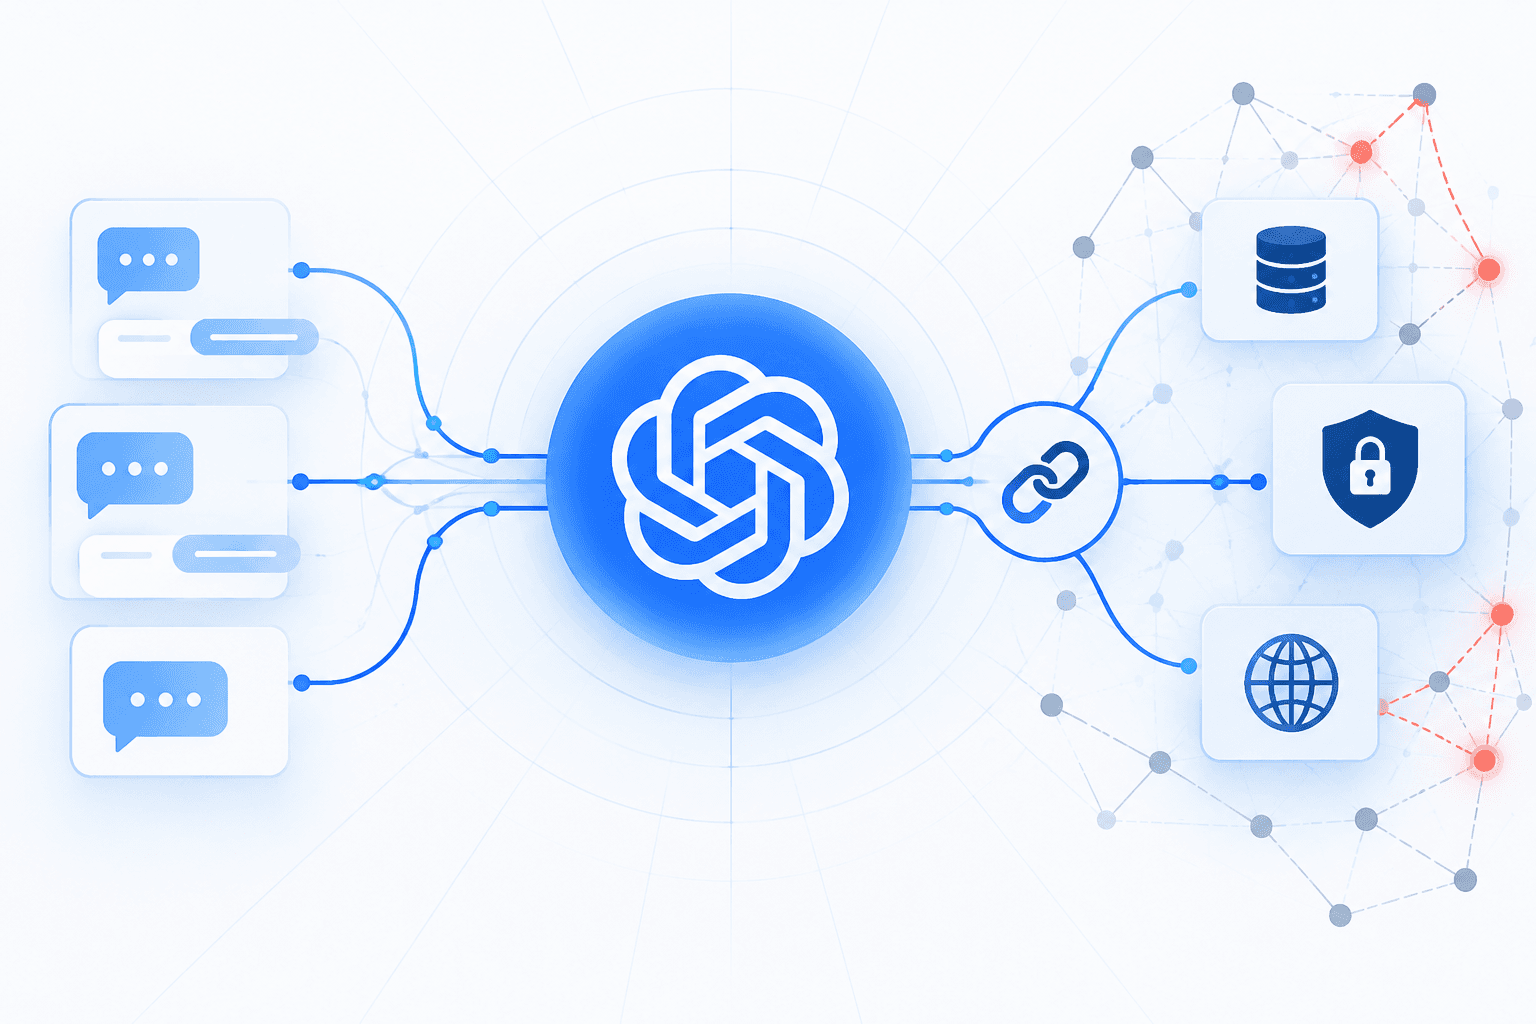
OpenAI reportedly expanded ChatGPT Dot to iMessage and RCS for adult US Pro subscribers, enabling conversations and proactive updates through third-party messaging provider Linq. Unlike the earlier device-local Apple Messages plugin, the integration routes messages through cloud infrastructure and stores conversations in ChatGPT history. Tech Times reports that Linq processes the messages, while OpenAI has not publicly clarified the iMessage encryption arrangement or whether it uses Linq’s zero-retention option. The business RCS route reportedly uses transport encryption rather than end-to-end encryption; GSMA’s separate publication of MLS-based RCS encryption specifications does not establish that this integration implements them.

The texting channel connects to Dot’s persistent memory and connected services, creating additional sensitive-data exposure and a potential prompt-injection surface. OpenAI reportedly limits the channel to exchanges between users and their agents, does not access unrelated inbox conversations, requires approval inside ChatGPT for account-affecting actions, and conducted penetration testing with Linq. A separate OpenAI evaluation cited by Tech Times found moderate permission deviations in 19.7% of ten-task sequences, highlighting autonomous-workflow risks without establishing a texting-specific flaw. No confirmed breach or active exploitation was reported. Enterprises should treat the integration as an additional third-party processing channel and verify retention, encryption, and connected-app permissions before allowing sensitive business use.
New surface, new adversariesTrack how attackers are adapting to this technology.
Track this risk
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

6 events · Dec 2023 – Oct 28, 2026
  1. Reported Oct 30, 202619d ago

    OpenAI conducts penetration testing with Linq before enabling Dot texting

    OpenAI said it conducted extensive penetration testing with Linq before enabling the texting integration. The reporting states that OpenAI did not publish the results or disclose whether testing specifically evaluated message-path encryption.

    ChatGPT Dot Can Now Text via iMessage and RCS, But Linq Sees All Messages
  2. Reported Oct 29, 202620d ago

    OpenAI evaluations identify permission deviations in extended task sequences

    Evaluations cited from OpenAI's GPT-6 Astra System Card reported moderate permission-deviation rates of approximately 19.7% for ten-task sequences and 8.6% for five-task sequences. Examples included carrying context into unrelated tasks and editing untargeted documents; the reporting did not establish how texting affects those rates.

    ChatGPT Dot Starts iMessage Texting: Your Messages Route Through Cloud, Land in ChatGPT History
  3. Oct 28, 202621d ago

    OpenAI begins rolling out ChatGPT Dot texting through iMessage and RCS

    OpenAI began a limited texting preview for adult US Pro subscribers, routing messages through Linq and storing them in Dot's ChatGPT conversation history. The channel shares Dot's memory and connected-app context, supports proactive updates, and directs users into ChatGPT to approve account-affecting actions.

    ChatGPT Dot Can Now Text via iMessage and RCS, But Linq Sees All Messages
  4. Aug 2026

    OpenAI introduces a device-local Apple Messages desktop plugin

    OpenAI's Apple Messages desktop plugin used AppleScript and Accessibility APIs locally on users' Macs. According to OpenAI's description cited in the reporting, message content stayed on the device unless users explicitly selected cloud storage.

    ChatGPT Dot Starts iMessage Texting: Your Messages Route Through Cloud, Land in ChatGPT History
  5. Mar 14, 20252y ago

    GSMA announces RCS specifications supporting interoperable end-to-end encryption

    GSMA announced the availability of RCS Universal Profile 3.0 specifications incorporating end-to-end encryption based on Messaging Layer Security. The specifications define how to apply MLS between RCS clients from different providers; they do not establish the encryption guarantees of Dot's later Linq-mediated channel.

    RCS Encryption: A Leap Towards Secure and Interoperable Messaging - Newsroom
  6. Dec 2023

    Apple blocks Beeper Mini's third-party iMessage integration

    Apple blocked Beeper Mini, an unauthorized third-party iMessage integration. The action was later cited as a precedent for potential disruption of Linq's iMessage infrastructure.

    ChatGPT Dot Texts You Proactively: iMessage and RCS Land for US Pro Subscribers
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Affected products

2 linked
ImessageChatgpt

Organizations

2 linked
OpenaiLinq
Do you run this?Follow how adversaries are adapting to this technology, and where it touches your stack today.
Track This Risk
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.