Android ‘SMS of Death’ Flaw Silently Crashes Telephony and Disconnects Calls
Vulnerability Disclosure · 6 sources · Updated 2h ago · First seen Oct 29, 2026
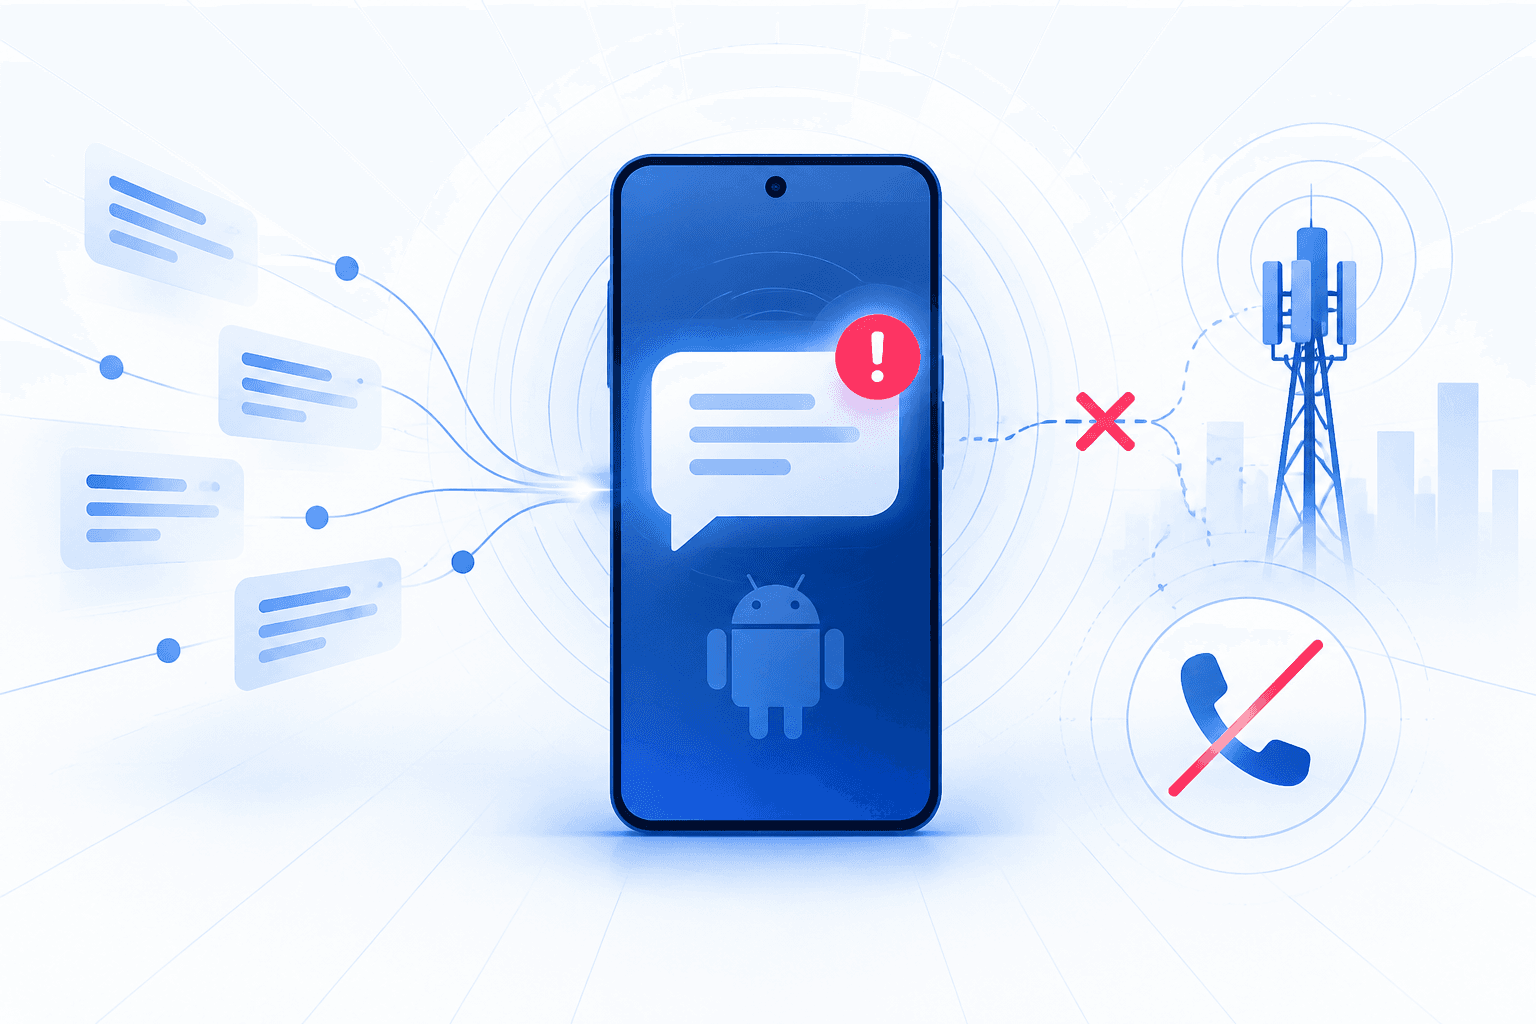
A researcher disclosed “SMS of Death,” a zero-click Android denial-of-service flaw in which a malformed WAP Push SMS silently crashes the telephony process, disconnecting active calls, including emergency calls, without displaying a message. An unchecked conversion of a header length to a signed integer reportedly triggers an uncaught exception that terminates com.android.phone. The researcher reproduced the crash on a Pixel 9 running April 2026 firmware and several Samsung Galaxy and A-series devices. Public claims that all Android phones are affected remain unverified by the supplied evidence.
Carrier retransmissions can reportedly prolong service disruption, while rapid delivery of approximately 30 messages can corrupt the SMS database and trigger recurring telephony crashes after reboot. Recovery reportedly required using a non-Android phone to acknowledge queued messages and clearing corrupted records through Android Debug Bridge (ADB). According to the disclosure, Google classified the report as a non-security issue and marked it “Won’t Fix.” Public proof-of-concept material is available in the MarkBlah/smsofdeath repository, but the references provide no evidence of in-the-wild exploitation or a confirmed patch; organizations should account for potential mobile voice-service outages in emergency communications planning.