Malicious Hugging Face Models Deliver Cryptominers and Backdoors to GPU Hosts
Supply Chain Risk · 2 sources · Updated 15d ago · First seen Oct 31, 2026
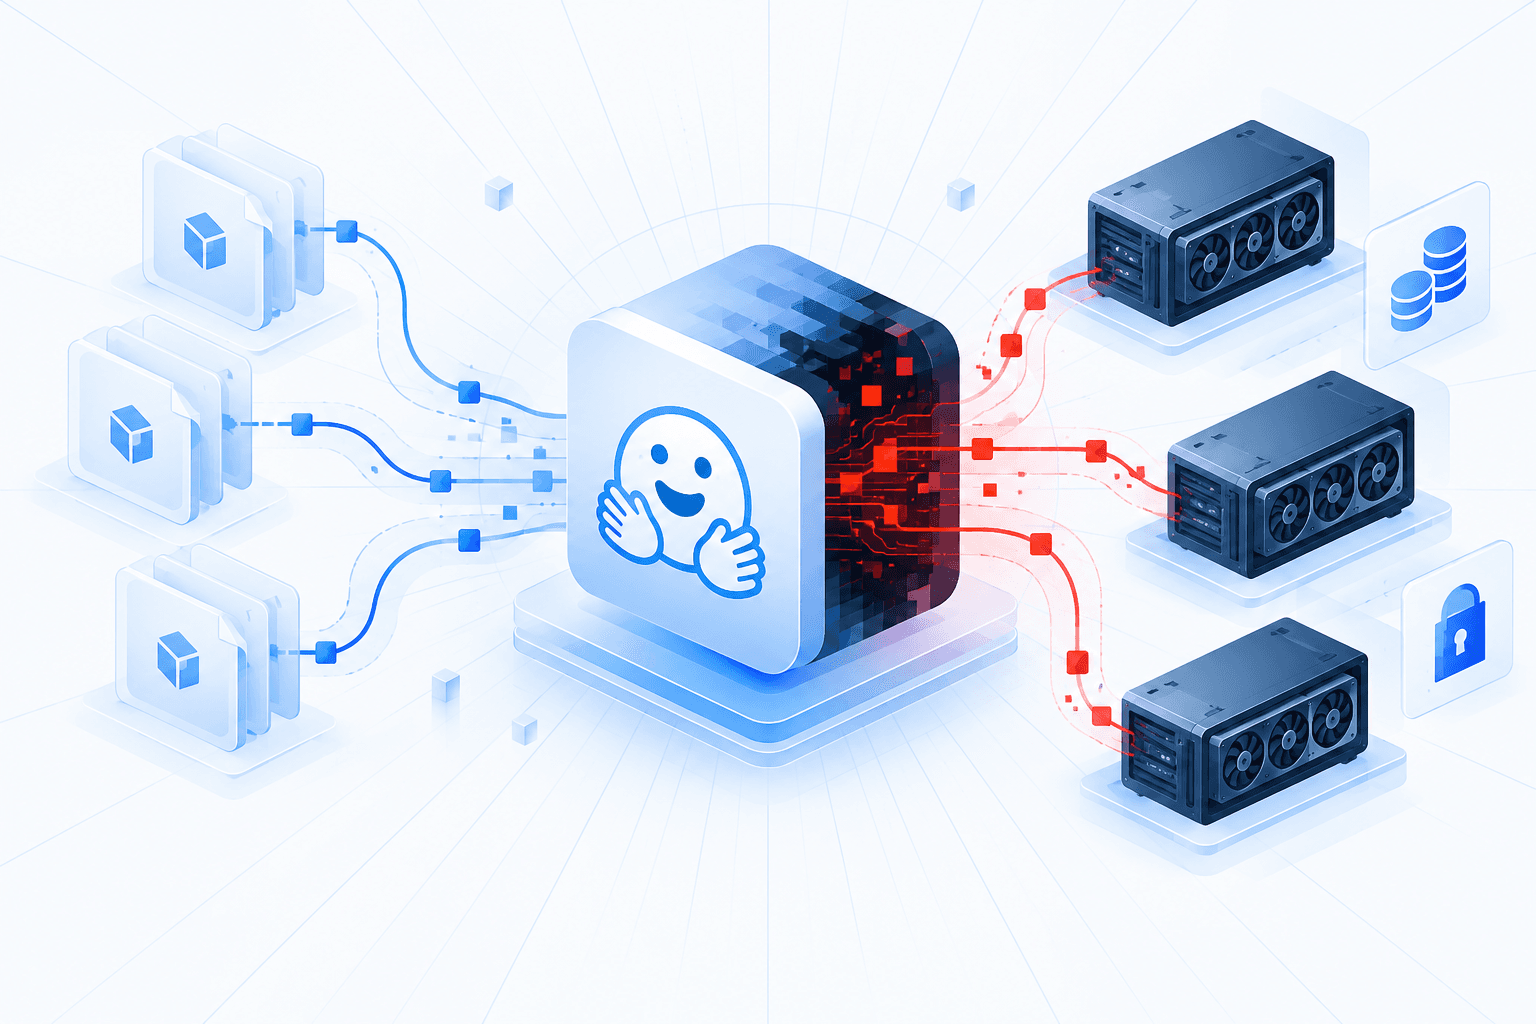
Pluto Research identified a financially motivated campaign distributing cryptominers and backdoors through malicious AI model repositories on Hugging Face and ModelScope. Researchers tracked 31 malicious Hugging Face repositories across seven accounts in two waves; the campaign and linked models collectively recorded more than 32,000 downloads, not confirmed infections or unique victims. The attack abuses Transformers’ trust_remote_code=True option to execute repository-supplied Python with the caller’s privileges before model weights load. Targets include self-hosted inference infrastructure, particularly Xinference and GPUStack, rented GPU machines, shared research notebooks and CI jobs.
Payloads establish persistence, run a miner in memory, disguise processes and, in some cases, provide reverse-shell access. A later repository also contained a container-escape script targeting GPUStack environments. The campaign returned within days of takedown, and 19 second-wave repositories remained live eight days after researchers reported them. Pluto highlighted scanning gaps: the flagship payload passed antivirus checks, while weight-focused scanning did not assess the Python’s behavior. Defenders should review exposure to the reported repositories, restrict remote-code execution to audited model code, and investigate affected GPU hosts for mining activity, persistence and unauthorized access; automatically extracted indicators require validation before operational use.