S3 Bucket Squatting Exposes SageMaker, Athena and EMR Workflows Across AWS Accounts
Vulnerability Disclosure · 6 sources · Updated 6d ago · First seen Nov 2, 2026
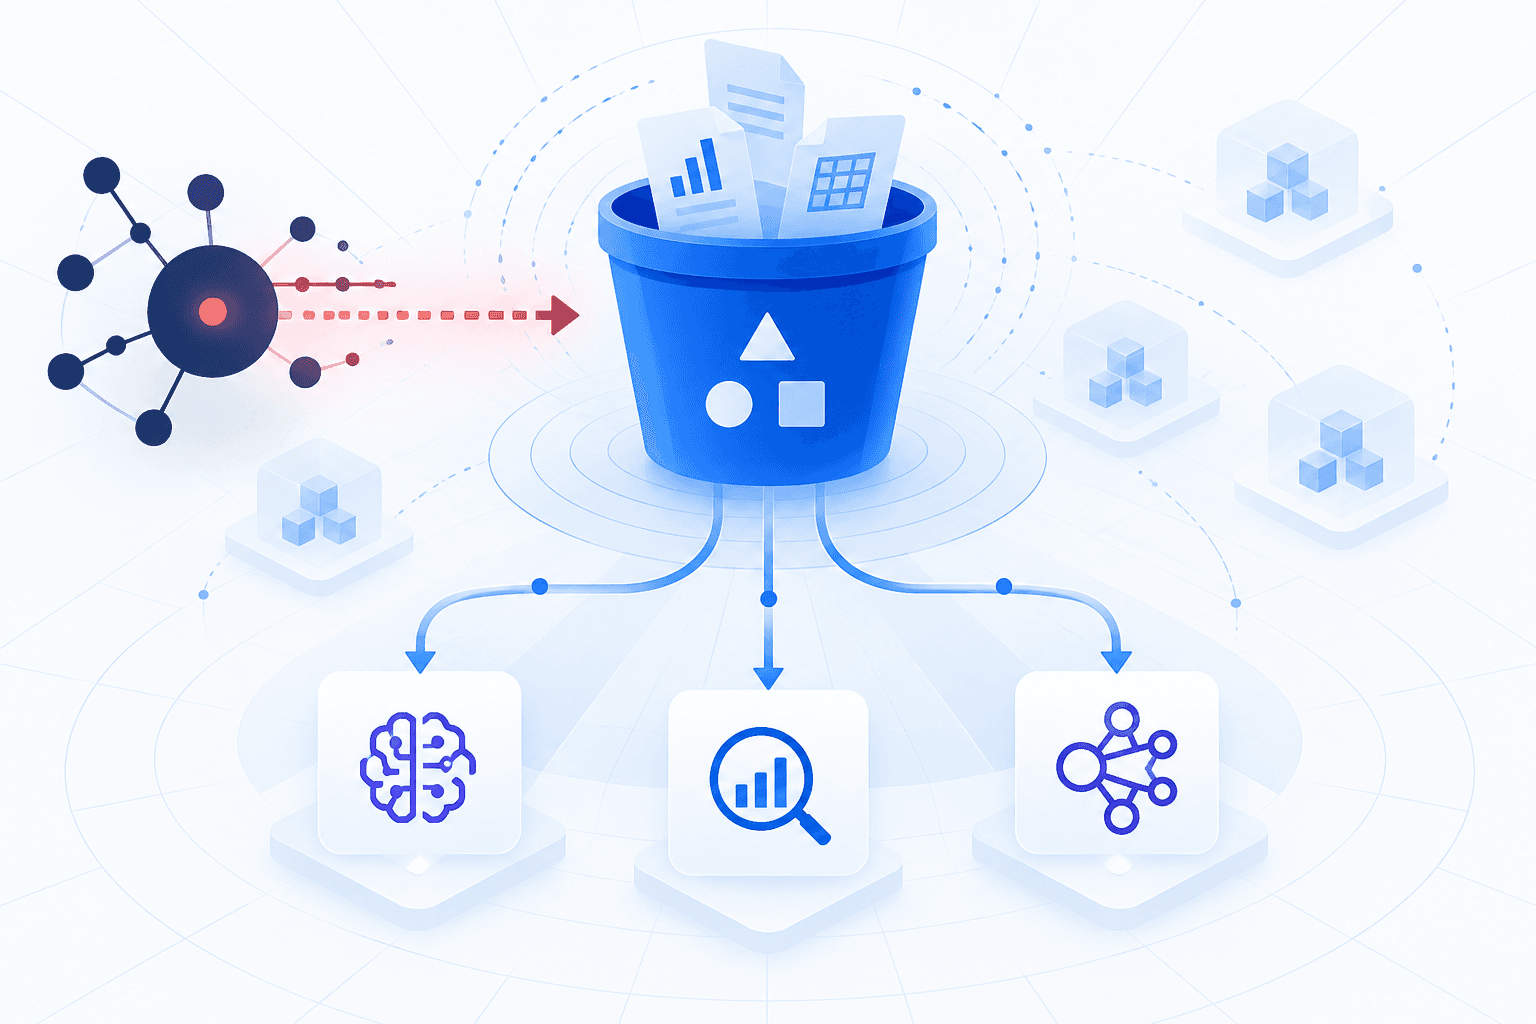
Researchers at Upwind disclosed three S3 bucket-squatting vulnerabilities affecting the SageMaker Python SDK and AWS SDK for pandas (awswrangler), enabling cross-account code execution, data theft and data poisoning. Predictable default bucket names and missing or ineffective ownership checks allowed attacker-owned storage to be accepted by victim workflows. In SageMaker, CVE-2026-112408, rated CVSS 4.0 9.4, enabled demonstrated processing-job and persistent inference-endpoint code injection, including IAM credential exfiltration. In Athena, CVE-2026-118029, rated 5.9, exposed query results and allowed CTAS manifest manipulation to substitute attacker-modified data. EMR logging configurations generated by the pandas library could send sensitive logs to attacker-controlled buckets—even buckets created after cluster startup, because uploads were buffered and retried. An assisted assessment captured approximately 20,000 log files; the reports do not establish malicious exploitation.
AWS addressed the SDK exposures in SageMaker Python SDK 3.10.0, AWS SDK for pandas 3.16.1 for Athena, and 3.18.0 for EMR logging. However, Upwind reported that EMR’s underlying RunJobFlow API still lacked bucket-existence and ownership checks, despite protections in the console. The findings show that earlier service-level mitigations and the introduction of account-namespaced buckets did not protect every SDK and API path. Organizations should upgrade affected libraries, verify bucket ownership in every account and region, replace predictable defaults with explicitly trusted destinations, enforce Athena workgroup result settings where appropriate, and audit workloads for references to buckets outside their accounts.