Attackers Exploit Node-RED Admin API Flaw to Deploy Linux Downloaders and Webshells
Active Exploitation · 19 sources · Updated 2h ago · First seen Nov 2, 2026
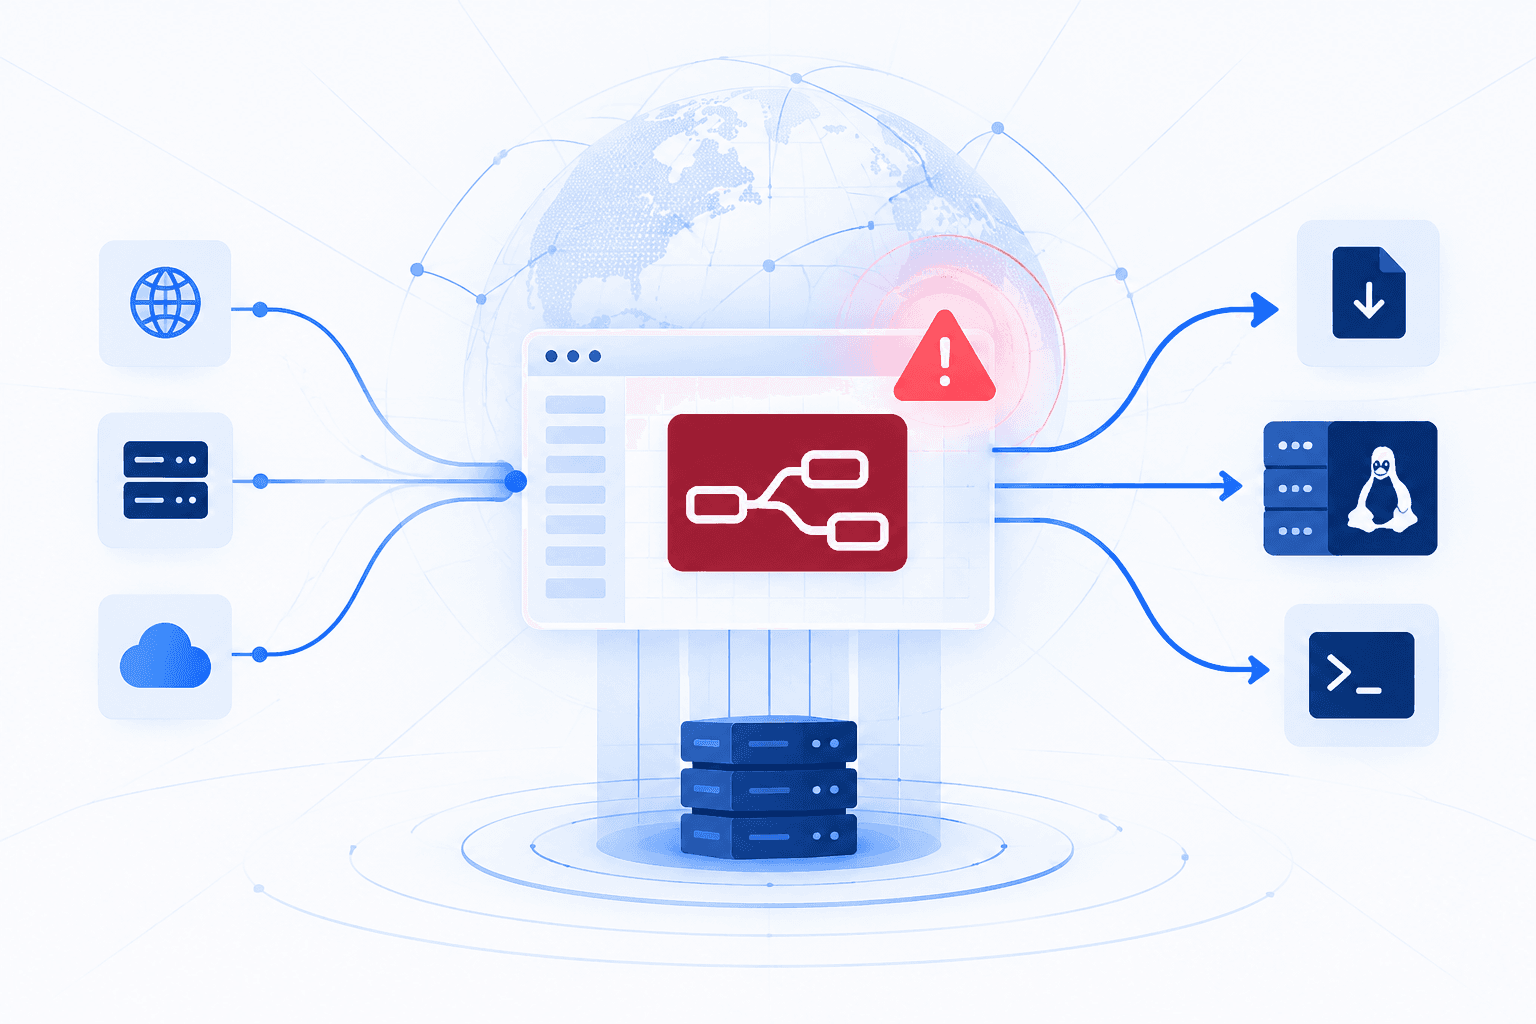
Attackers are exploiting CVE-2026-58115, a CVSS 10.0 unauthenticated Node-RED administrative API vulnerability assigned against Siemens SIMATIC IoT2050, to deploy flows capable of executing system commands. VulnCheck recorded 16 attempts from 4.201.105.116 between October 30 and November 1, following publication of its detection on October 27. The attempts included encoded Linux downloaders and flow-based webshells; one used a single request to the flows API to schedule the download and execution of a purported Linux AMD64 bot from 85.215.73.250:8080. Researchers did not retrieve the payloads, leaving malware capabilities and successful infections unverified.
Node-RED is widely used for workflow automation in ICS/OT environments and embedded in commercial products, making exposed administrative interfaces a significant risk. The attacking address also attempted exploitation against unrelated products, suggesting opportunistic mass scanning rather than a targeted industrial campaign; its Microsoft-hosted network does not establish the operator’s identity. VulnCheck added the flaw to its Known Exploited Vulnerabilities catalog, while reporting that it was not yet in CISA’s catalog. Defenders should identify externally reachable Node-RED instances, restrict administrative access, apply available updates, and inspect deployed flows for unauthorized command-execution nodes and HTTP endpoints.