NCSC Warns AI-Powered Ransomware Is Highly Likely to Target UK Infrastructure by 2028
Emerging Technology Risk · 20 sources · Updated 3d ago · First seen Nov 3, 2026
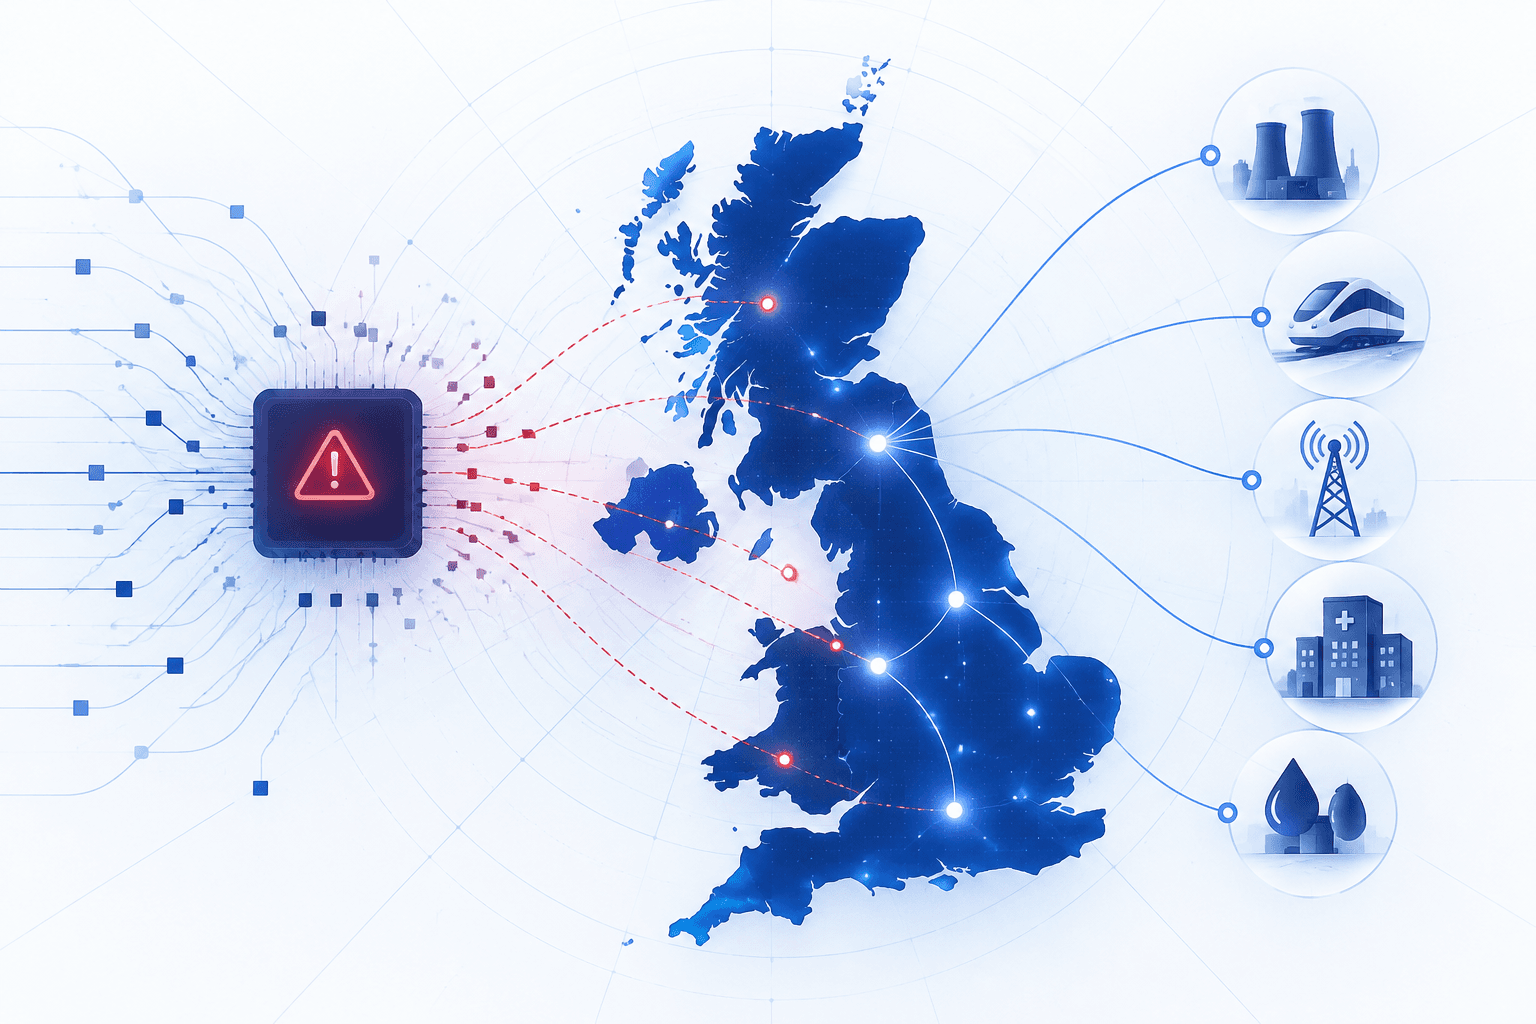
The UK’s National Cyber Security Centre (NCSC) assesses that AI-powered malware is highly likely to feature in a ransomware attack against UK critical national infrastructure by 2028. Its State of the Cyber Nation report warns that AI will increase the scale and efficiency of reconnaissance, social engineering, malicious code development and vulnerability exploitation, with Russia and China expected to routinely use AI in cyber operations. NCSC chief executive Richard Horne warned of a possible unprecedented rise in incidents in the coming months as attackers uncover longstanding weaknesses, rather than relying solely on entirely new attack techniques.
The NCSC identified technical debt, unsupported systems, delayed patching and underinvestment as key sources of exposure, urging organisations to strengthen resilience, reduce unnecessary internet exposure and treat Cyber Essentials as a baseline—not a complete security strategy. The government announced £60 million for the first phase of its national Cyber Shield and £70 million for a National Exposure and Real-Time Vulnerability Centre, alongside a new AI Cyber Security Centre of Excellence in Manchester. Britain is also testing frontier AI for defensive vulnerability discovery through Project DROMOS; the NCSC says defenders can retain a structural advantage through sustained investment, disciplined AI adoption and effective control of their environments.