cPGuard Update Channel Hijacked to Deploy Backdoor and Steal Server Credentials
Supply Chain Risk · 17 sources · Updated 2h ago · First seen Nov 3, 2026
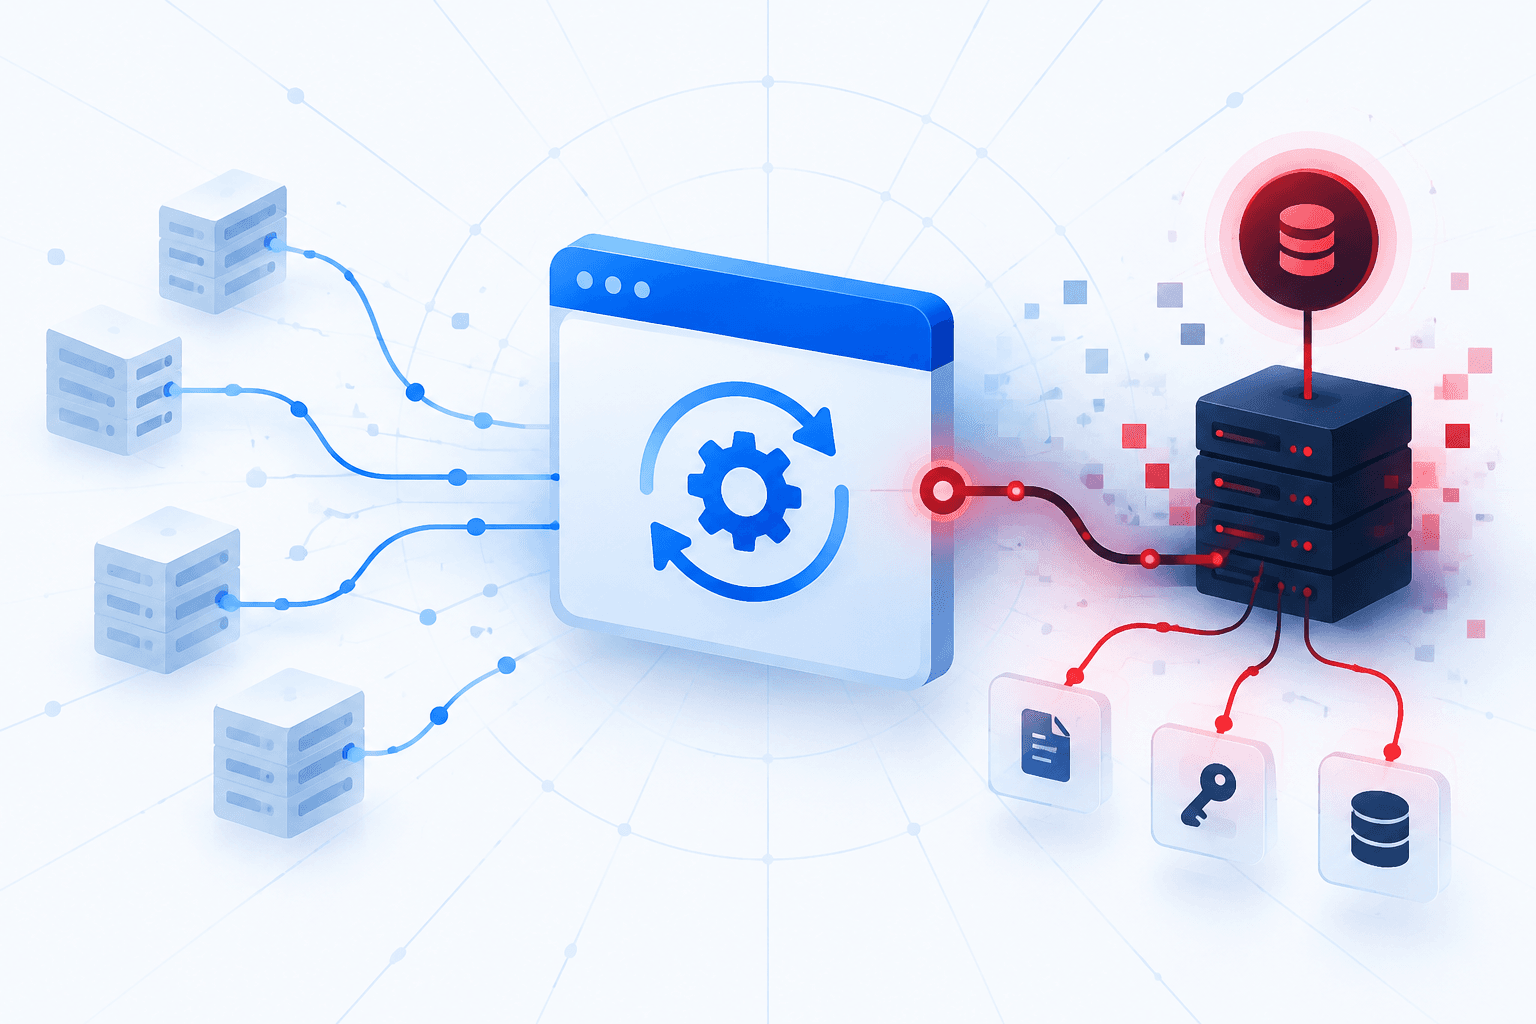
An unidentified attacker compromised OPSSHIELD’s cPGuard licensing and update infrastructure and distributed a malicious script through the Linux hosting security tool’s update channel. Cryptika reported that stolen credentials enabled the compromise and that versions 5.88.12 through 5.88.19 delivered the script, which installed a backdoor and collected Linux account files, database configuration, shell history, and SSH-related files. Collected data was sent to OPSSHIELD’s licensing server under a compromised account. By November 3, OPSSHIELD reportedly estimated that the attacker had retrieved 32 collected files corresponding to 32 customer servers; the total potentially affected population remained unknown.
OPSSHIELD said it stopped malicious distribution, secured the compromised account, and released cPGuard 5.88.25 to remove known malicious artifacts. Its advisory urges administrators to update every cPGuard server to version 5.88.25 or later immediately. Where malicious execution is known or suspected, customers should reset passwords, rotate potentially exposed SSH keys and other credentials, and assess whether rebuilding affected servers is warranted: cleanup cannot invalidate stolen secrets. The initial access method and full extent of attacker access remained under investigation.