Gorbag Targets Ukrainian Courts and Frontline Authorities With BeautyStealer
Active Exploitation · 23 sources · Updated 2m ago · First seen Nov 3, 2026
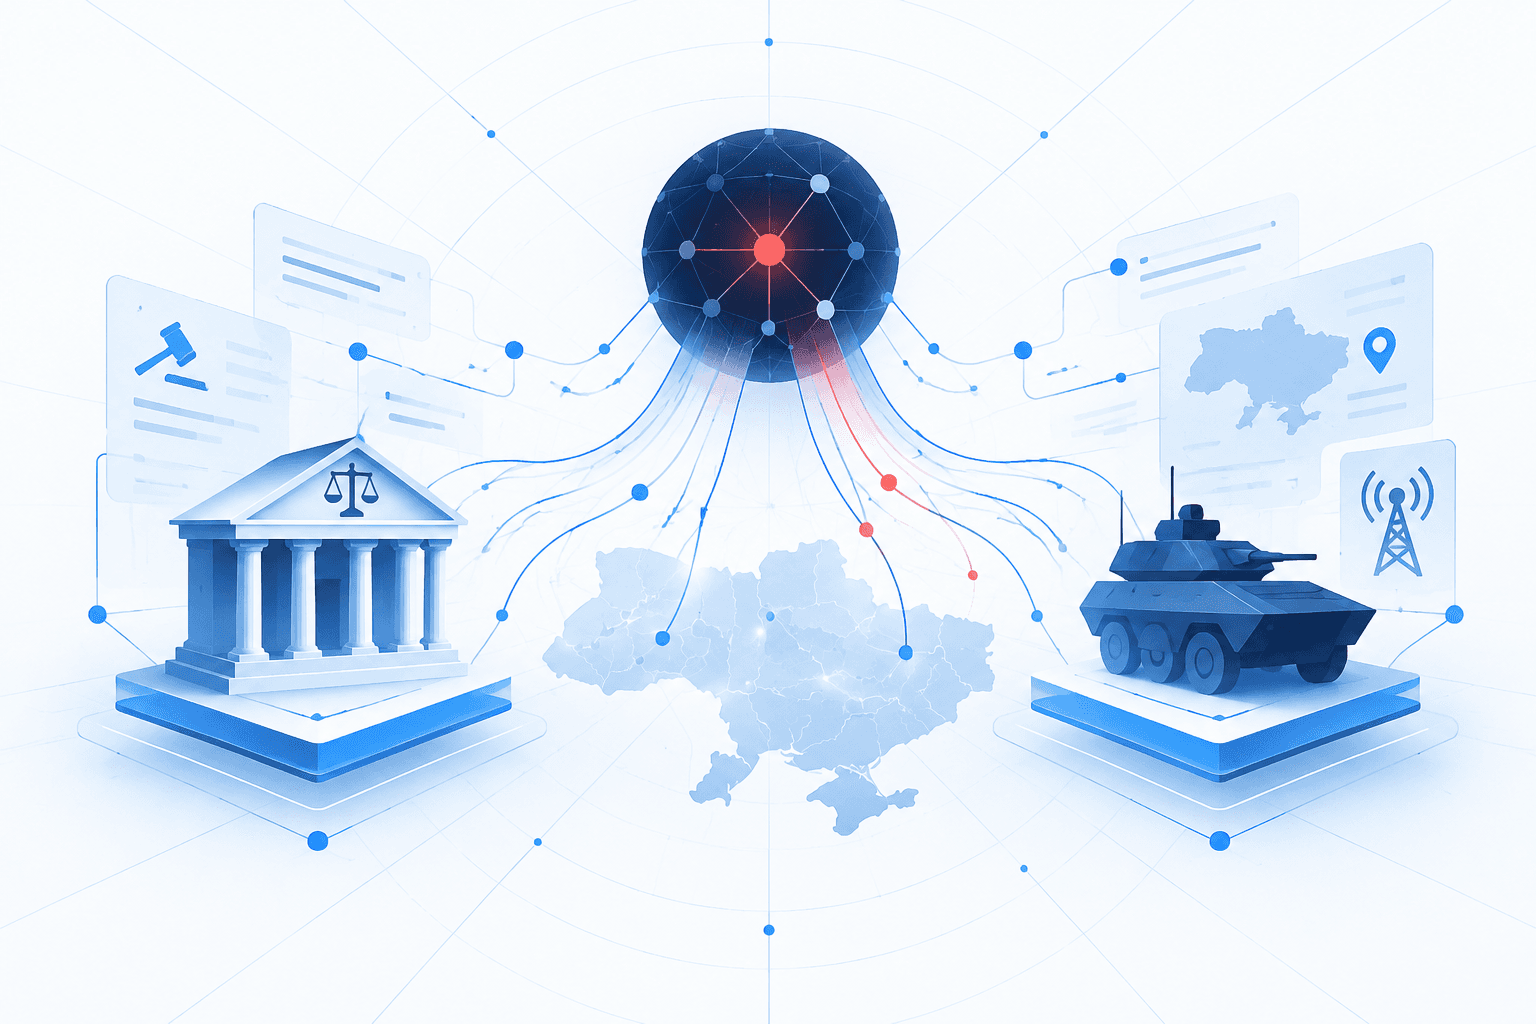
Russia-aligned threat group Gorbag has used spear-phishing since at least February 2025 to steal credentials and documents from Ukrainian law enforcement, courts, defense organizations and local governments near the front lines, ESET reported. Targets also included a major transportation hub for foreign military aid. The campaign initially delivered macro-enabled Excel attachments before shifting in early 2026 to malicious RAR archives exploiting the WinRAR path-traversal vulnerability CVE-2025-8088 to establish persistence through the Windows Startup folder.
Gorbag’s C++ malware, BeautyStealer, rapidly collects browser credentials and cookies, OpenVPN configurations and selected documents before attempting to delete itself. ESET observed expanded file-theft, encryption and exfiltration capabilities, with an emphasis on rapid collection rather than sophisticated long-term implants. The researchers assessed that the targeting could help Russia monitor war-crimes investigations, assess airstrike damage and understand Ukrainian civil-defense efforts. Gorbag might also supply stolen access to other actors, but that role remains unconfirmed and follow-on activity has not been observed. Defenders should prioritize patching WinRAR, scrutinizing unsolicited archive and macro-enabled attachments, and investigating unexpected Startup-folder entries.