Hijacked antd-img-crop GitHub Repository Delivers OverLord Stealer via Forged Commit
Supply Chain Risk · 3 sources · Updated 22h ago · First seen Nov 3, 2026
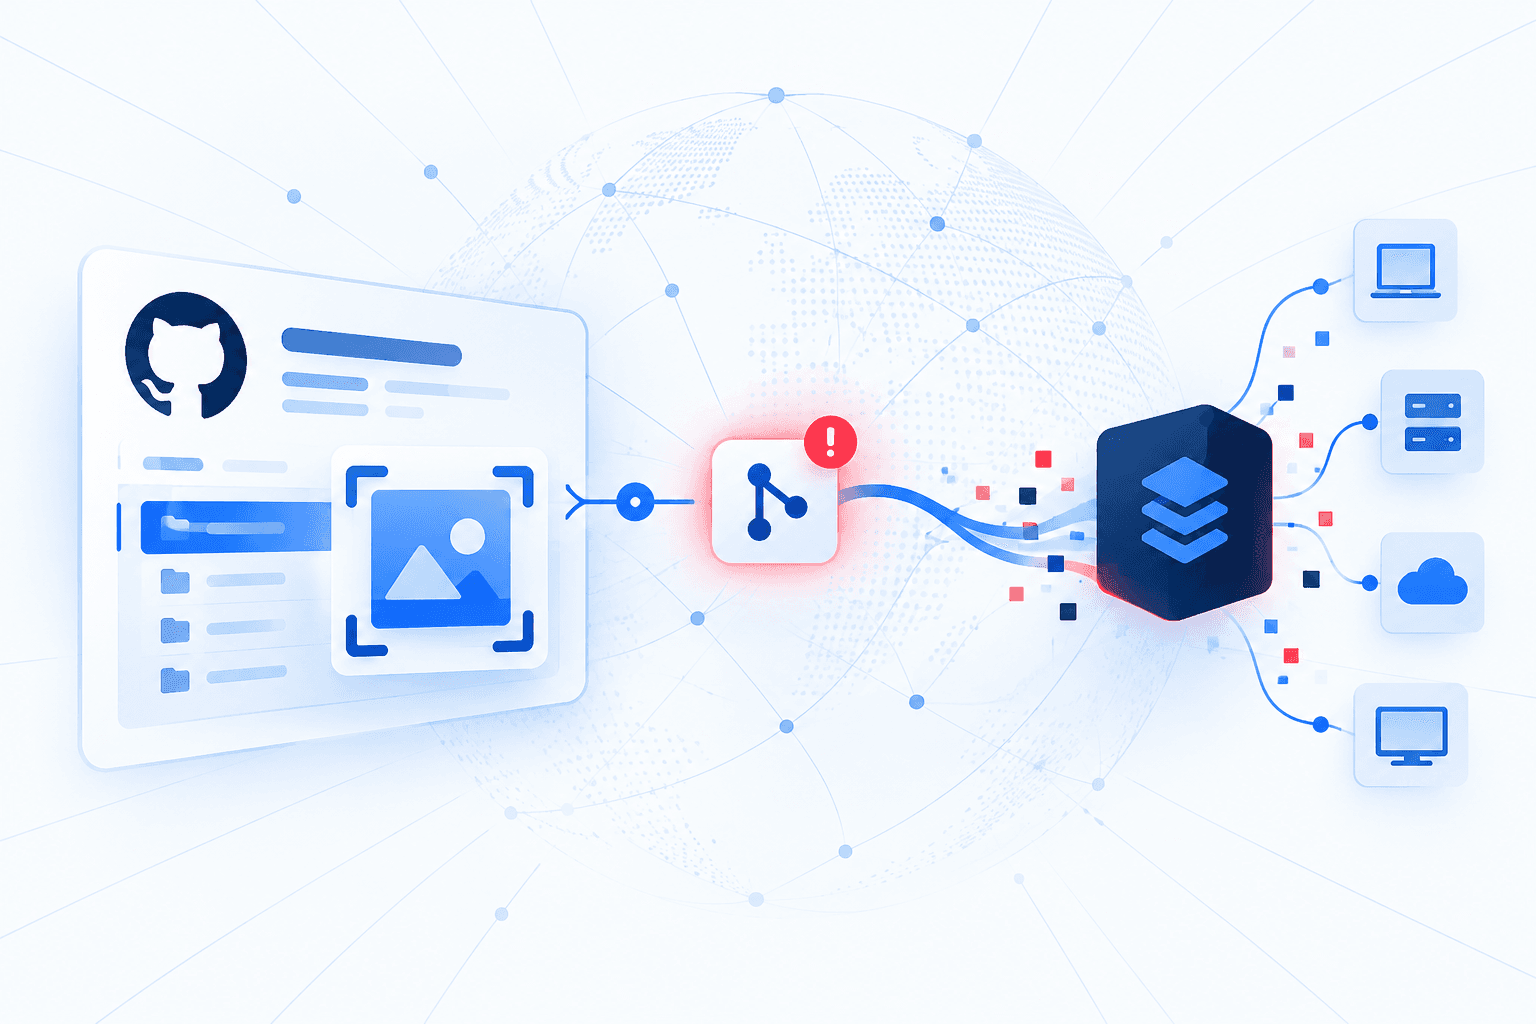
An attacker hijacked the antd-img-crop GitHub repository using a compromised maintainer account and force-pushed a forged release commit on October 31, 2026, SafeDep reported. A malicious prebuild hook triggers a three-stage infection chain when developers run the project's build, stealing credentials, cryptocurrency wallets, and developer secrets across macOS, Linux, and Windows before installing the OverLord remote-access agent disguised as Google software. The published npm package is not affected; the reported exposure concerns the compromised GitHub source.
SafeDep also identified a fake Amber Group careers portal and a suspected sideloaded VS Code or Cursor extension as additional delivery routes. Recruitment lures and cryptocurrency-focused targeting resemble the Contagious Interview campaign, but the researchers did not establish the operators' identity. An earlier malicious modification to hugo-paper used the same maintainer account and infrastructure, prompting SafeDep to assess that the account remained compromised. Organizations should review developer use of the affected repository and investigate potential credential exposure; indicators reproduced in the secondary report require validation because some purported SHA-256 hashes are malformed.