CodeStorm AiTM Phishing Kit Linked to More Than 100 Microsoft 365 Tenant Compromises
Social Engineering & Fraud · 3 sources · Updated 17h ago · First seen May 20, 2026
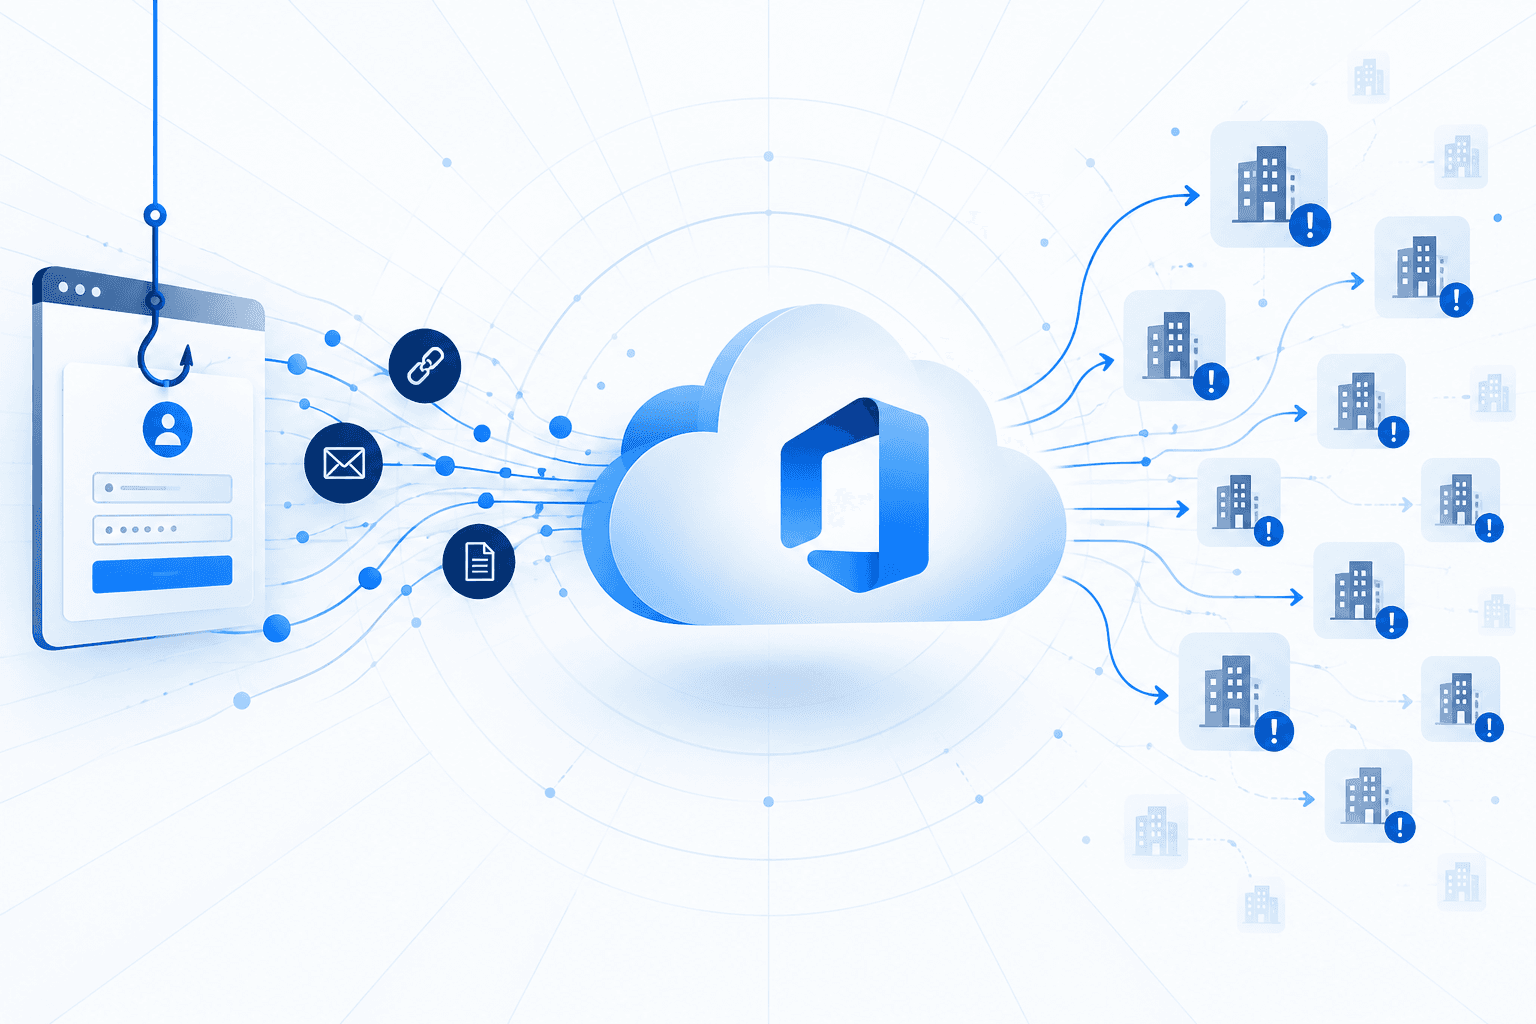
Hexastrike identified CodeStorm, a previously undocumented adversary-in-the-middle (AiTM) phishing kit targeting Microsoft 365 credentials, multifactor authentication responses, and authenticated session material. Active since at least January 2025 and still operating at the report’s May 2026 publication, the campaign was linked to more than 100 confirmed tenant compromises and approximately 600 targeted organizations—not 600 confirmed victims. Its infrastructure encompassed at least 400 attacker-controlled apex domains and roughly 12,000 subdomains. Attackers delivered lures through compromised accounts, trusted SaaS platforms, PDF and HTML files, and occasional QR codes.
CodeStorm combines Cloudflare Turnstile gating, encrypted JavaScript, Tencent Cloud Object Storage payload delivery, and browser anti-analysis checks with real-time proxying of Microsoft authentication. Hexastrike assessed a moderate-confidence association with Storm-1167, but found insufficient code-level overlap to classify it as an existing publicly documented kit family. Observed follow-on activity included session reuse, concealment through Outlook inbox rules, SharePoint reconnaissance, and onward phishing. Microsoft has separately documented multistage AiTM phishing leading to business email compromise, underscoring the risk beyond credential theft. Defenders should prioritize phishing-resistant authentication and correlate identity activity with suspicious mailbox rules, cloud-content access, and outbound phishing rather than relying on conventional MFA alone.