EY Survey Reveals AI Governance Gaps as Organizations Bypass Controls for Deployment
Emerging Technology Risk · 2 sources · Updated 13d ago · First seen May 28, 2026
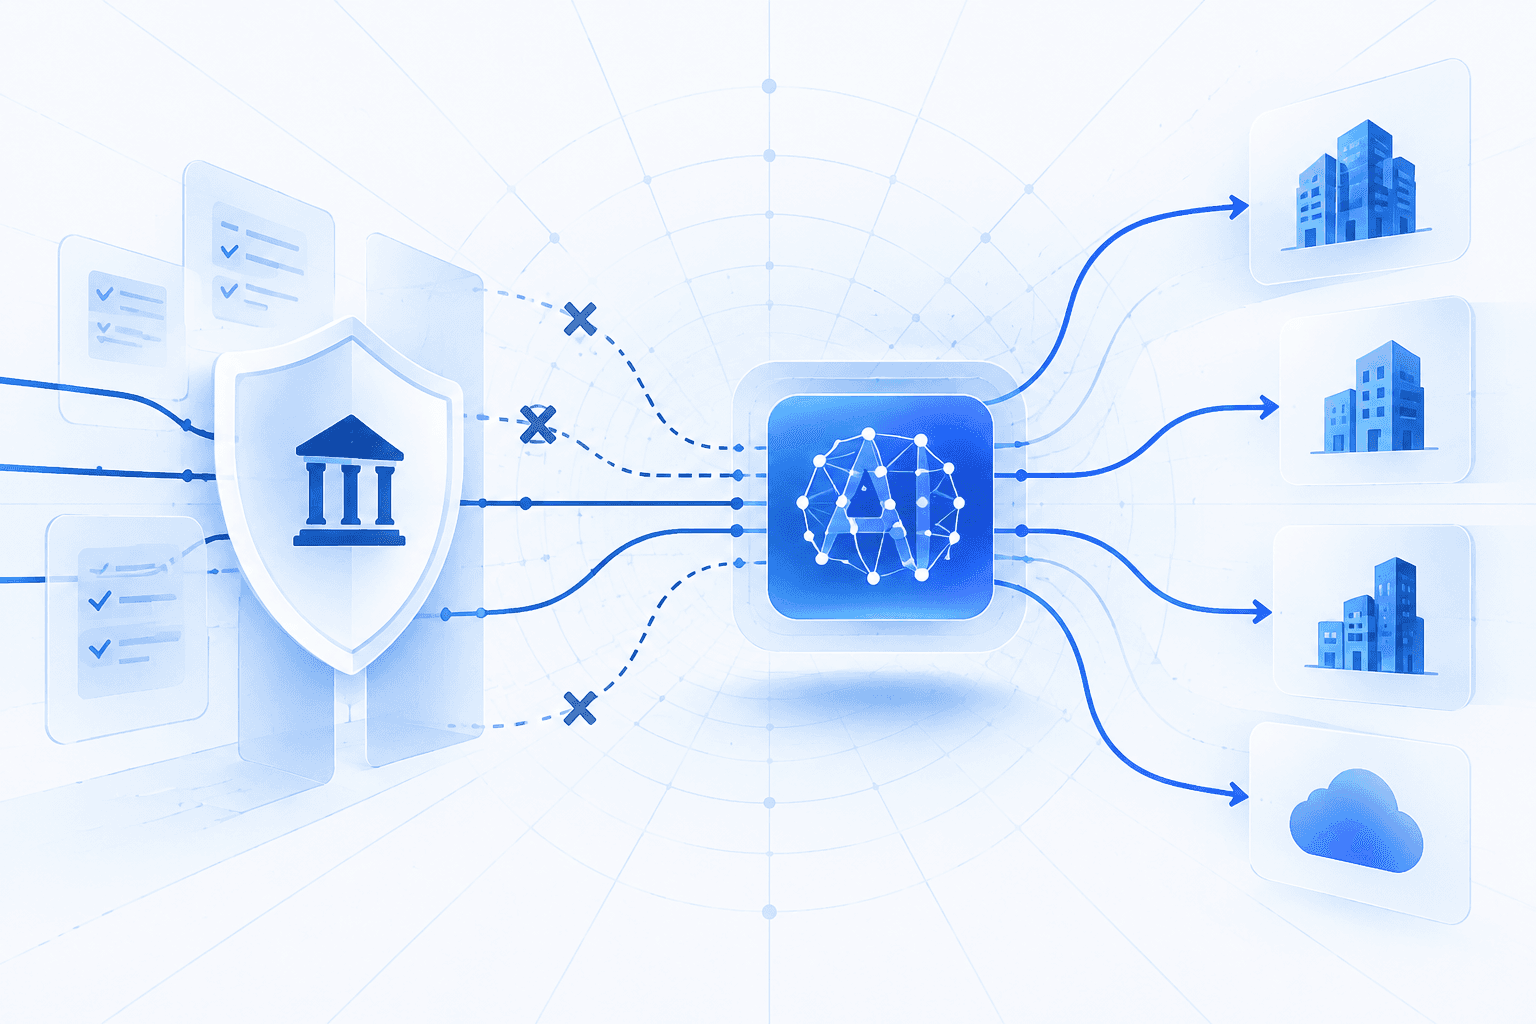
An EY survey of 202 senior AI decision-makers at US organizations found a significant gap between formal AI governance and operational oversight: 98% reported having a governance policy, yet 47% had bypassed governance for urgent deployments and 41% lacked visibility into organizational AI use. EY’s findings also highlighted weaknesses in oversight of agentic AI, including governance frameworks not yet updated for autonomous systems and an inability among some respondents to detect unauthorized internal AI agents.
Kiteworks’ assessment of the findings argues that written policies alone cannot demonstrate compliance without enforceable controls and audit evidence. Autonomous agents compound the exposure by taking actions under unclear accountability or outside existing oversight. The article recommends assigning accountable human owners, enforcing access controls for each request, encrypting sensitive data, and maintaining tamper-evident logs. For CISOs, the priority is to verify that governance operates across actual AI deployments through continuous evidence collection and periodic assurance reviews—not merely that policies exist.