PolinRider Loaders Found in 10 Hijacked npm Packages Use Ethereum to Locate Payloads
Malware Intelligence · 3 sources · Updated 2d ago · First seen Nov 4, 2026
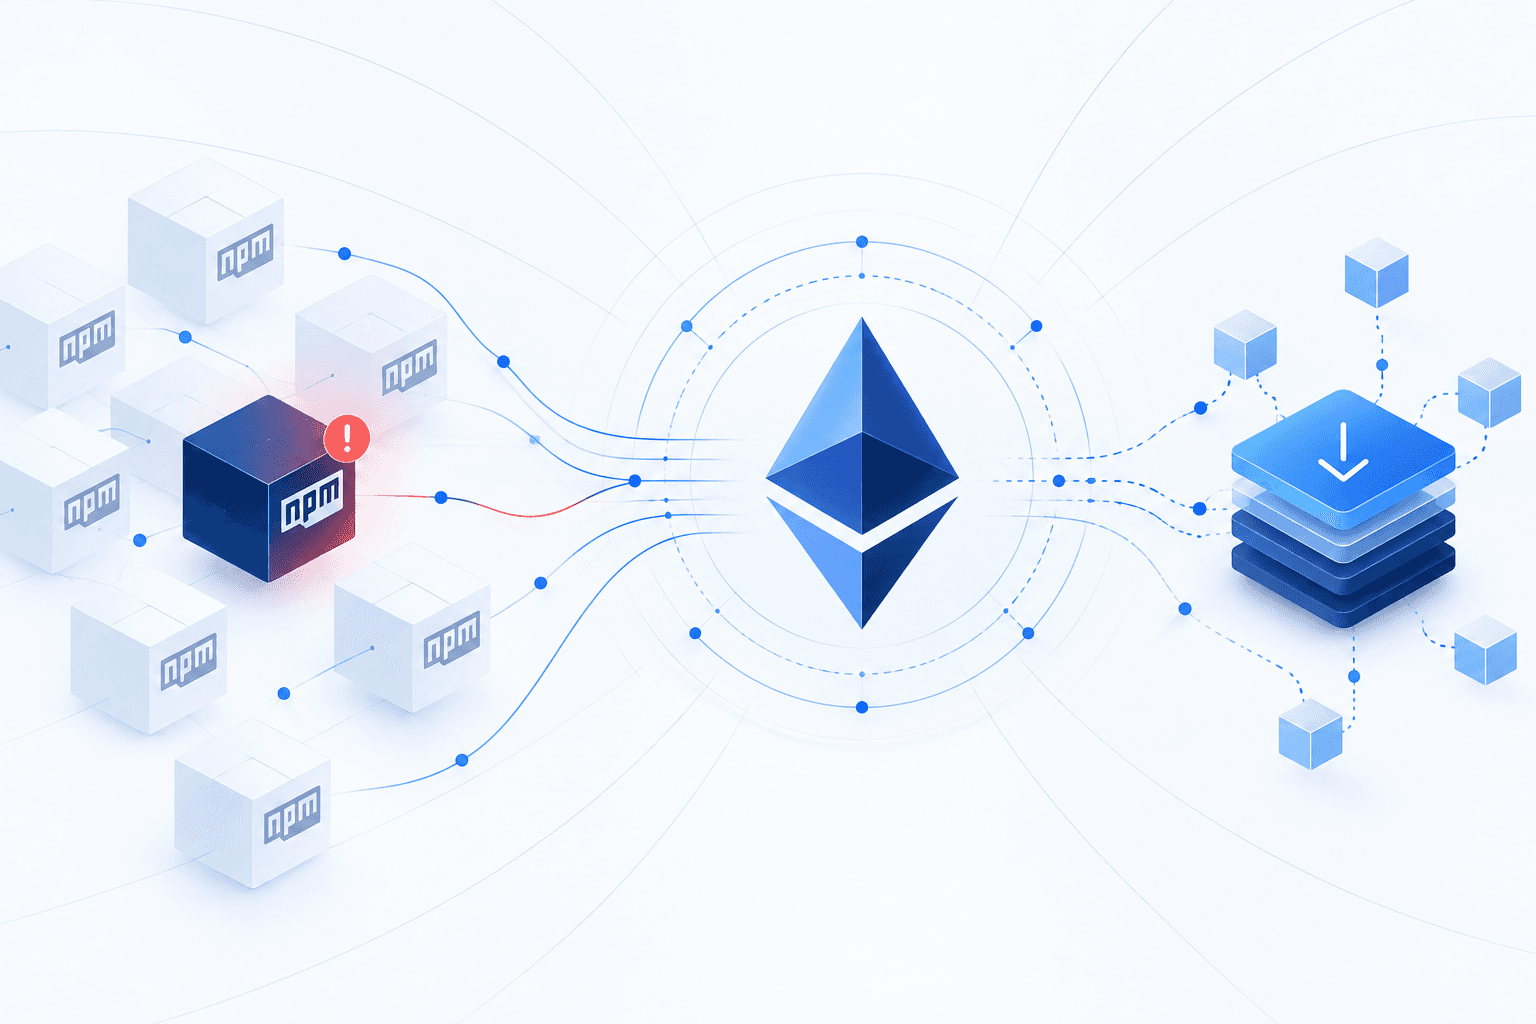
Sonatype Research Labs identified concealed runtime loaders in 12 npm releases across 10 hijacked packages, tracking the campaign as sonatype-2026-010515. The loaders query transactions from a hard-coded Ethereum wallet to derive a payload-server address, retrieve XOR-encoded JavaScript, and execute it within the application or detached Node.js processes. Shared wallet details, infrastructure, and retrieval paths connect the releases to previously documented PolinRider activity, but do not establish common ownership with GhostAction. Greenflagged documented related releases published through the npm accounts clockbook-app and pubngo-stack, including an initial variant concealed behind 157 tab characters and another using different obfuscation.
Disabling npm installation scripts does not prevent execution: the injected code runs when affected modules are loaded or applications start. Although the first malicious releases used the next distribution tag, subsequent changes exposed ordinary installations through latest, including @adminide-stack/utils@0.0.16-130 and @adminide-stack/client-redux@0.0.16-18. Organizations should identify and remove affected releases, inspect application hosts and build environments for evidence of execution, and treat systems that ran the injected code as compromised. Response should include assessing potentially exposed credentials and rotating those at risk.