Backdoored ARTEX Docker Image Enables Unauthenticated Root Command Execution
Supply Chain Risk · 3 sources · Updated 11d ago · First seen Nov 5, 2026
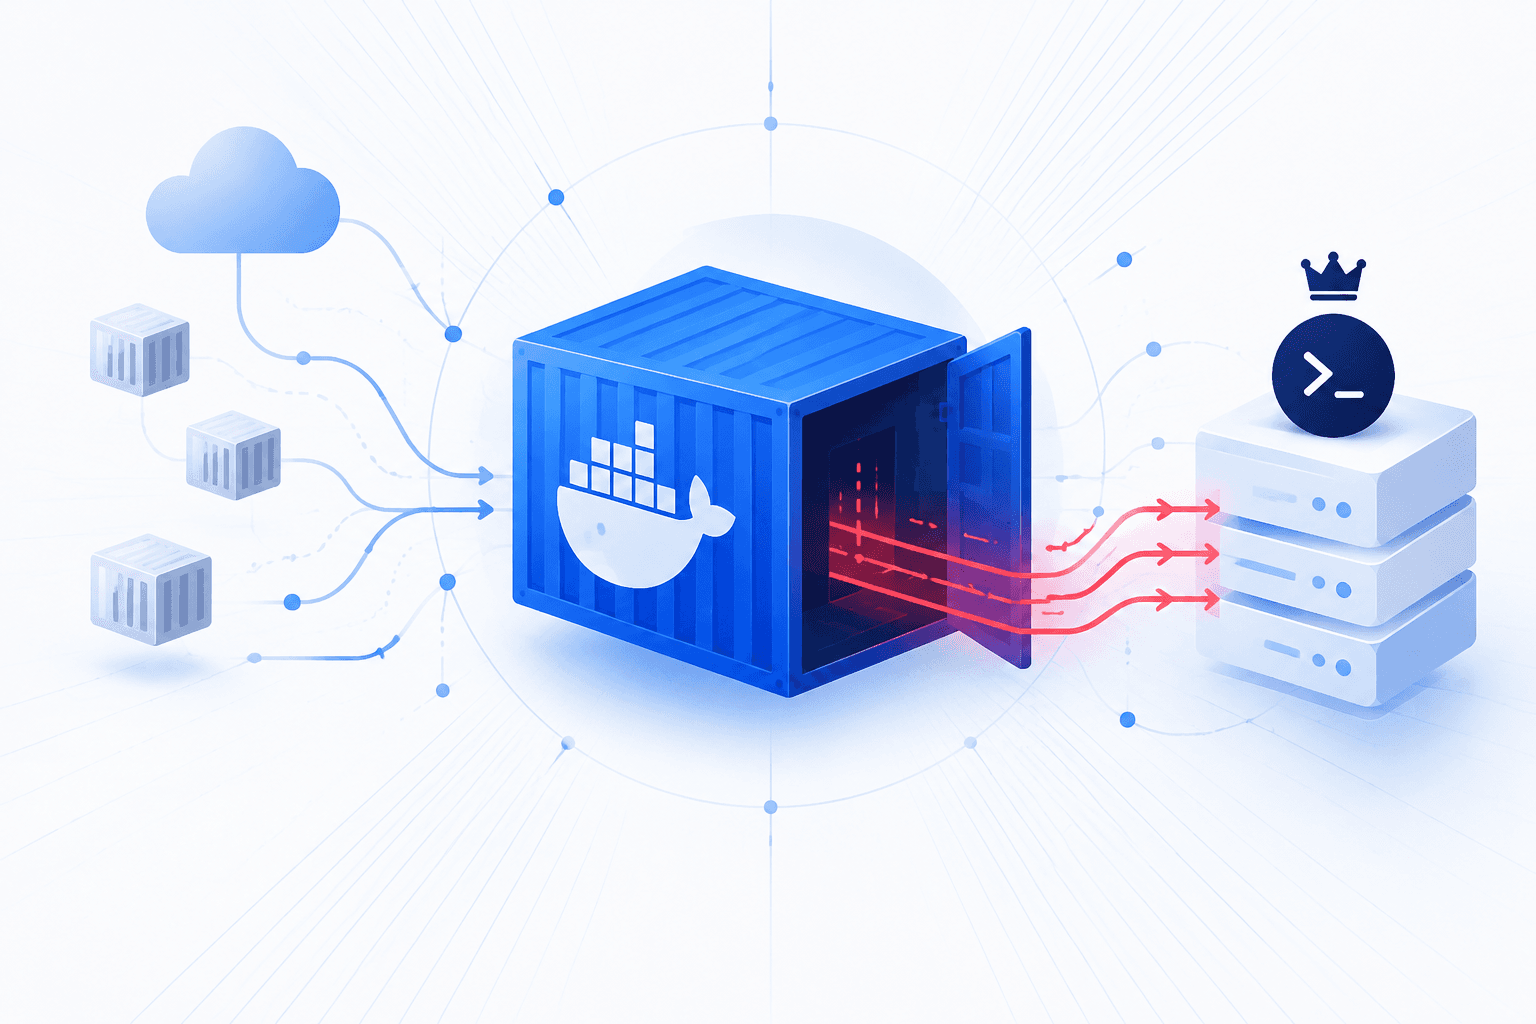
Backdoored copies of the ARTEX AI penetration-testing tool allow unauthenticated attackers to execute commands with root privileges through a hidden function in a modified login handler. Researcher Badbyte identified the malicious modification, and researchers found 62 internet-facing consoles running the compromised build between November 2 and 4, 2026. The implicated Docker image had approximately 9,000 downloads, although that figure does not establish the number of affected deployments. Organizations using ARTEX should verify image provenance, isolate compromised deployments, and assess potential credential exposure.
Separately, India’s CERT-In reported an active AI-assisted campaign by Crafty Falcon targeting the country’s banking, financial services, and insurance sector, cryptocurrency exchanges, and digital-asset providers. Attackers exploit exposed applications, APIs, and credentials, including abusing payment APIs from compromised, allowlisted infrastructure to bypass controls and transfer funds to attacker-controlled accounts. Reported techniques include autonomous offensive tools, rapid script generation, infrastructure rotation, cloud compromise, and detection suppression. CERT-In also issued AI security auditing guidance covering authorization boundaries, agent permissions, human oversight, emergency shutdown, credential revocation, and continuous assurance. The references do not establish a connection between Crafty Falcon and the ARTEX backdoor.