Attackers Use Agentic AI to Turn Exposed GitHub Secrets Into Cloud Access
Emerging Technology Risk · 11 sources · Updated 8d ago · First seen Nov 6, 2026
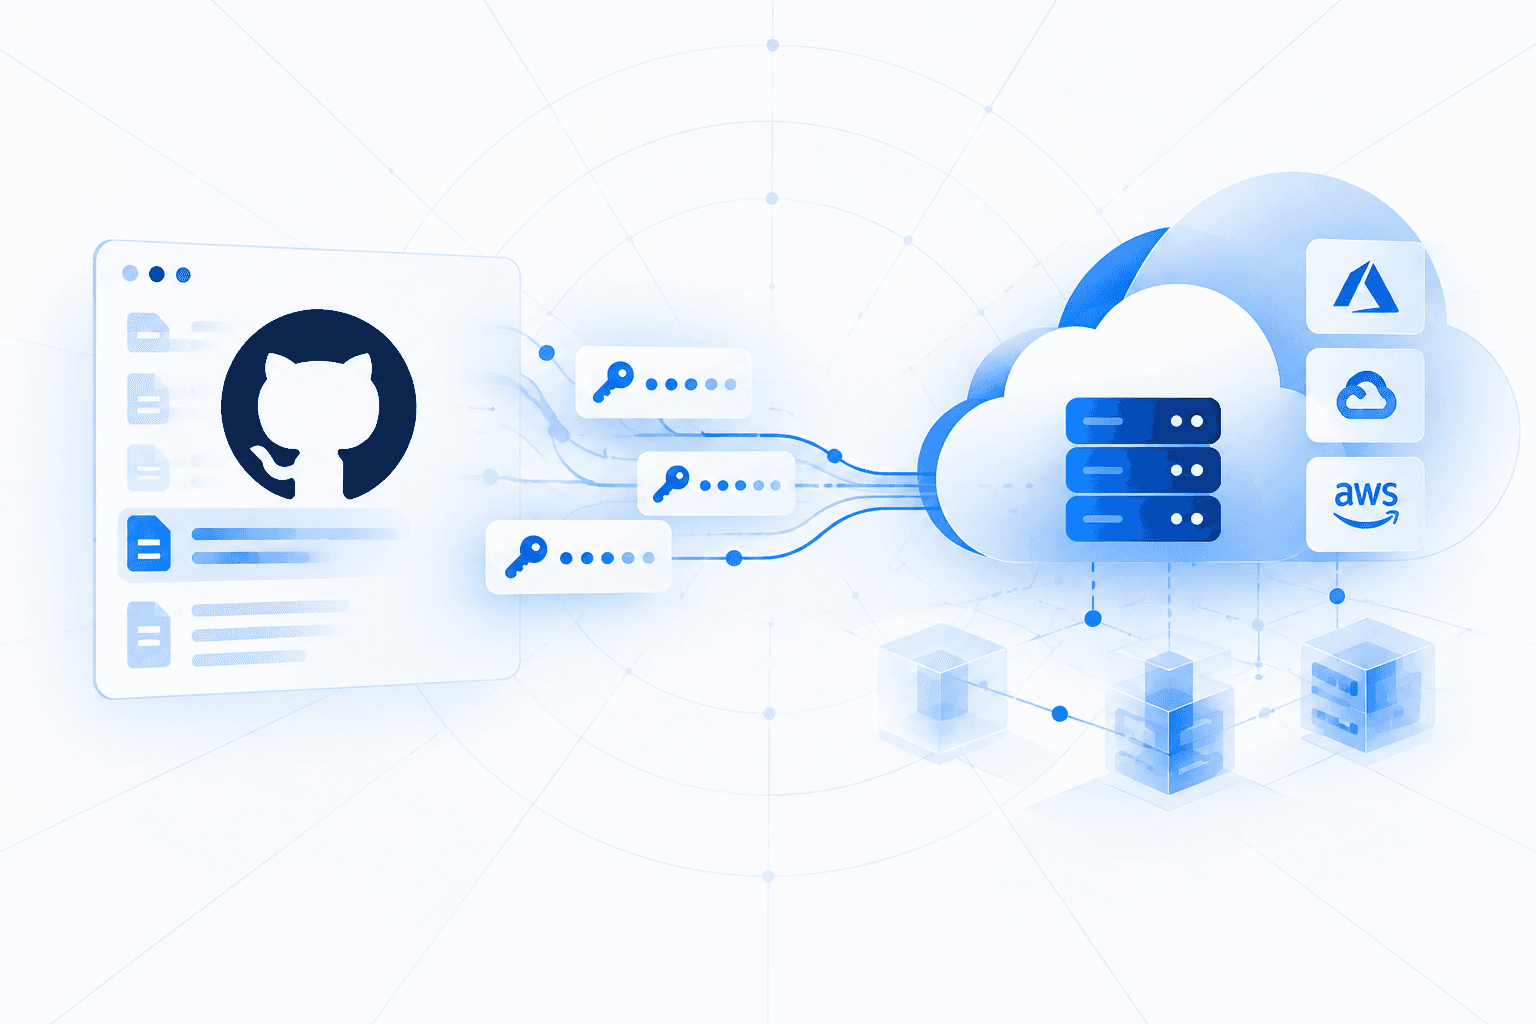
Threat actors are using agentic AI offensive frameworks, including ARTEX, to discover exposed credentials in public GitHub repositories and automate attacks against cloud environments, Microsoft Threat Intelligence reported. Microsoft observed activity beginning in August 2026 and documented application-credential abuse against Microsoft Entra ID, Azure, and Microsoft 365 from October 28. Attackers used compromised application identities to enumerate resources, obtain additional credentials, access organizational content, and exfiltrate secrets. In one observed case, an agent moved from GitHub secret discovery to Azure Key Vault data exfiltration in five minutes. API request sequences showed behavior consistent with adaptive troubleshooting, including correcting API versions after failed requests.
A separate Todyl report described an actor using stolen application credentials to sign into Entra ID and Azure DevOps as workload identities, underscoring the risk of compromised nonhuman accounts. Microsoft recommends immediately revoking or rotating exposed credentials, reviewing historical activity for misuse, and restricting workload-identity permissions. Defenders should prioritize detection of rapid, cross-service activity rather than relying solely on IP addresses or user-agent strings, which may not reliably distinguish automated attacks from legitimate application behavior.