Binance Signing-Service Compromise Enabled Persistent Wallet Draining via EIP-7702
Emerging Technology Risk · 4 sources · Updated 20h ago · First seen Nov 6, 2026
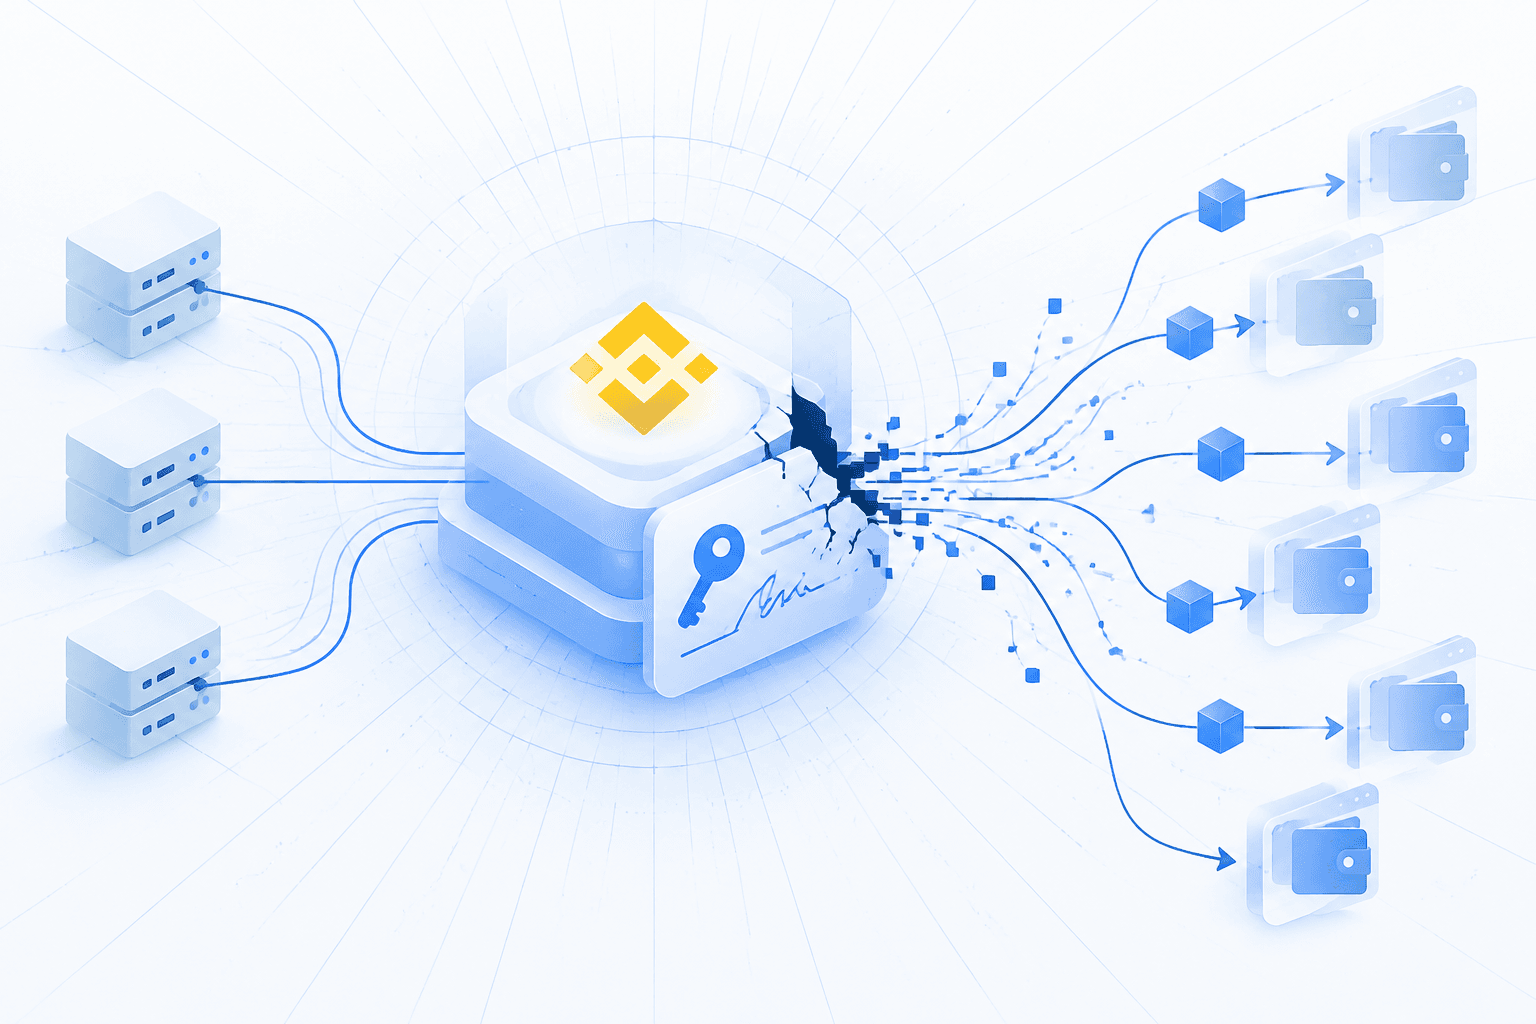
An attacker gained unauthorized access to Binance’s wallet-signing service during its October 2026 security incident, obtaining valid signatures that enabled fund theft without a confirmed private-key leak. According to Binance’s November 3 report, the attack involved social engineering, misuse of an internal AI tool, and stolen credentials. Trail of Bits reported that the attacker used EIP-7702 delegation to establish persistent wallet authority, allowing repeated transfers—including theft of later deposits—without additional Binance signatures. Other wallets were drained through ordinary signed transfers.
The incident highlights a custody risk beyond private-key exposure: compromised signing systems can authorize lasting control over wallets even when keys remain protected. Trail of Bits recommends restricting access to signing infrastructure, treating delegation as an administrative privilege requiring separate approval, and enforcing custody safeguards independent of operational keys. Organizations should monitor changes in wallet authority alongside asset movements and test controls against EIP-7702 and ERC-4337 execution paths rather than relying solely on transfer monitoring.