Mallory
← Back to News
widely-deployed-product-advisory

Outlook Requires SPF, DKIM and DMARC for High-Volume Email Senders

Patch & Detection Intelligence · 2 sources · Updated 8d ago · First seen May 20, 2026
Outlook Requires SPF, DKIM and DMARC for High-Volume Email Senders

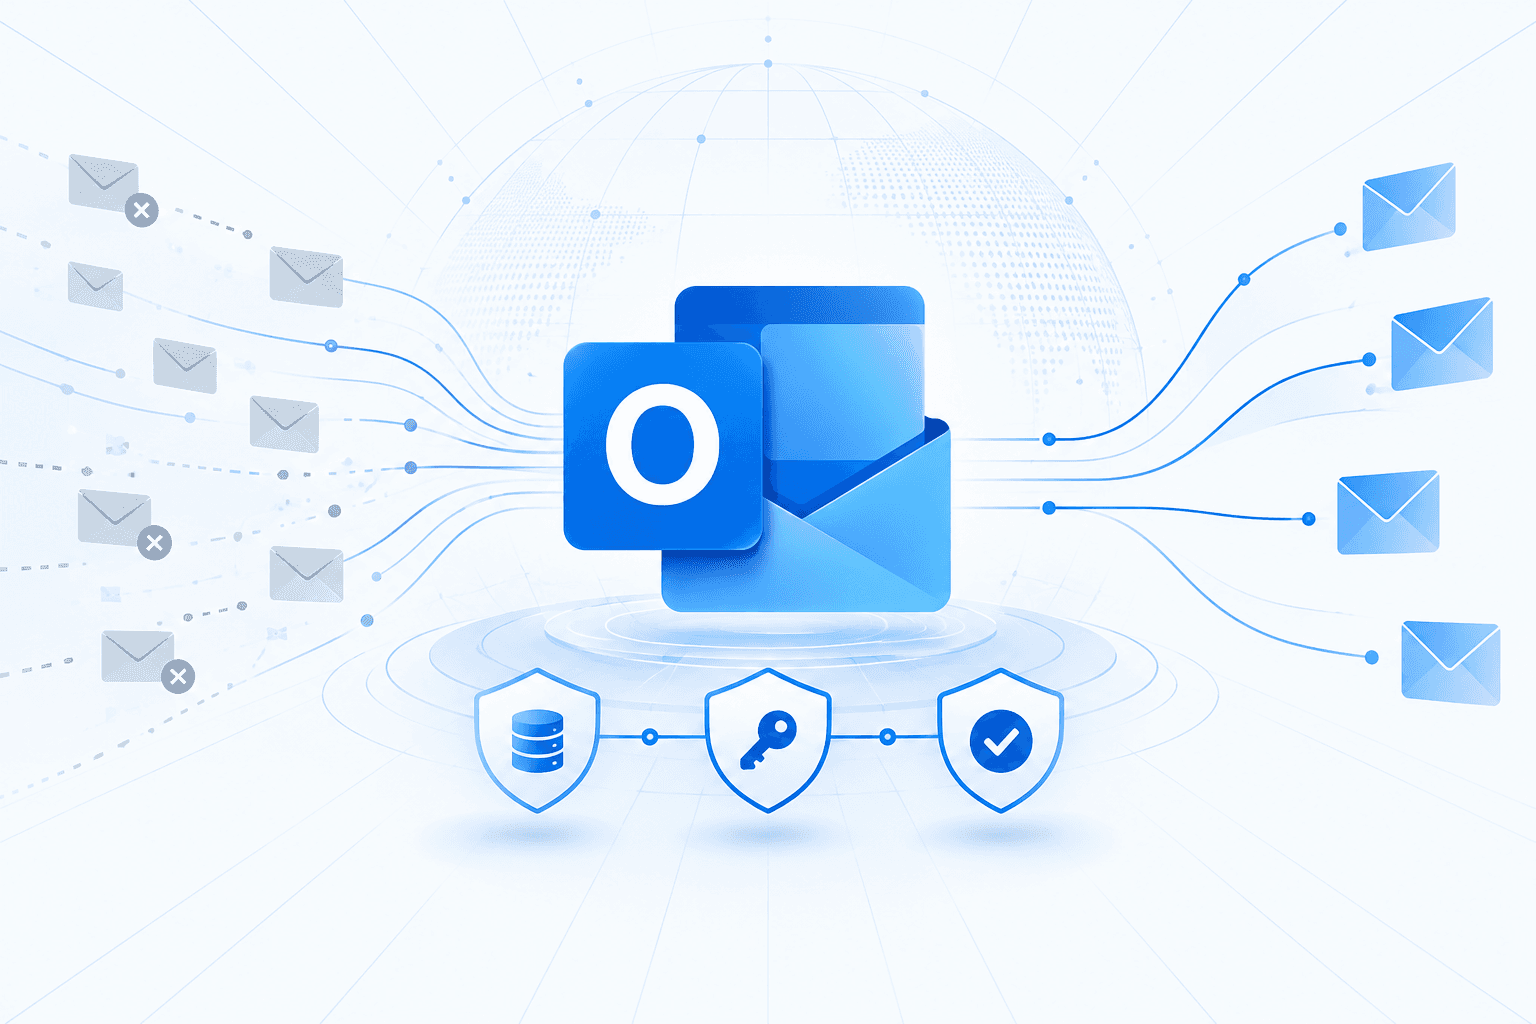
Microsoft announced mandatory email authentication for domains sending more than 5,000 messages daily to Outlook, aiming to reduce spoofing, phishing and spam. Senders must pass both SPF and DKIM checks and publish a DMARC policy of at least p=none, with domain alignment through SPF or DKIM. The announcement named May 5, 2025, as the enforcement start date but gave conflicting descriptions of handling noncompliant messages: immediate rejection versus initial delivery to Junk followed by rejection at an unspecified later date. Safe Sender lists will not bypass the authentication requirements.

Microsoft’s supporting guidance explains that SPF and DKIM alone have limitations, while DMARC checks alignment with the visible From domain and ARC helps preserve authentication results through legitimate intermediaries. Microsoft 365 also combines authentication results with reputation, history and behavioral signals through composite authentication. Organizations should audit all sending services, including third parties, validate SPF records, enable DKIM, and configure DMARC reporting before tightening policies. Valid sender addresses, reliable unsubscribe mechanisms and clean mailing lists are additional recommended practices, but do not replace authentication compliance.
Patch this, or something else?See real exploitation activity before you spend the cycle.
Triage this advisory
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

1 event
  1. Reported Apr 2, 20252y ago

    Outlook announces mandatory email authentication for high-volume senders

    Outlook announced that domains sending more than 5,000 emails daily must pass SPF and DKIM checks and publish a DMARC policy of at least p=none with SPF or DKIM alignment. The announcement identified May 5, 2025, as the planned enforcement start, but gave conflicting descriptions of whether noncompliant messages would be rejected immediately or initially delivered to Junk.

    Strengthening Email Ecosystem: Outlook’s New Requirements for High‐Volume Senders | Microsoft Community Hub
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Affected products

1 linked
Outlook

Organizations

1 linked
Microsoft Corporation
Do you run this?See real exploitation activity behind this advisory so you can triage it against everything else in the queue.
Prioritize This Patch
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.