Mallory
← Back to News
actively-exploited-vulnerabilityremote-access-implantdefense-evasion-methodinternet-facing-service-vulnerability

AhsayCBS Zero-Day Exploitation Deploys Web Shells and a Host-Locked Python Backdoor

Active Exploitation · 9 sources · Updated 5d ago · First seen Nov 10, 2026
AhsayCBS Zero-Day Exploitation Deploys Web Shells and a Host-Locked Python Backdoor

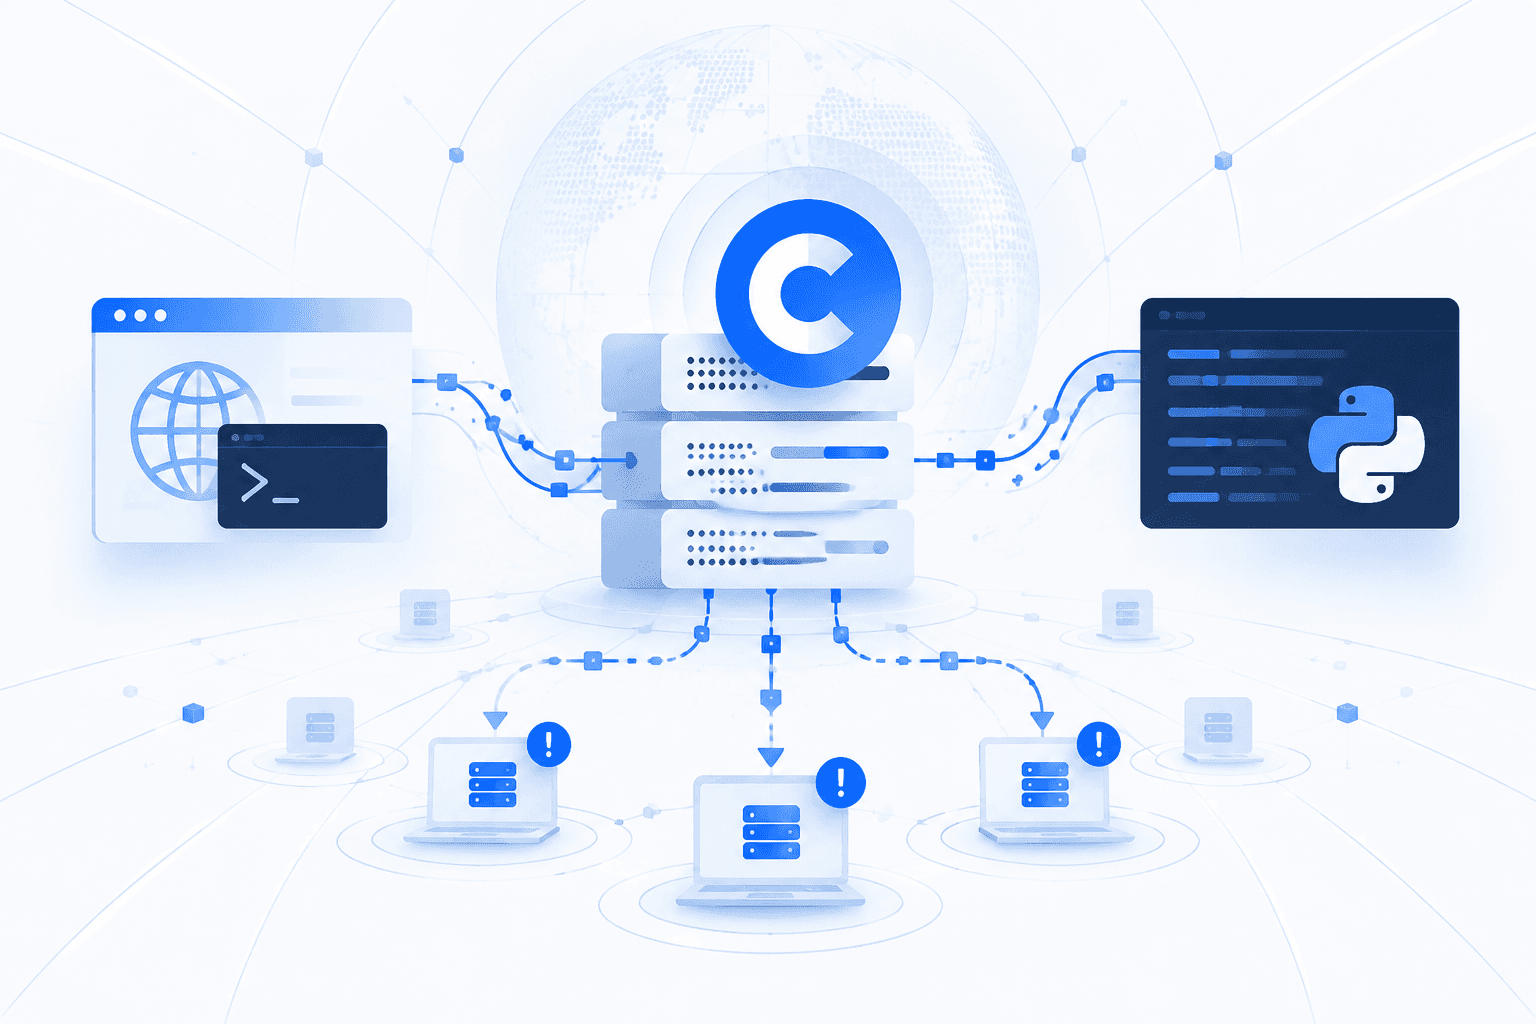
An unidentified threat actor exploited two AhsayCBS vulnerabilities, CVE-2026-105133 and CVE-2026-105134, to bypass authentication and execute arbitrary commands on backup infrastructure. Huntress observed the activity in October 2026, and Ahsay Backup released patches in mid-October. The flaws were assessed to have been exploited as zero-days. The intrusion involved five web-shell families, two XMRig cryptocurrency miners, tunneling tools, remote-access software, and Microsoft Defender exclusions.

A custom Python backdoor restricted execution to its intended host, helping it evade sandbox analysis, before loading an embedded DLL into memory and contacting creepexplosiondarknight[.]com. A credential-retrieval command observed on a Veeam server in the same environment suggested deliberate targeting of backup infrastructure, although the extent of credential retrieval remained unknown. Organizations running AhsayCBS should prioritize the available patches and investigate backup systems for web shells, unauthorized remote-access tools, unexpected Defender exclusions, and signs of credential access.
This is being exploited nowSee which actors are running it and whether you're in range.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

7 events · Oct 2026 – Nov 9, 2026
  1. Reported Nov 11, 20267d ago

    Ahsay releases AhsayCBS 10.3.6.1 with additional security hardening

    Ahsay Backup released AhsayCBS 10.3.6.1 with additional security hardening following attacks on its backup servers. The company said partners reported unauthorized access starting October 9 and issued guidance identifying signs of compromise, including rogue administrator accounts.

    TheHackersNews: 🚨 UPDATE: Ahsay Backup has released AhsayCBS 10.3.6.1 with additional security hardening following attacks on its backup...
  2. Reported Nov 10, 20267d ago

    Credential-retrieval command targets a Veeam server in the same environment

    Huntress observed a command consistent with NetExec's Veeam credential-theft module that queried the VeeamBackup PostgreSQL database and attempted to decrypt stored credentials using DPAPI. The extent of credential retrieval was unknown, but Huntress assessed that the activity suggested deliberate targeting of backup infrastructure.

    Attackers Exploit AhsayCBS Flaws to Deploy Sandbox-Evading Python Backdoor
  3. Reported Nov 10, 20267d ago

    Expanded intrusion deploys a host-bound Python backdoor and persistent access tools

    A more extensive intrusion deployed five JSP web-shell families, two XMRig miners, GOST and Chisel tunnels, and AnyDesk, Atera, and Splashtop, while configuring Microsoft Defender exclusions. A custom Python implant checked a MachineGuid-derived marker before loading an embedded DLL in memory and contacting creepexplosiondarknight[.]com, restricting execution to its intended host.

    Attackers Exploit AhsayCBS Flaws to Deploy Sandbox-Evading Python Backdoor
  4. Nov 9, 20269d ago

    Huntress details PNG-concealed Java loader and authenticated AhsayCBS webshell

    Huntress published technical findings showing a webshell that extracted AES-encrypted Java payloads from PNG pixels, loaded them into memory, and concealed responses in images. A separate webshell authenticated requests with HMAC-SHA256 and supported command execution and large file transfers, although investigators found no logs proving its download function was used.

    Hackers Exploit AhsayCBS Vulnerabilities to Hide Malware in PNG Images and Deploy Stealthy Backdoors
  5. Reported Nov 5, 202613d ago

    Ahsay releases v9.17.0 with vulnerability patches and security hardening

    Ahsay released version 9.17.0 with patches for CVE-2026-105133 and CVE-2026-105134 and its Q4/2026 security patchset. The release strengthens authentication and session management, disables remote API access by default, disables the JSP engine to prevent malicious JSP execution, and removes access-token use.

    New Ahsay v9.17.0 Released | Ahsay Backup
  6. Oct 2026

    Ahsay Backup patches both exploited AhsayCBS vulnerabilities

    Ahsay Backup released patches for CVE-2026-105133 and CVE-2026-105134 in mid-October 2026, addressing the flaws used to bypass authentication and execute arbitrary commands.

    Attackers Exploit AhsayCBS Flaws to Deploy Sandbox-Evading Python Backdoor
  7. Oct 2026

    Attackers exploit AhsayCBS flaws to deploy web shells and cryptocurrency miners

    Huntress observed an unidentified attacker chaining CVE-2026-105133 and CVE-2026-105134 to bypass authentication and execute arbitrary commands in October 2026. Initial smash-and-grab activity deployed web shells and XMRig miners; the vulnerabilities were assessed to have been exploited as zero-days.

    Attackers Exploit AhsayCBS Flaws to Deploy Sandbox-Evading Python Backdoor
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

1 linked

Affected products

1 linked
Ahsaycbs

Observables

44 linked

Indicator values are masked on this page. View all 44 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Correlate live exploitation activity against the software you actually run, and see where you're exposed.
See Who's Exploiting This
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.