Critical Fortinet2Shell Flaw Enables FortiClient RCE with FortiPAM Enabled
Vulnerability Disclosure · 11 sources · Updated 4d ago · First seen Nov 11, 2026
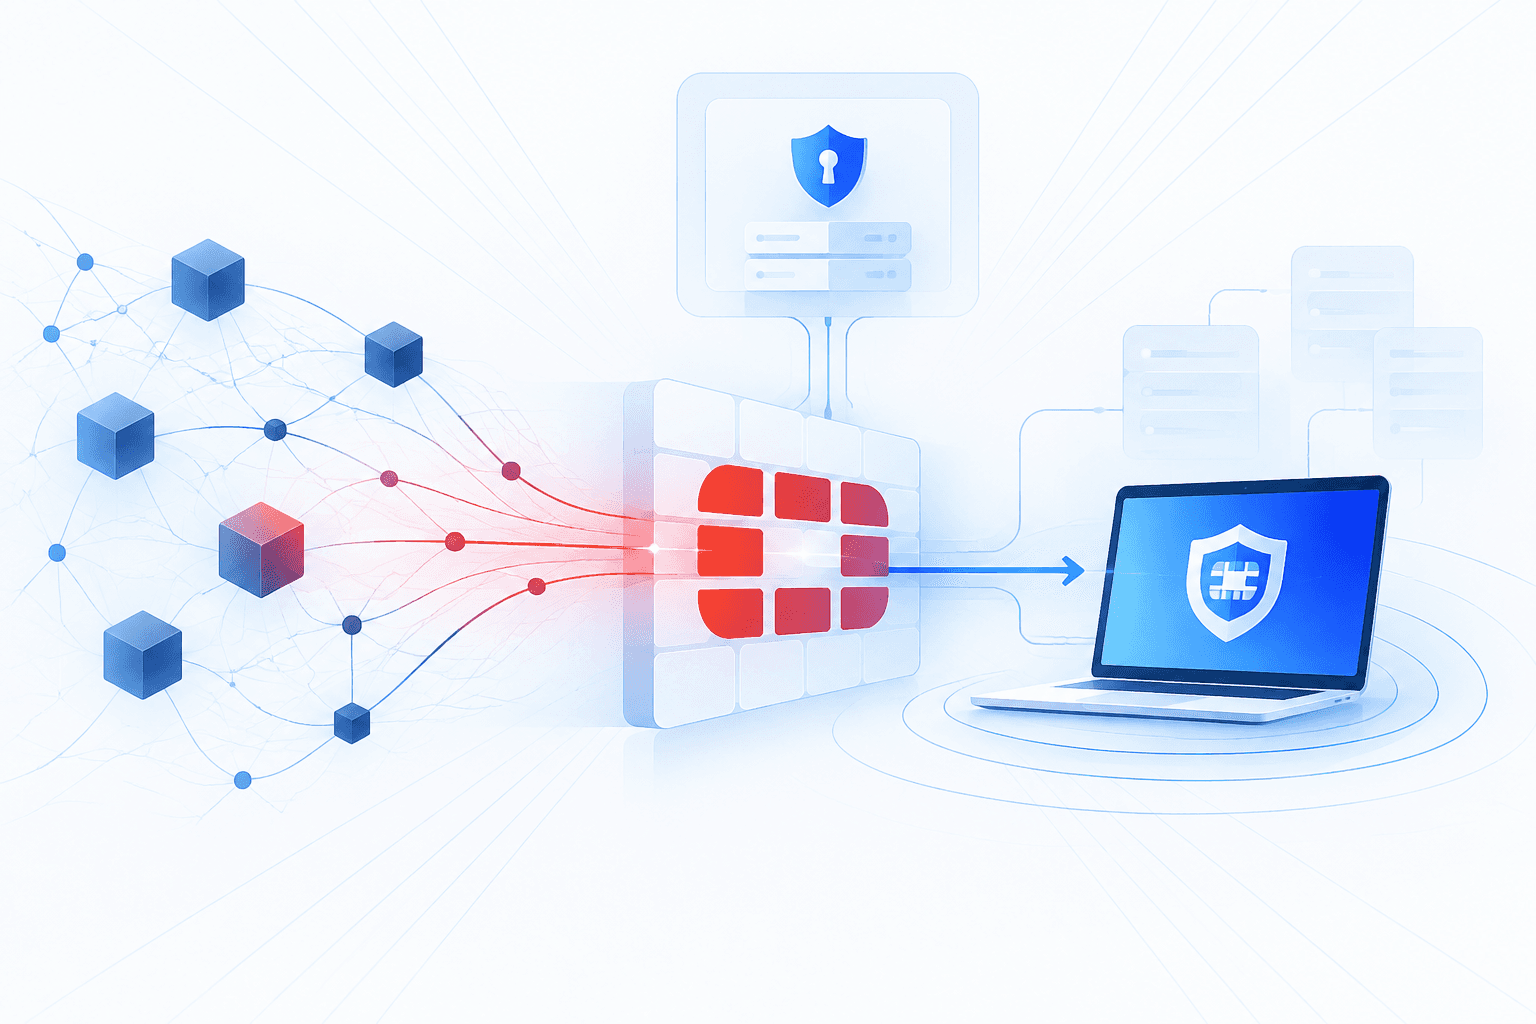
Fortinet disclosed CVE-2026-121529, a critical FortiClient vulnerability dubbed Fortinet2Shell with a CVSS score of 9.1, that allows unauthenticated remote code execution when a victim visits a malicious website. An origin-validation error involving a cross-origin resource sharing (CORS) misconfiguration lets attacker-controlled web pages communicate with a local service and execute attacker-supplied code. The issue affects specified FortiClient Mac, Windows, and Windows PAM releases in the 7.4 and 7.2 branches when FortiPAM functionality is enabled.
Organizations should identify affected installations and upgrade to the applicable fixed release: 7.4.8 or later or 7.2.15 or later. On Windows, a listener on TCP port 9191 and a running FortiVRS.exe process may indicate exposure, but neither establishes compromise. Fortinet reports no known exploitation and no available virtual patch, making deployment of the applicable software update the remediation priority.